
 #1
API testing, fuzzing, schema validation, authentication testing, and gateway security tools.
Kitploit recommended
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 openpcc/openpcc
An open-source framework for verifiably private AI inference
 lsh123/xmlsec
XML Security Library
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 undeadsec/swaggerspy
Automated OSINT tool that scans SwaggerHub API documentation to discover exposed secrets, credentials, and sensitive information using regex-based…
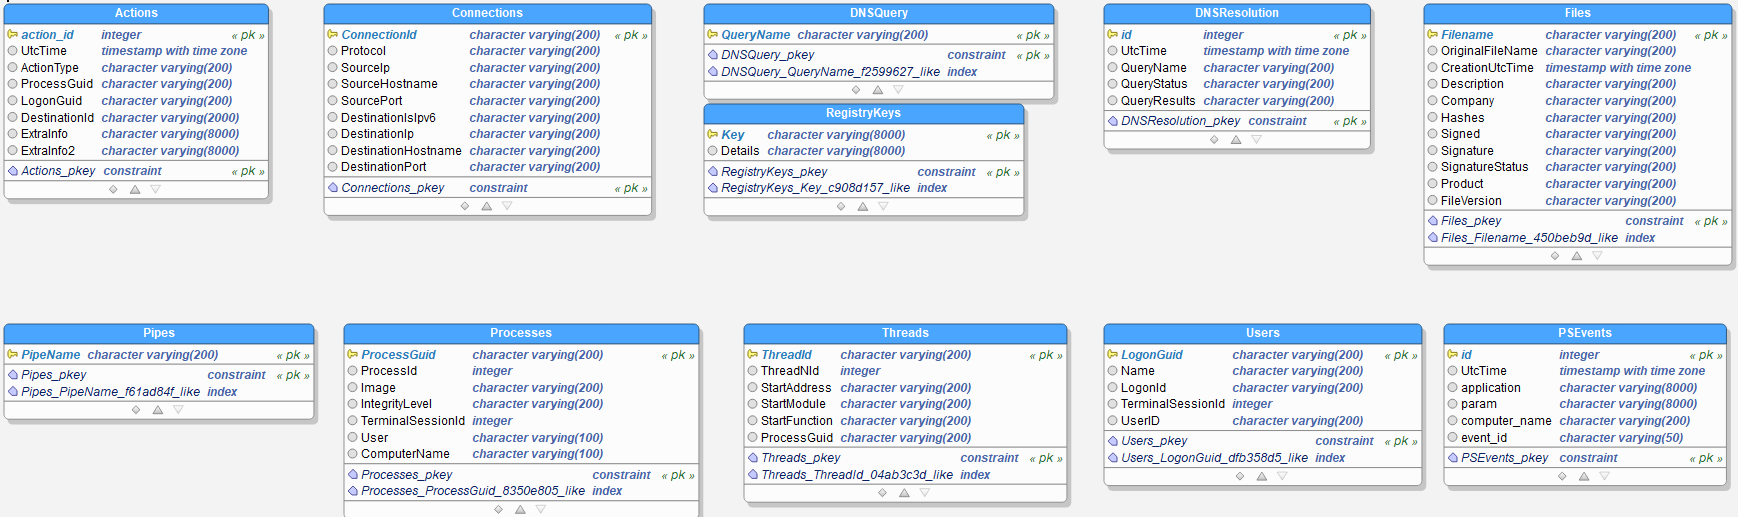 lucky-luk3/grafiki
Threat Hunting tool about Sysmon and graphs
 sentrypeer/sentrypeer
Distributed SIP honeypot that detects and shares fraud data on VoIP attacks. Collects bad actor IPs and phone numbers via peer-to-peer network, with…
 nicholasaleks/graphql-threat-matrix
GraphQL threat framework used by security professionals to research security gaps in GraphQL implementations
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
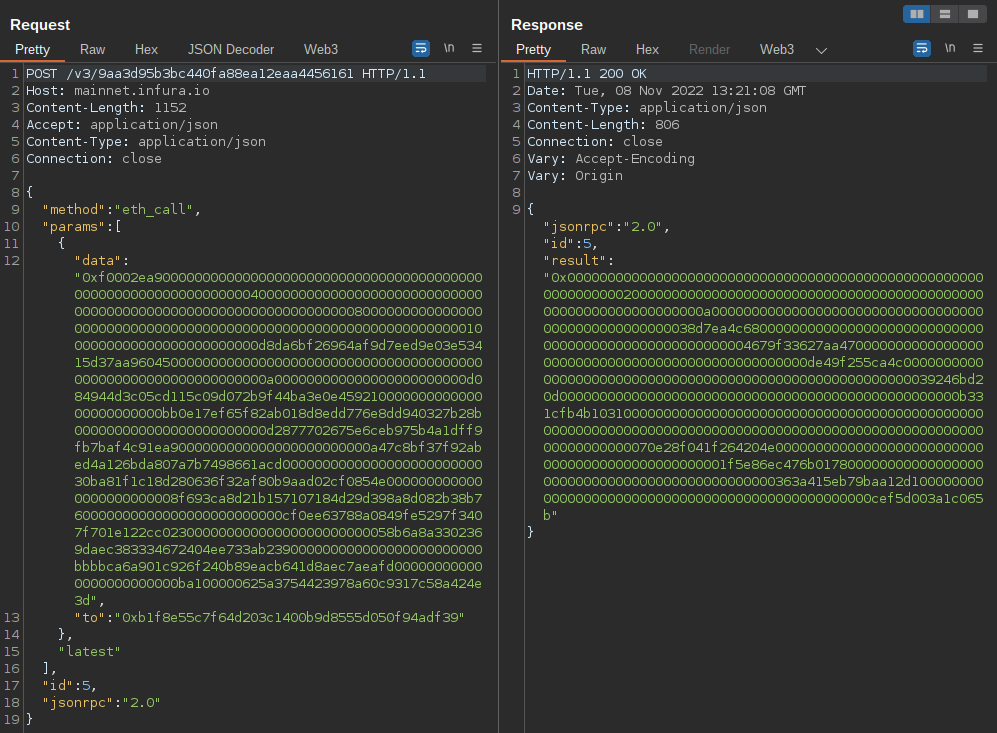 uwctcjnwlk/web3-decoder
Burp Suite extension for decoding Ethereum JSON-RPC calls and smart contract interactions, supporting multiple chains and automatic ABI retrieval.
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 vulncheck-oss/cli
VulnCheck's official command line tool







