
 #1
API testing, fuzzing, schema validation, authentication testing, and gateway security tools.
Kitploit recommended

 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
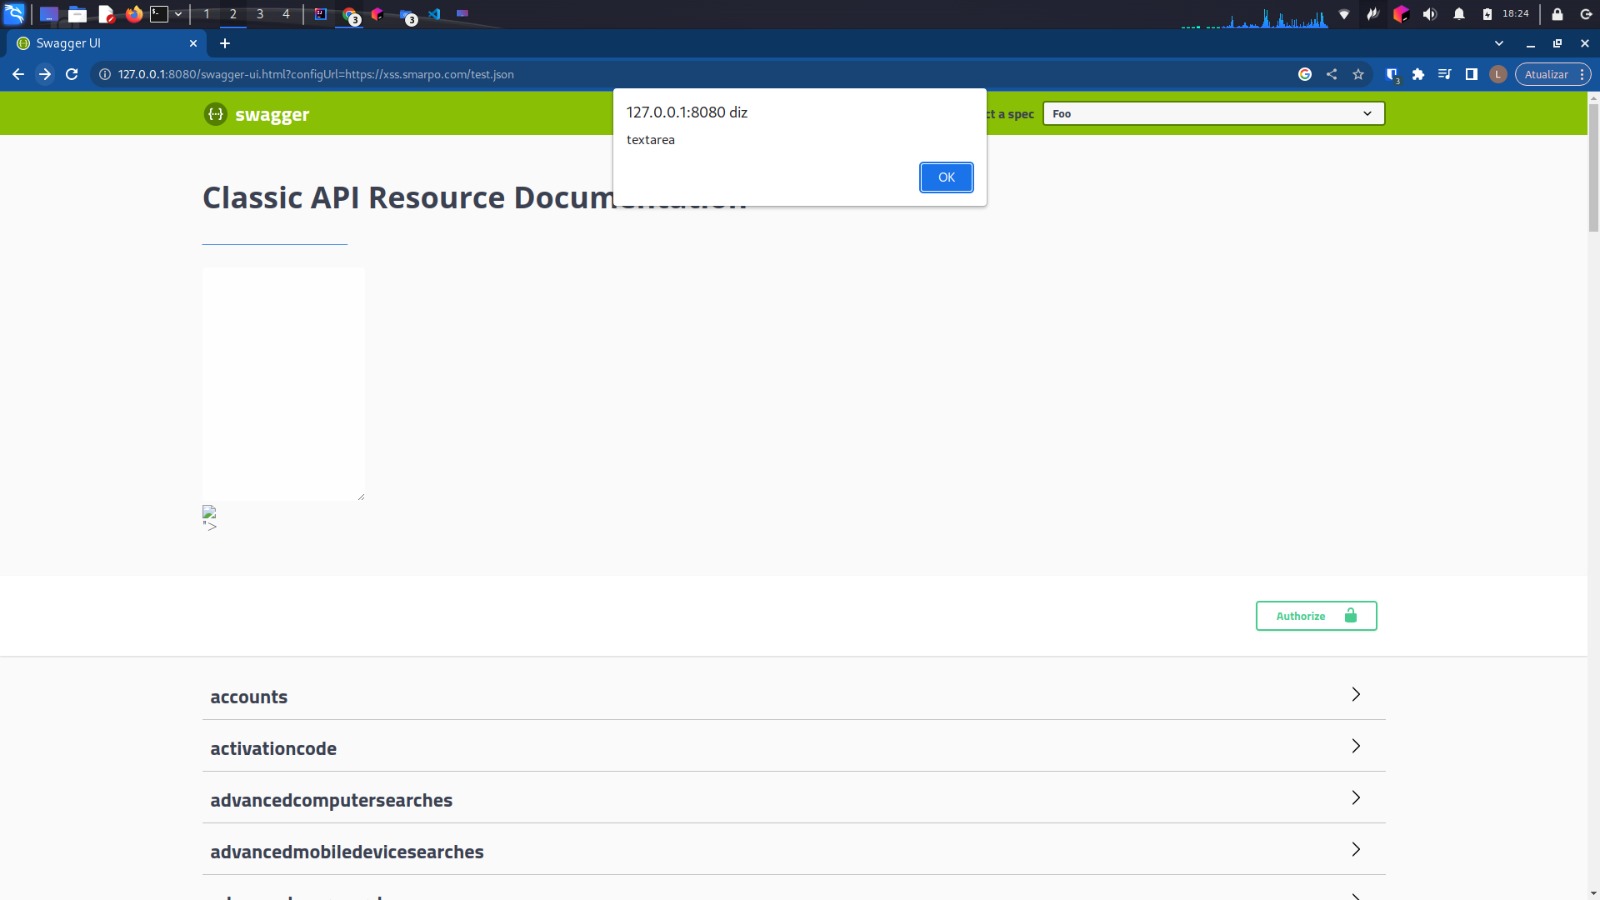 lucasrenaa/cve-2018-25031
Python-based proof-of-concept script demonstrating CVE-2018-25031 XSS vulnerability in Swagger UI using Selenium for automated detection across…
 nbs-system/naxsi
NAXSI is an open-source, high performance, low rules maintenance WAF for NGINX
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 jzheaux/cve-2023-34035-mitigations
Demonstrates CVE-2023-34035 vulnerability in Spring Security with vulnerable and mitigated sample applications, teaching proper servlet mapping and…
 randomrobbiebf/cve-2022-45354
Download Monitor <= 4.7.60 - Sensitive Information Exposure via REST API
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 mx-moth/flask-saml2
Flask library for building SAML Service Providers and Identity Providers
 cloudgraphdev/cli
The universal GraphQL API and CSPM tool for AWS, Azure, GCP, K8s, and tencent.
 randomrobbiebf/super-secret-finder
Burp Plugin for Secret Matching
 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 vagnerd/cve-2023-27587-poc
The simple PoC of CVE-2023-27587
 al1ex/alibab-nacos-unauthorized-reset-pwd
Alibab-Nacos-Unauthorized-Reset PWD
 vulnmachines/joomla_cve-2023-23752
Joomla! 4.0.0 through 4.2.7. An improper access check allows unauthorized access to webservice endpoints.

 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
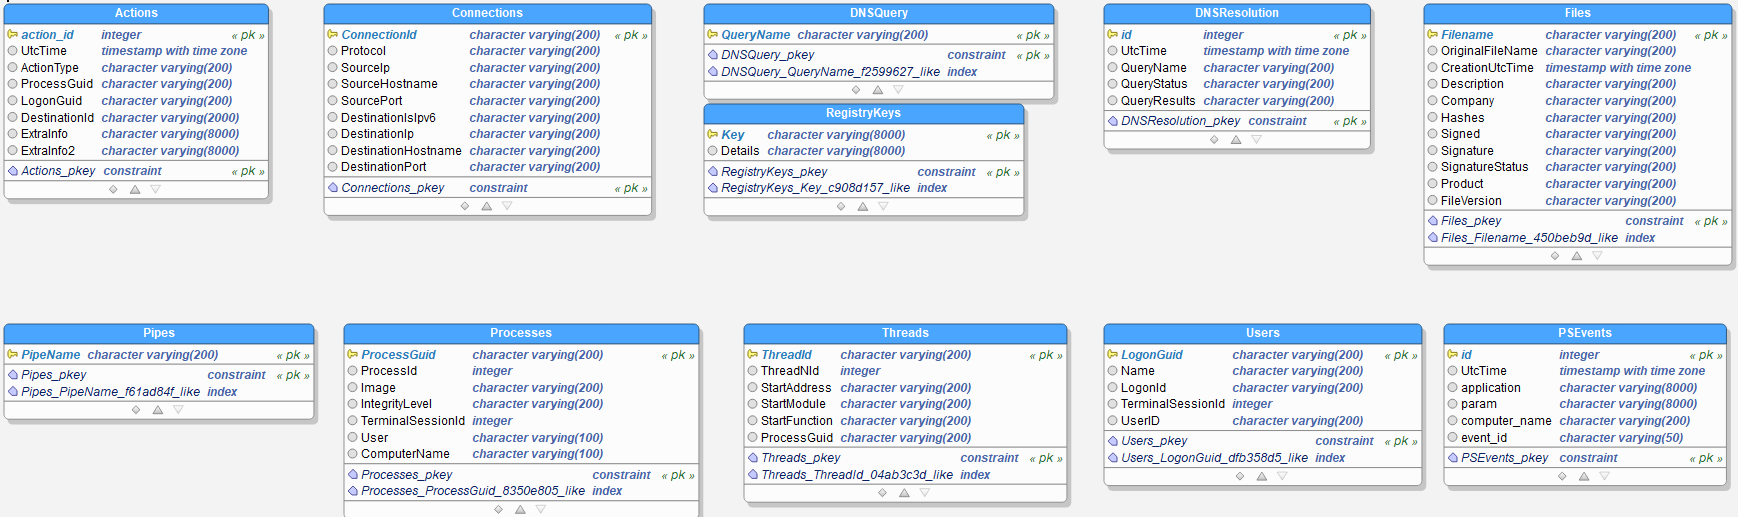 lucky-luk3/grafiki
Threat Hunting tool about Sysmon and graphs
 acczdy/cve-2022-24112_poc
CVE-2022-24112_POC








