#1
Behavioral anomaly detection, outlier analysis, UEBA, and statistical threat detection tools.
Kitploit recommended
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 delvelabs/batea
AI-based, context-driven network device ranking
 jazbengu/threatdetect
Streamlit-based insider threat detection prototype using XGBoost and Isolation Forest to analyze employee activity data, generate risk summaries, and…
 reyjesusq/sentinel-mcp
Autonomous AI-powered cyber defense system using MCP, Gemini 2.0 Flash, Dynatrace observability and MongoDB. Google Cloud Hackathon submission.
 roxanne_ardary/nexora
AI-driven endpoint governance platform that monitors software usage, applies deterministic policy-based risk classification, and generates structured…
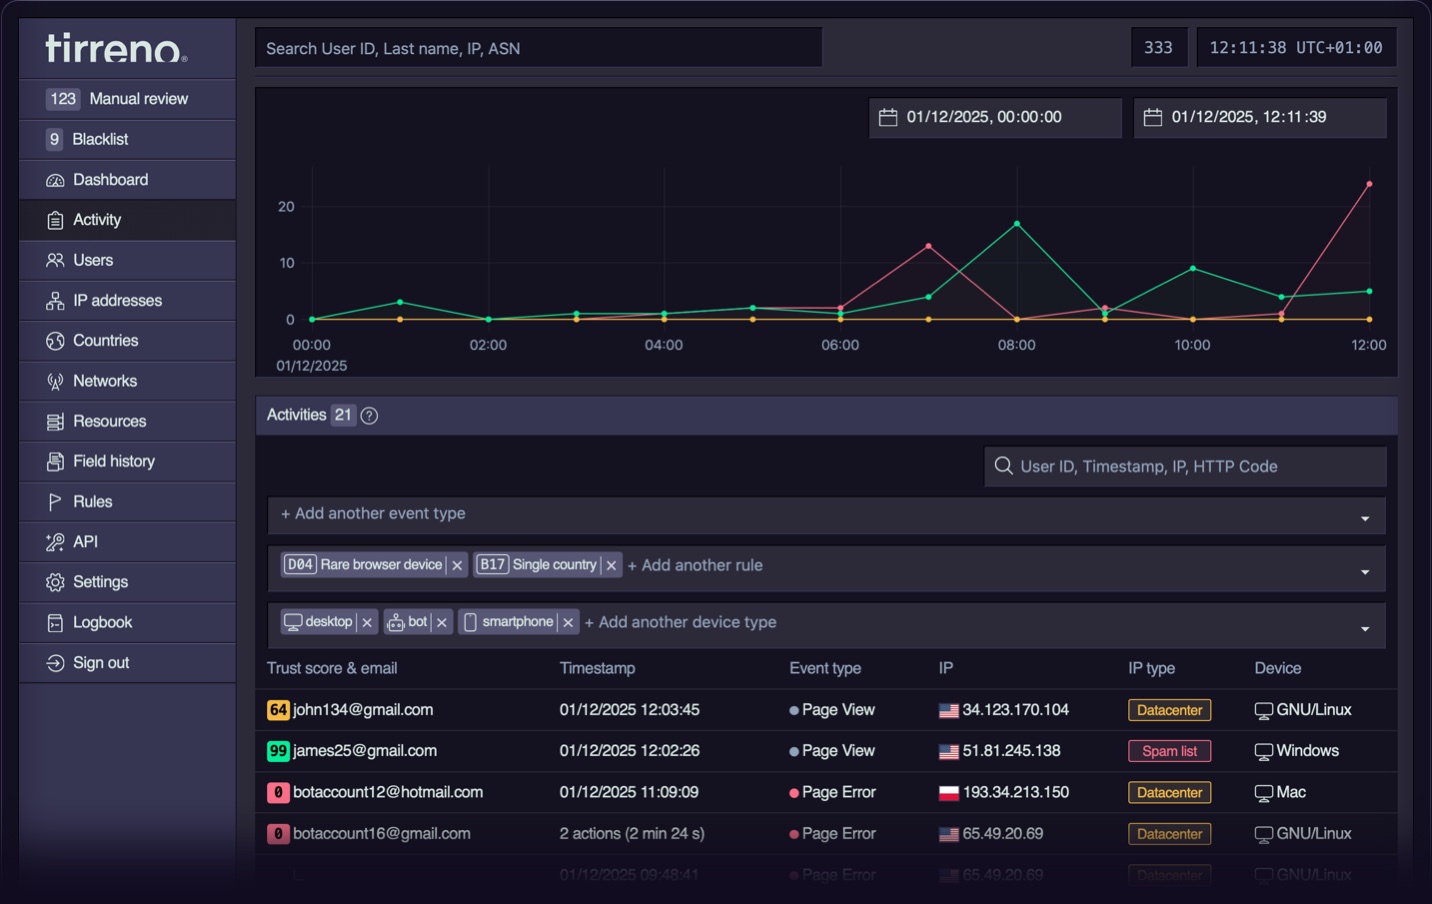 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 protectai/rebuff
Multi-layered prompt injection detector for AI applications using heuristics, LLM-based analysis, vectorDB attack signatures, and canary token leak…
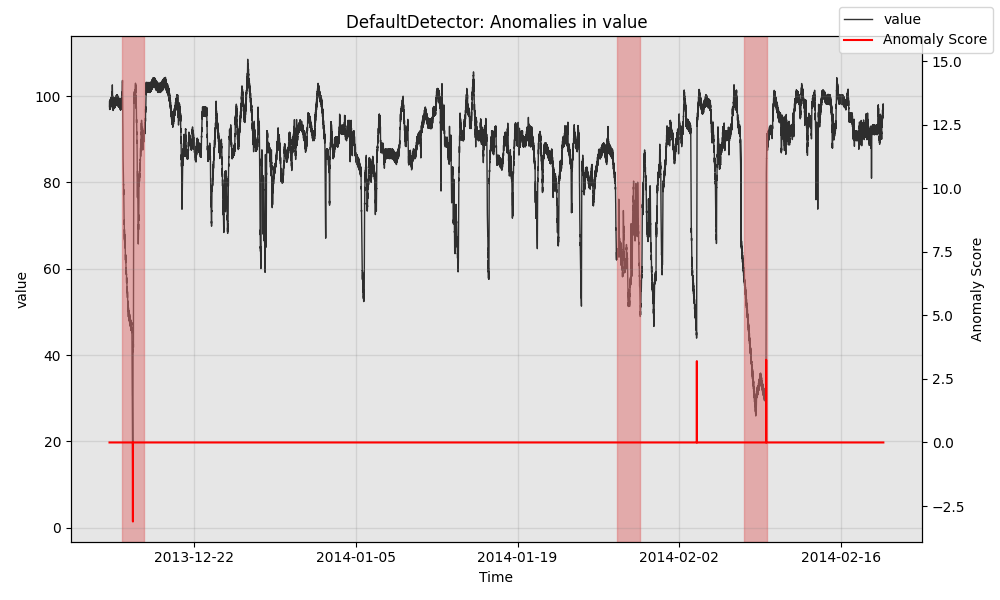 salesforce/merlion
End-to-end Python framework for time series intelligence, offering anomaly detection, forecasting, change point detection, AutoML, ensembles, and…
 fusion1110/ebpf-hid_guard
Linux kernel-space HID injection attack detector using eBPF. Monitors USB and Bluetooth HID devices for anomalous keystroke timing and automatically…