#1
Behavioral anomaly detection, outlier analysis, UEBA, and statistical threat detection tools.
Kitploit recommended
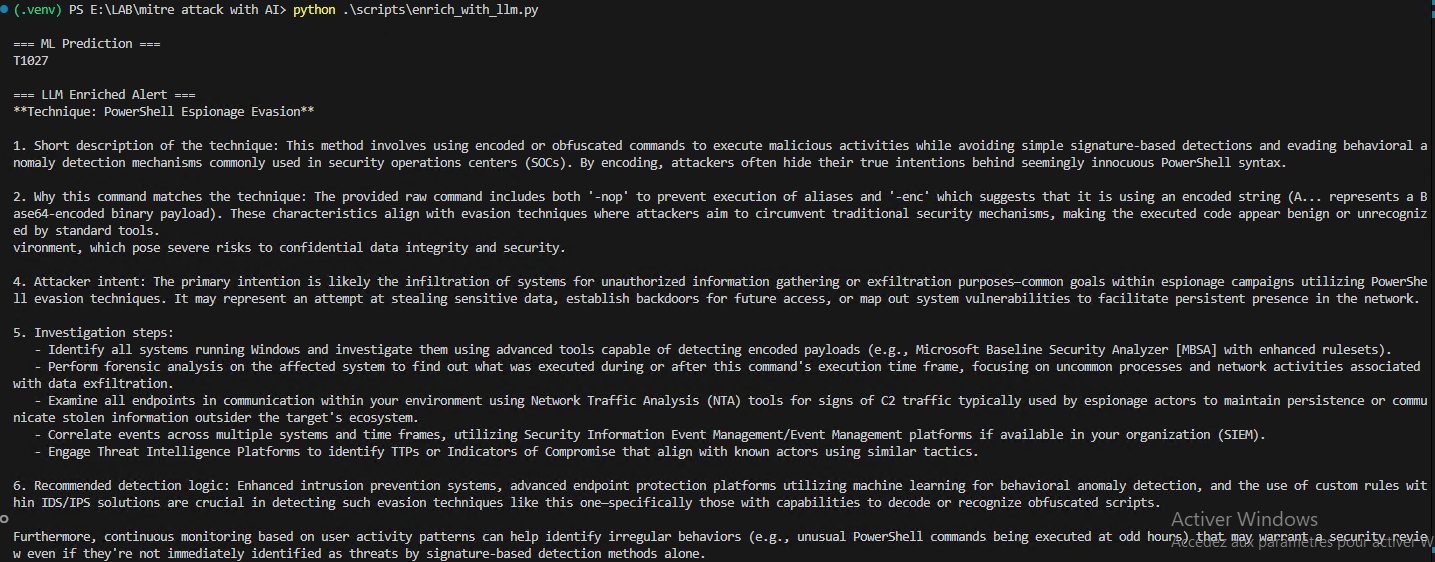
 mouna23/ai-driven-mitre-attack
This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.
 anecdotes-yair/trust-my-agent-ai
Security & Compliance bodyguard for OpenClaw agents
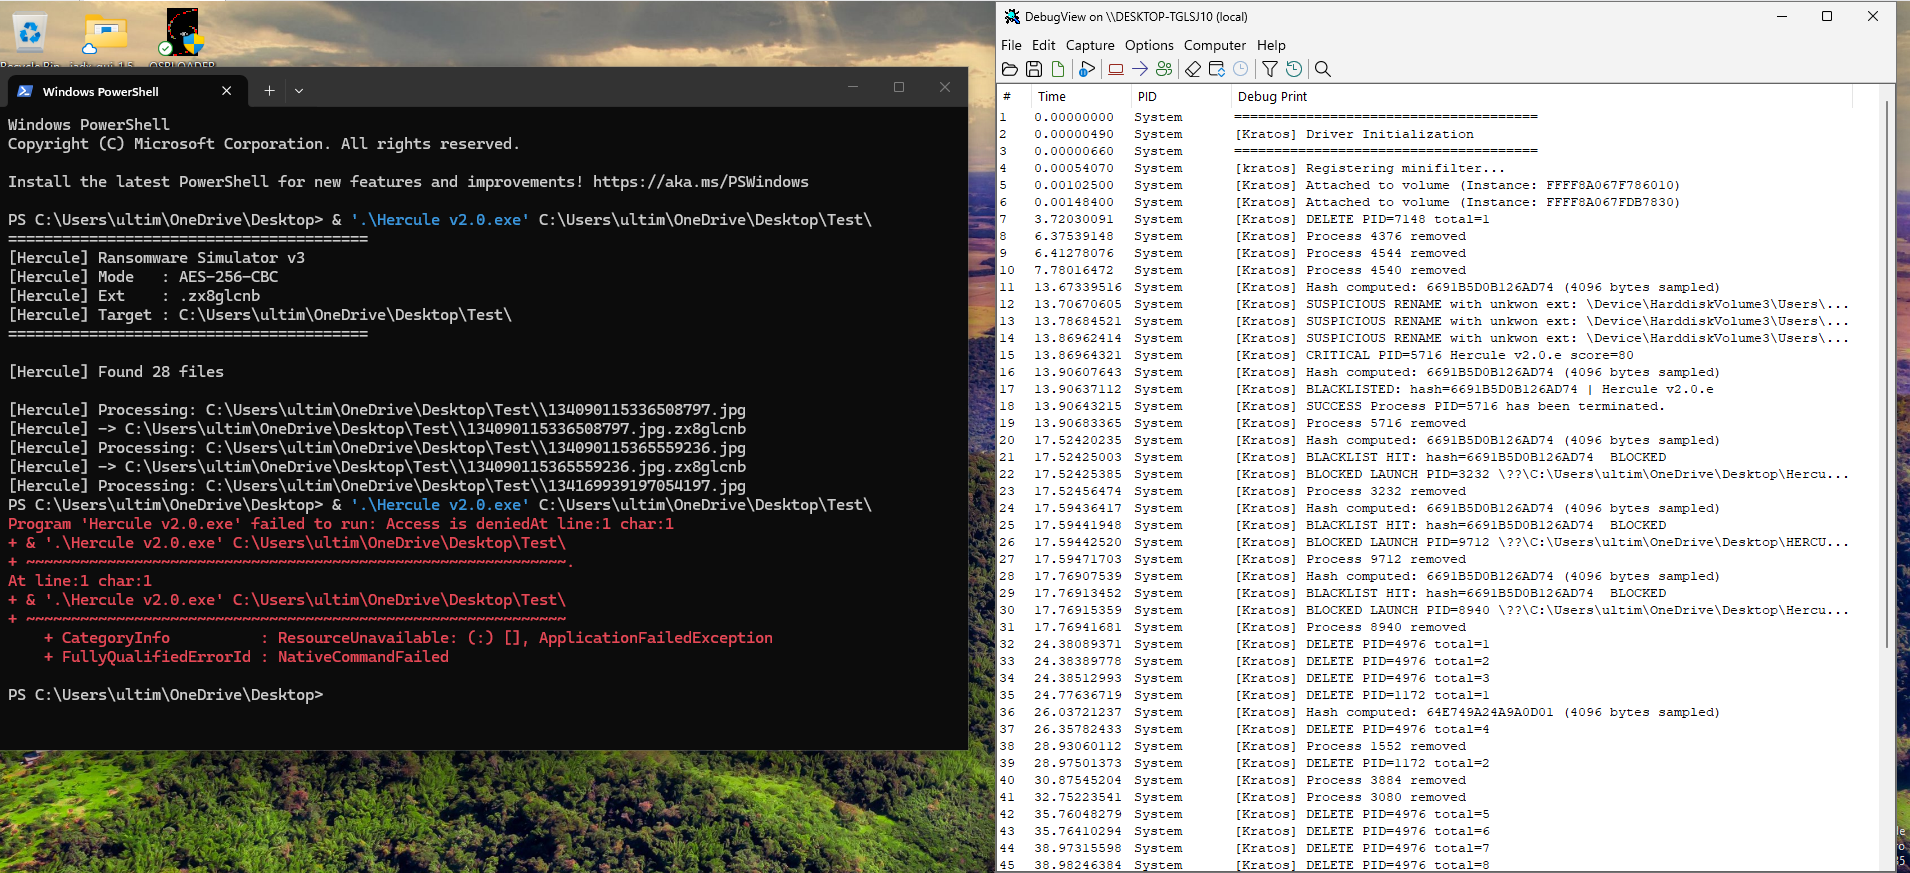 mukendi/kratosminifilter
Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize
 corelight/zeek-quasarrat-detector
Zeek detector for QuasarRat
 nccgroup/reactor
Runs custom filters on Elasticsearch and alerts on matches
 skac44/cve-2024-38063
Simulates CVE-2024-38063 TCP/IP remote code execution attack, captures network traffic with TShark, and trains a machine learning model to detect…
 pe3zx/crowdstrike-falcon-queries
A collection of Splunk's Search Processing Language (SPL) for Threat Hunting with CrowdStrike Falcon
 edoardottt/offensive-onos
My experiments in weaponizing ONOS applications (https://github.com/opennetworkinglab/onos)
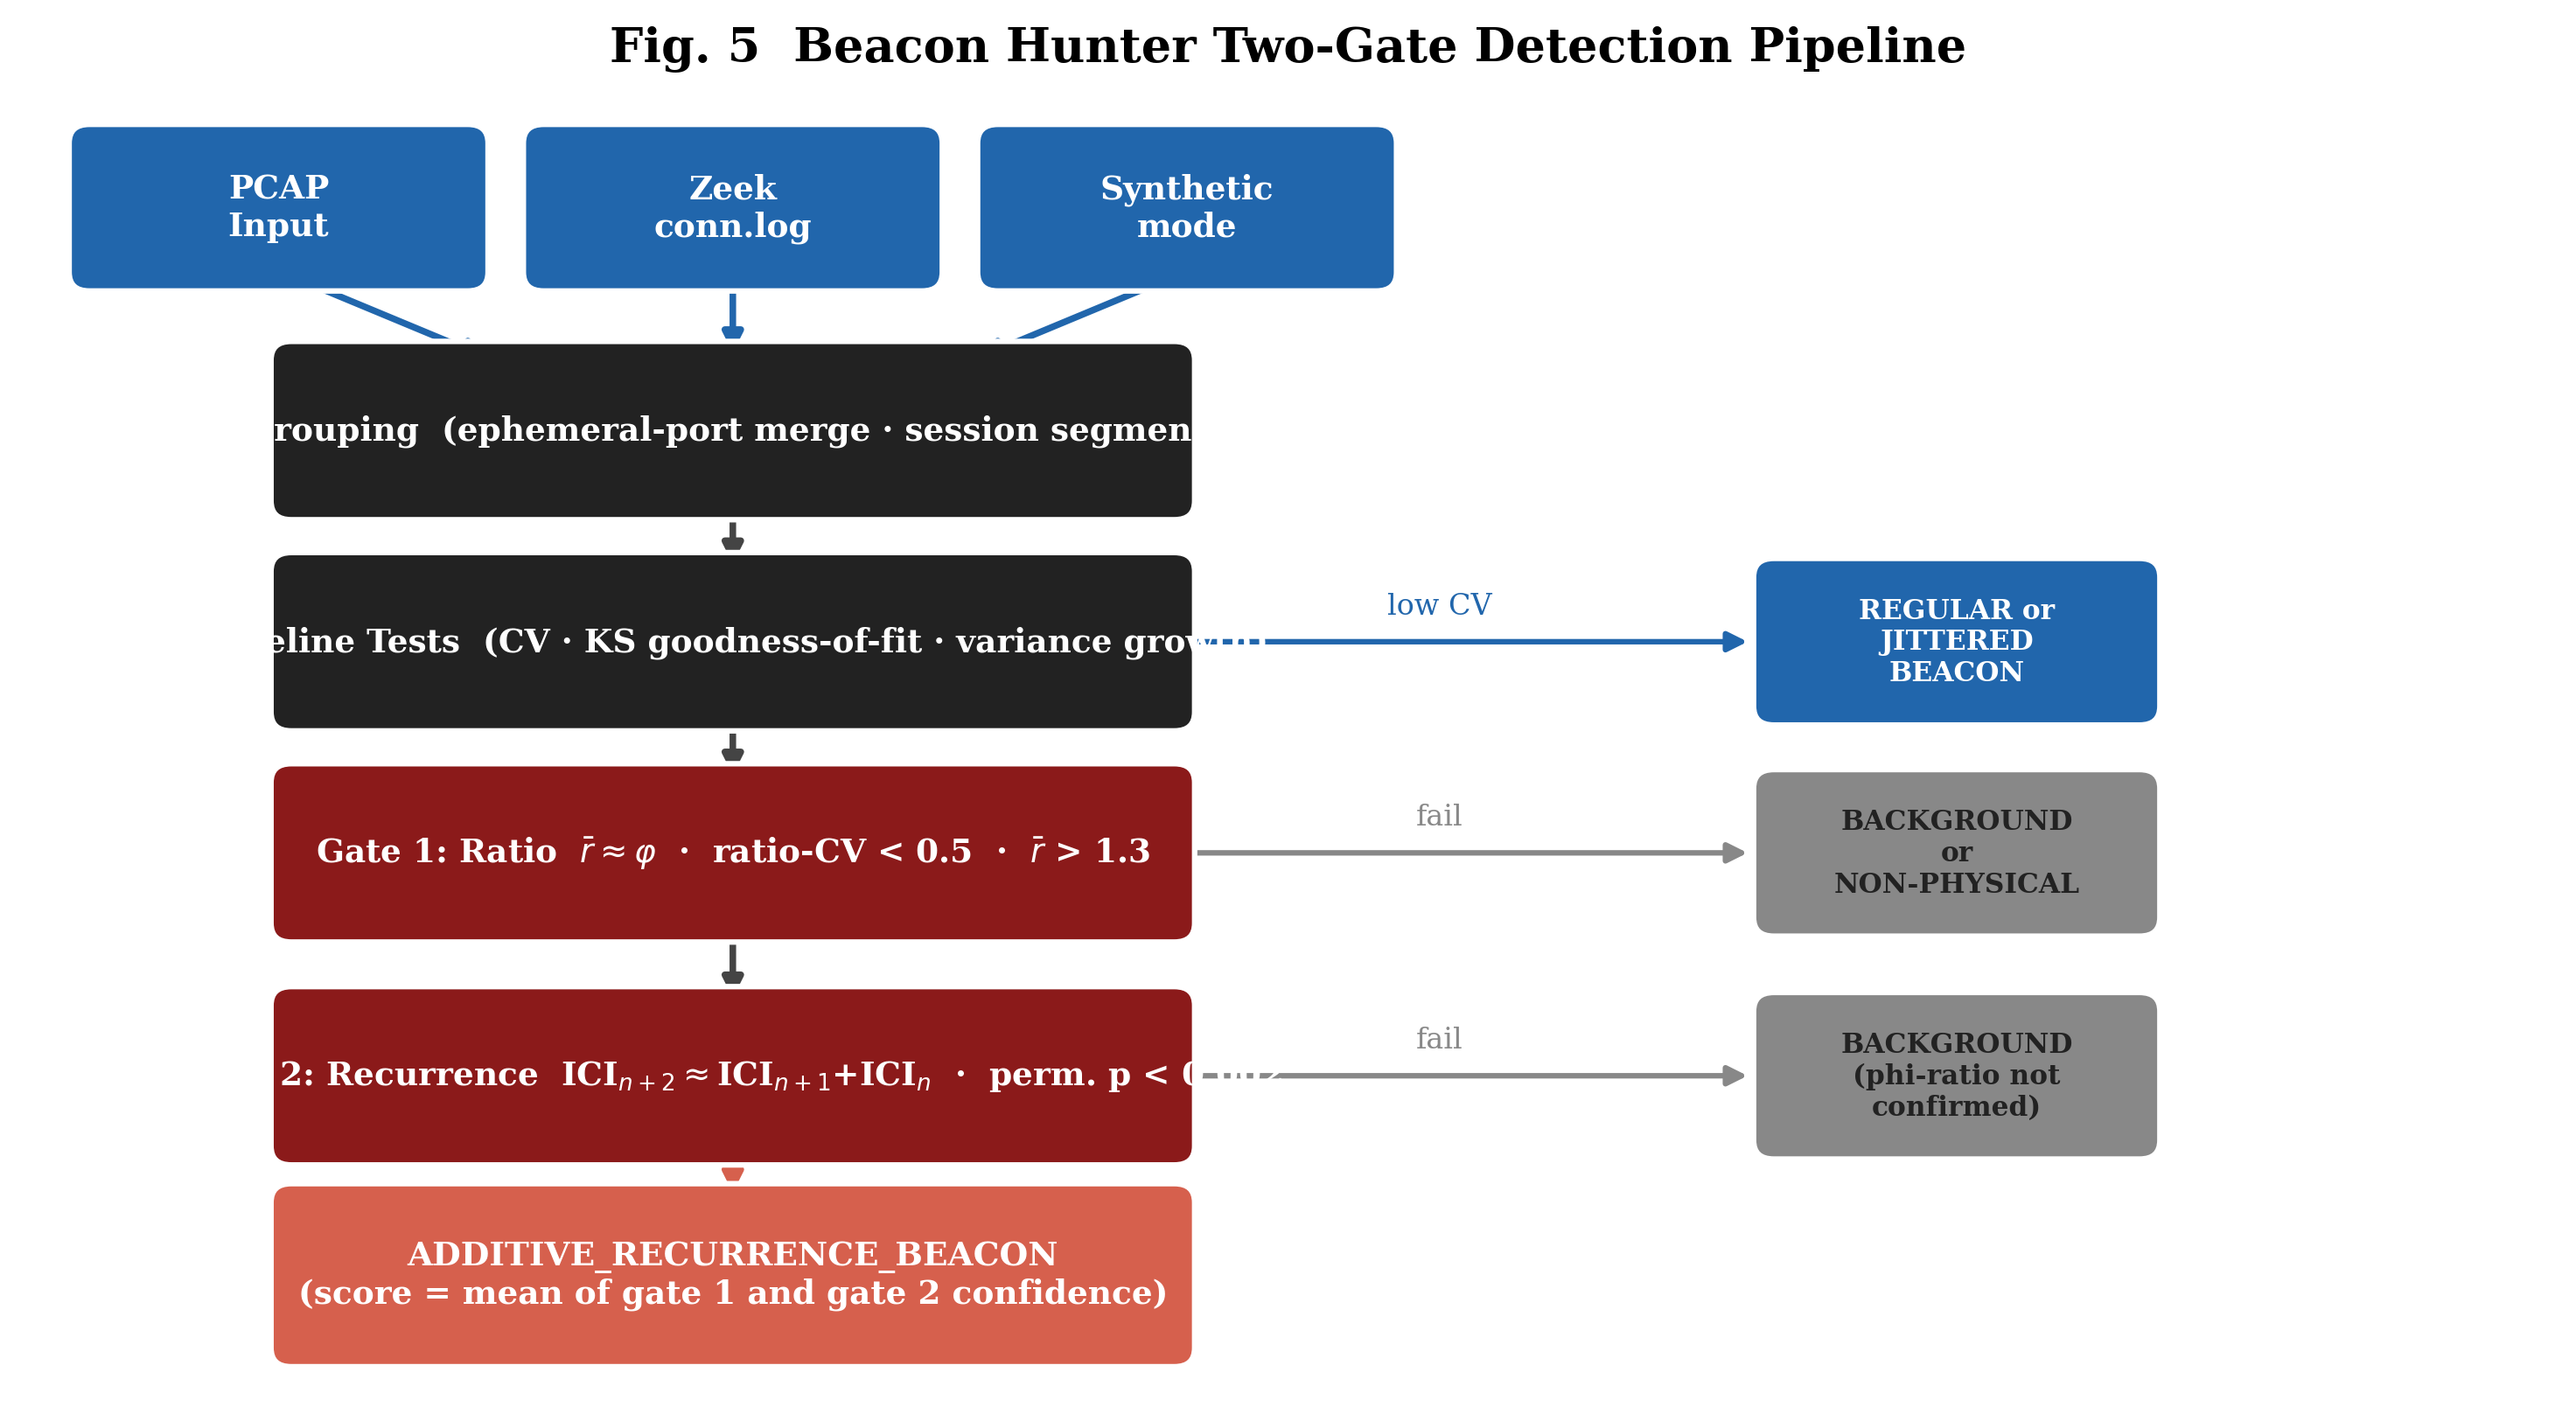 mrcord77/beacon-hunter
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors
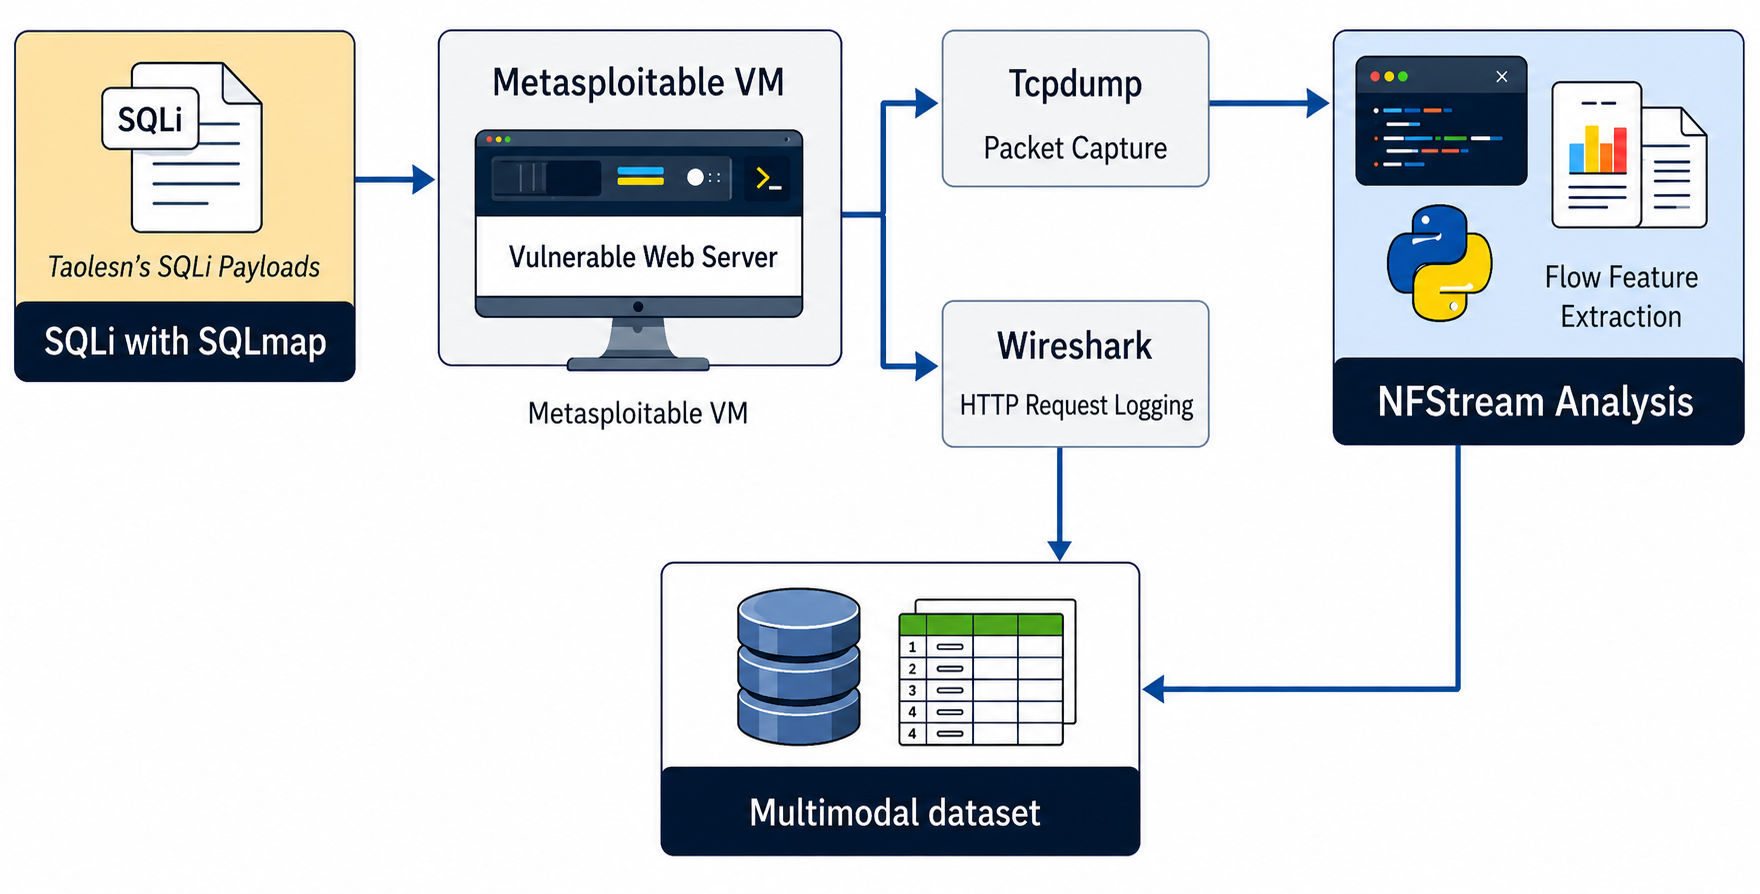 paul12345-cyber/multimodal-web-attack-dataset
This repository hosts a multimodal web attack dataset (MWAD) to advance AI-driven threat detection research.
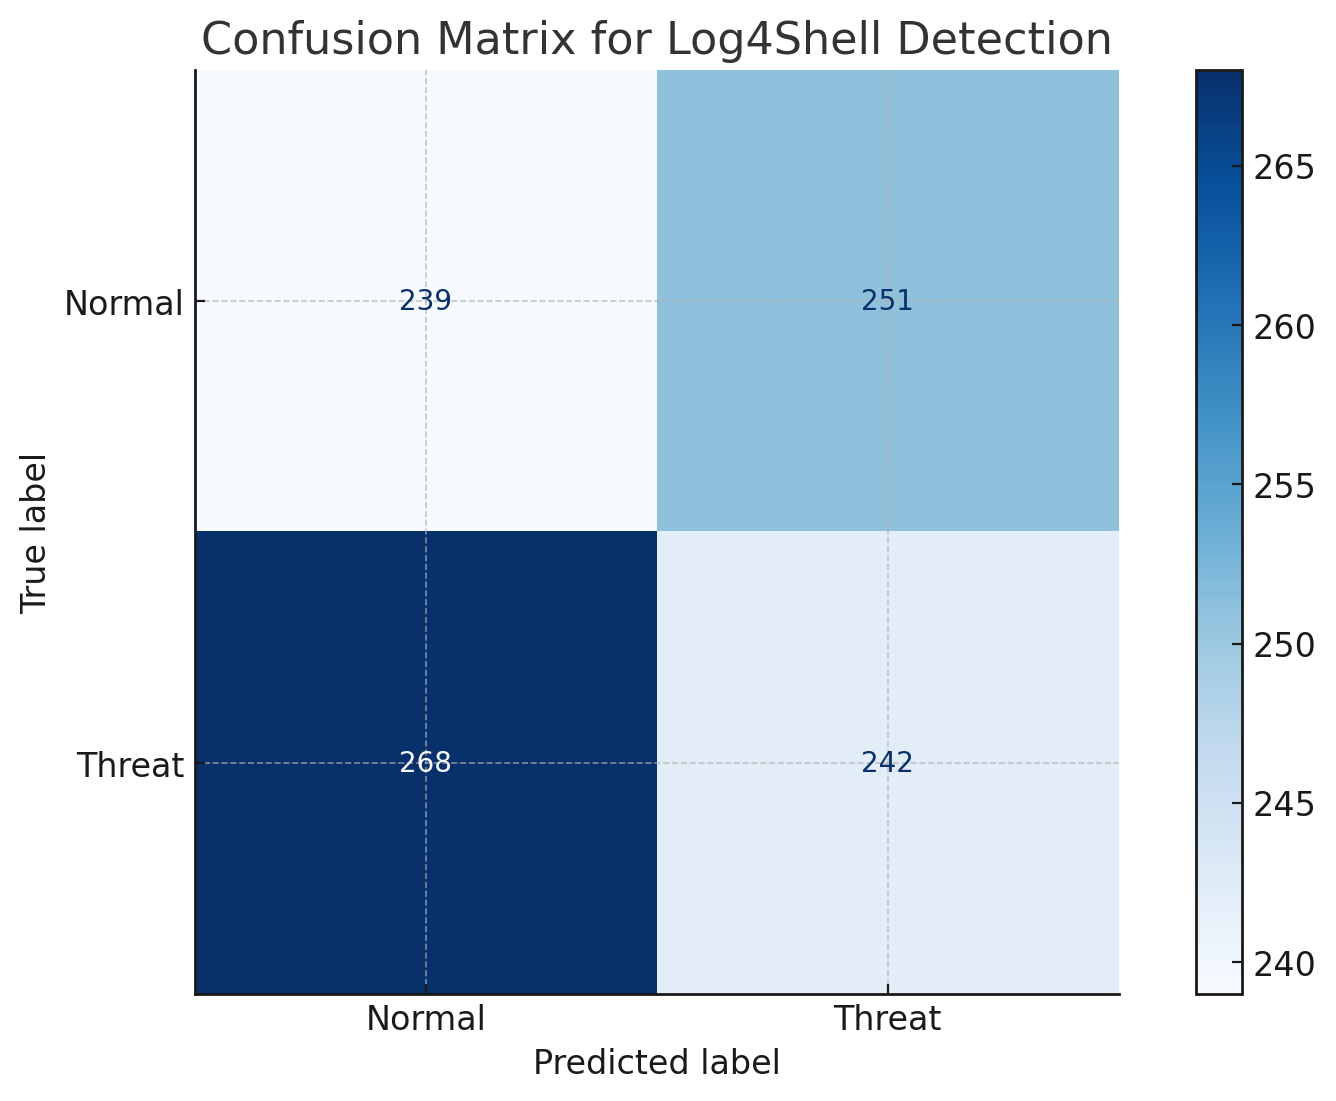 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…
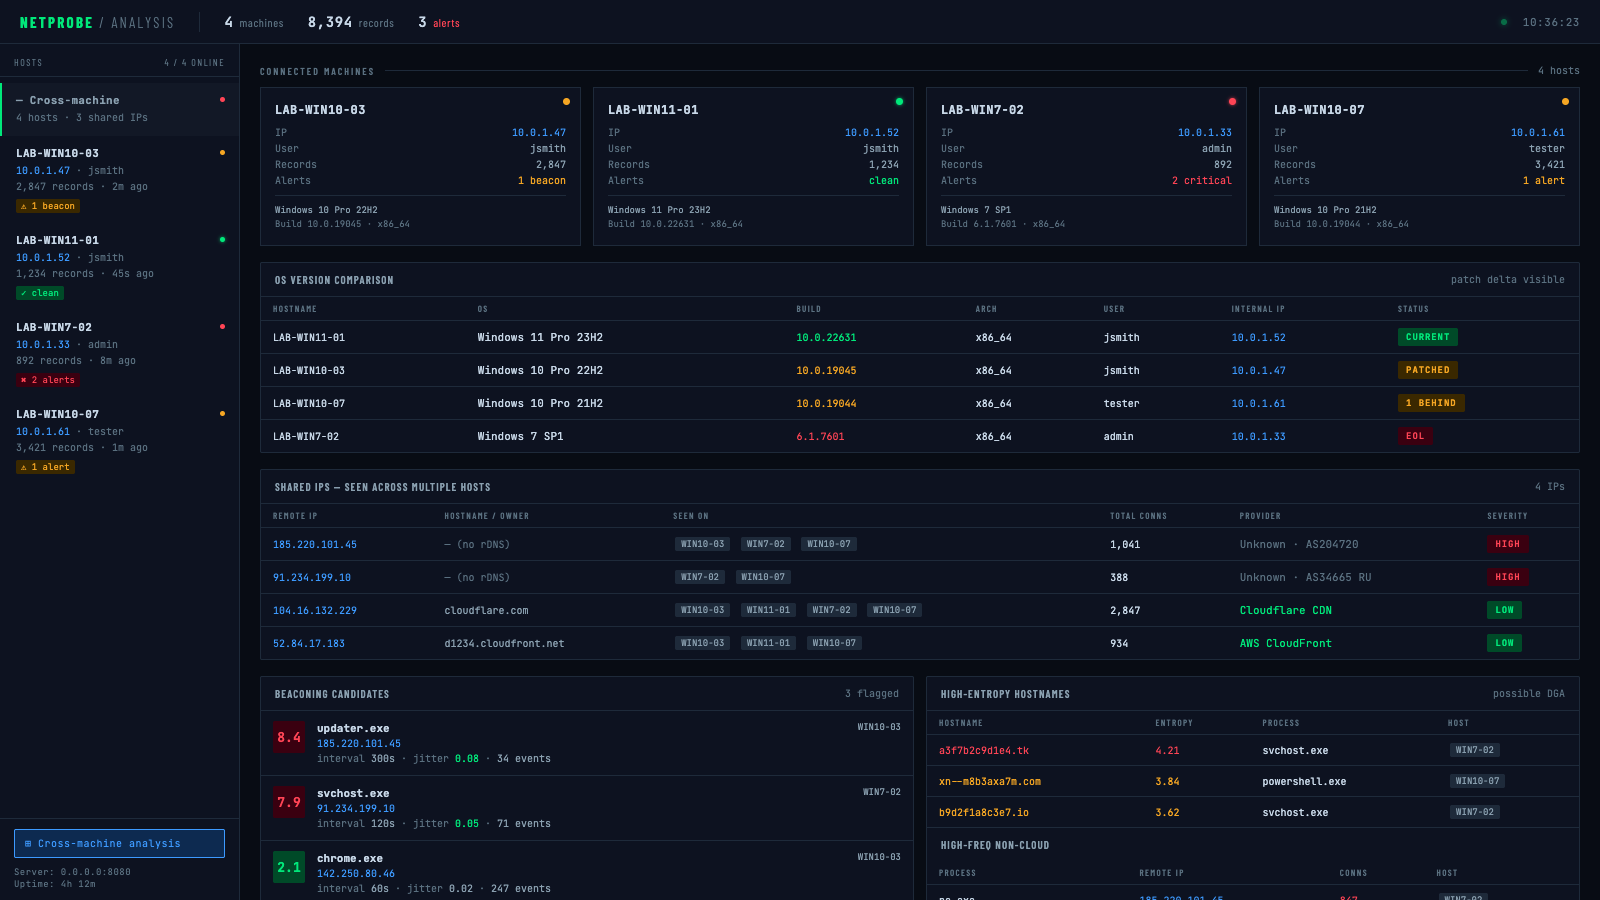
 hackinglz/gibson
Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity
 kennbroorg/poorskeme
OSINT - Data Visualization - Blockchain - Awareness - Scam
 ait-aecid/rootkit-detection-ebpf-time-trace
Detection of rootkit file hiding activities through analysis of shifts in kernel function execution times.