
 #1
Tools focused on penetration testing, reversing, and securing Android apps and the Android OS.
Kitploit recommended
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.
 nanopathi/system_bt_aosp10_r33_cve-2020-0463
Android Bluetooth stack (Fluoride) with a fix for CVE-2020-0463, enabling security analysis and exploitation testing of Bluetooth vulnerabilities on…
 satheesh575555/system_bt_aosp10_r33-cve-2020-0138
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2020-0138, addressing a critical vulnerability in the Bluetooth component.
 trinadh465/frameworks_base_cve-2022-20493
Android framework base repository containing patches or analysis for CVE-2022-20493, addressing a security vulnerability in the Android platform.
 shaikusaf/system_bt_aosp10_r33_cve-2022-20224
AOSP Bluetooth stack repository modified to address CVE-2022-20224, providing a patched version of the Fluoride Bluetooth stack for Android 10.
 pazhanivel07/system_bt_a10-r33_cve-2021-0474
Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0435
AOSP Bluetooth stack repository modified for CVE-2021-0435, providing a patched or vulnerable version for analysis and testing of Bluetooth…
 shaikusaf/system_bt_aosp10_r33_cve-2020-0380
AOSP Bluetooth stack (Fluoride) with a patch for CVE-2020-0380, enabling analysis and testing of Bluetooth vulnerabilities on Android 10.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0431, enabling analysis and testing of Bluetooth vulnerabilities in AOSP 10.
 nanopathi/system_bt_aosp10_r33_cve-2021-0522
Android Bluetooth stack (system/bt) source code including patch for CVE-2021-0522 privilege escalation vulnerability.
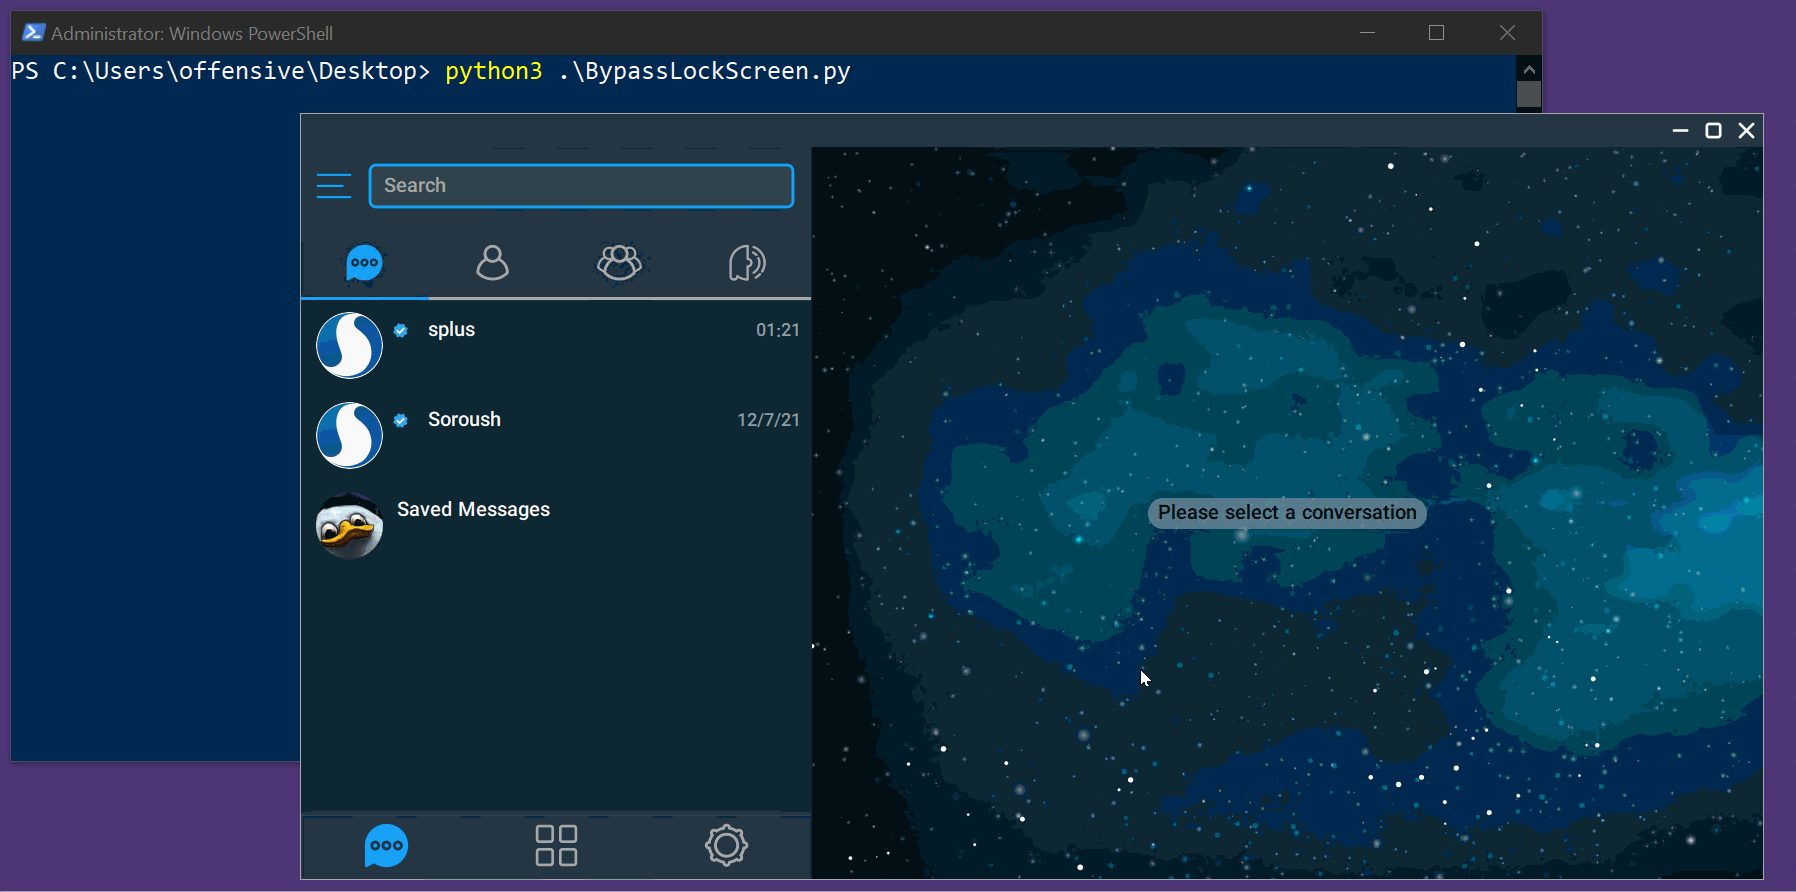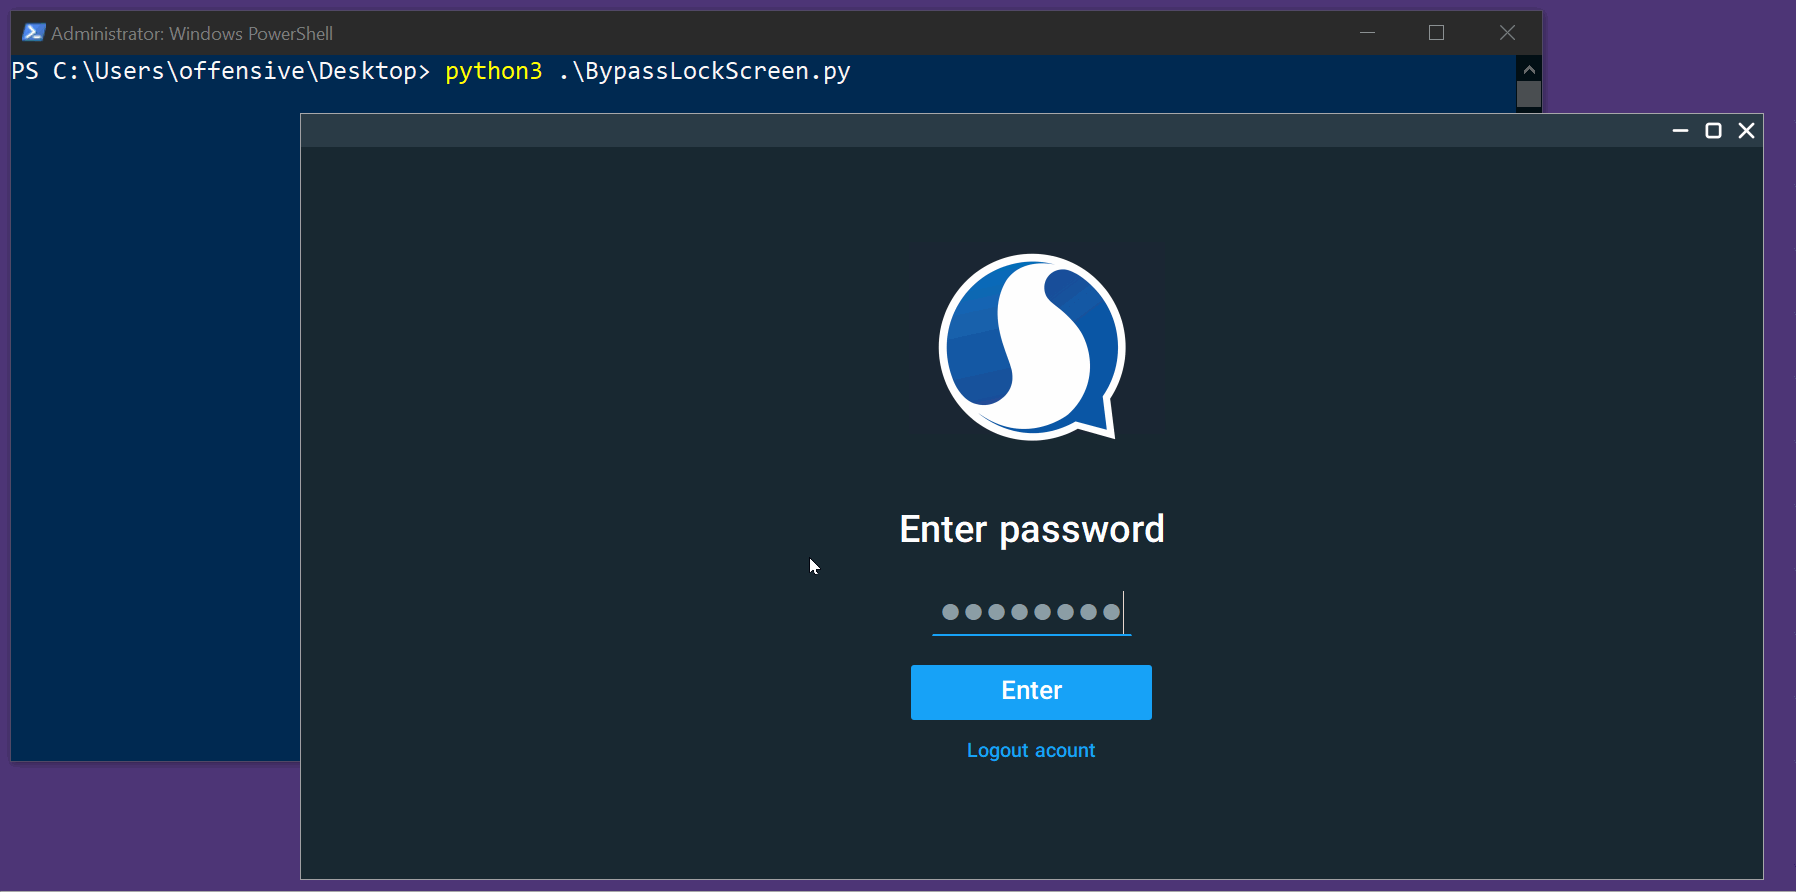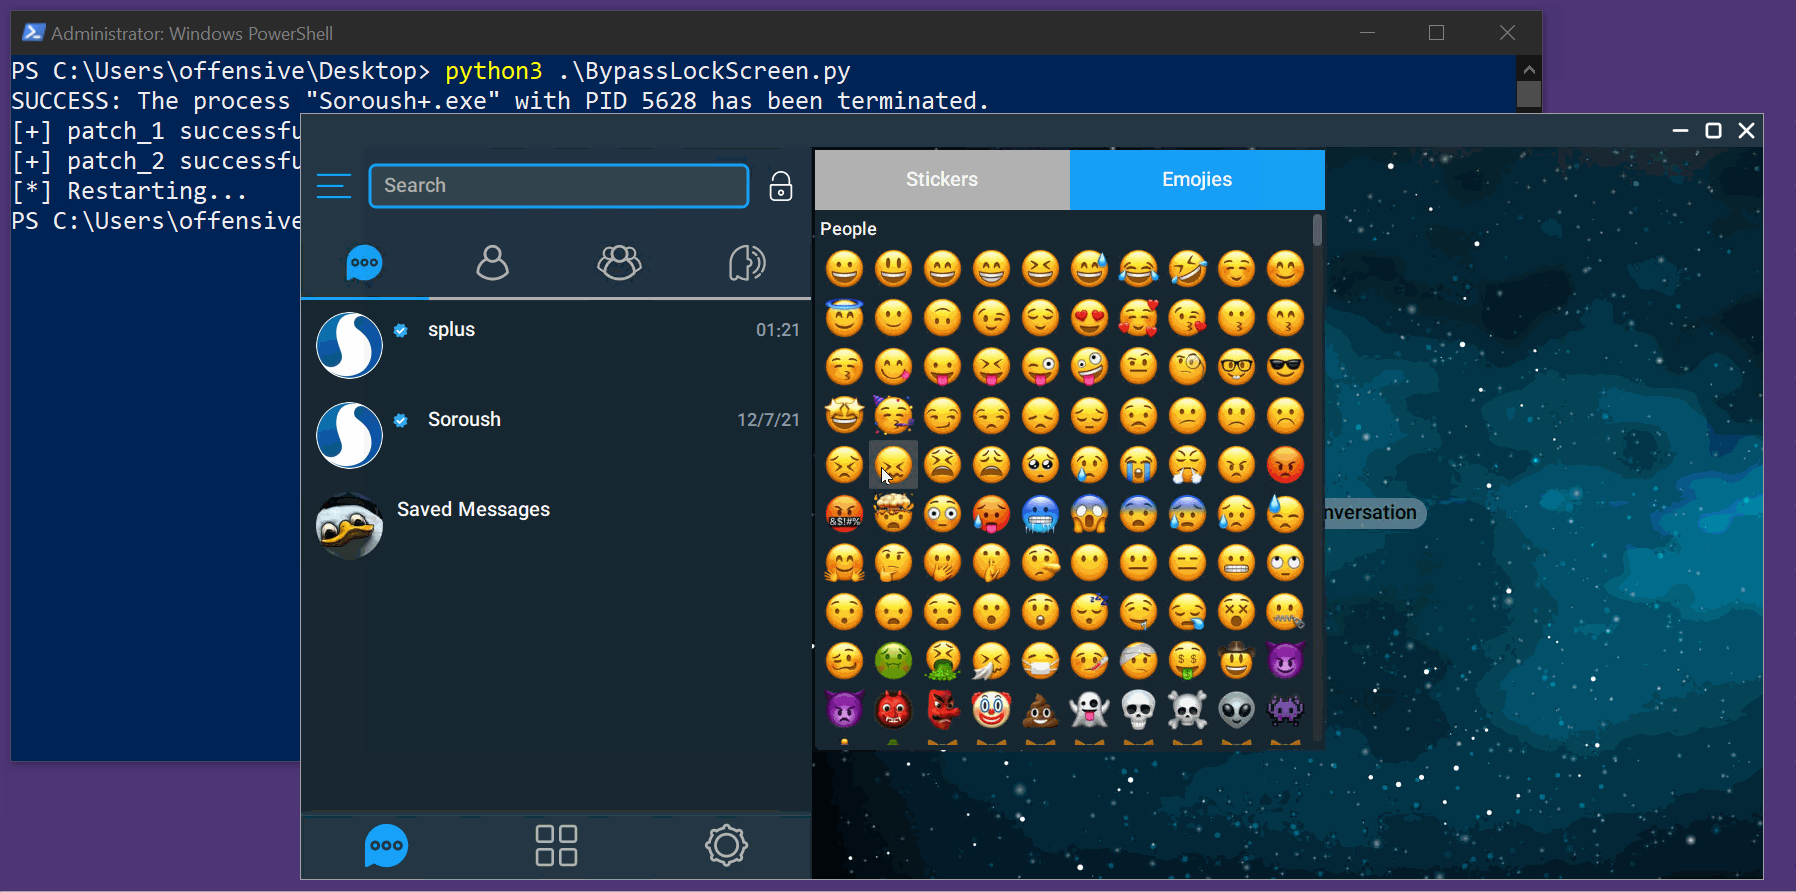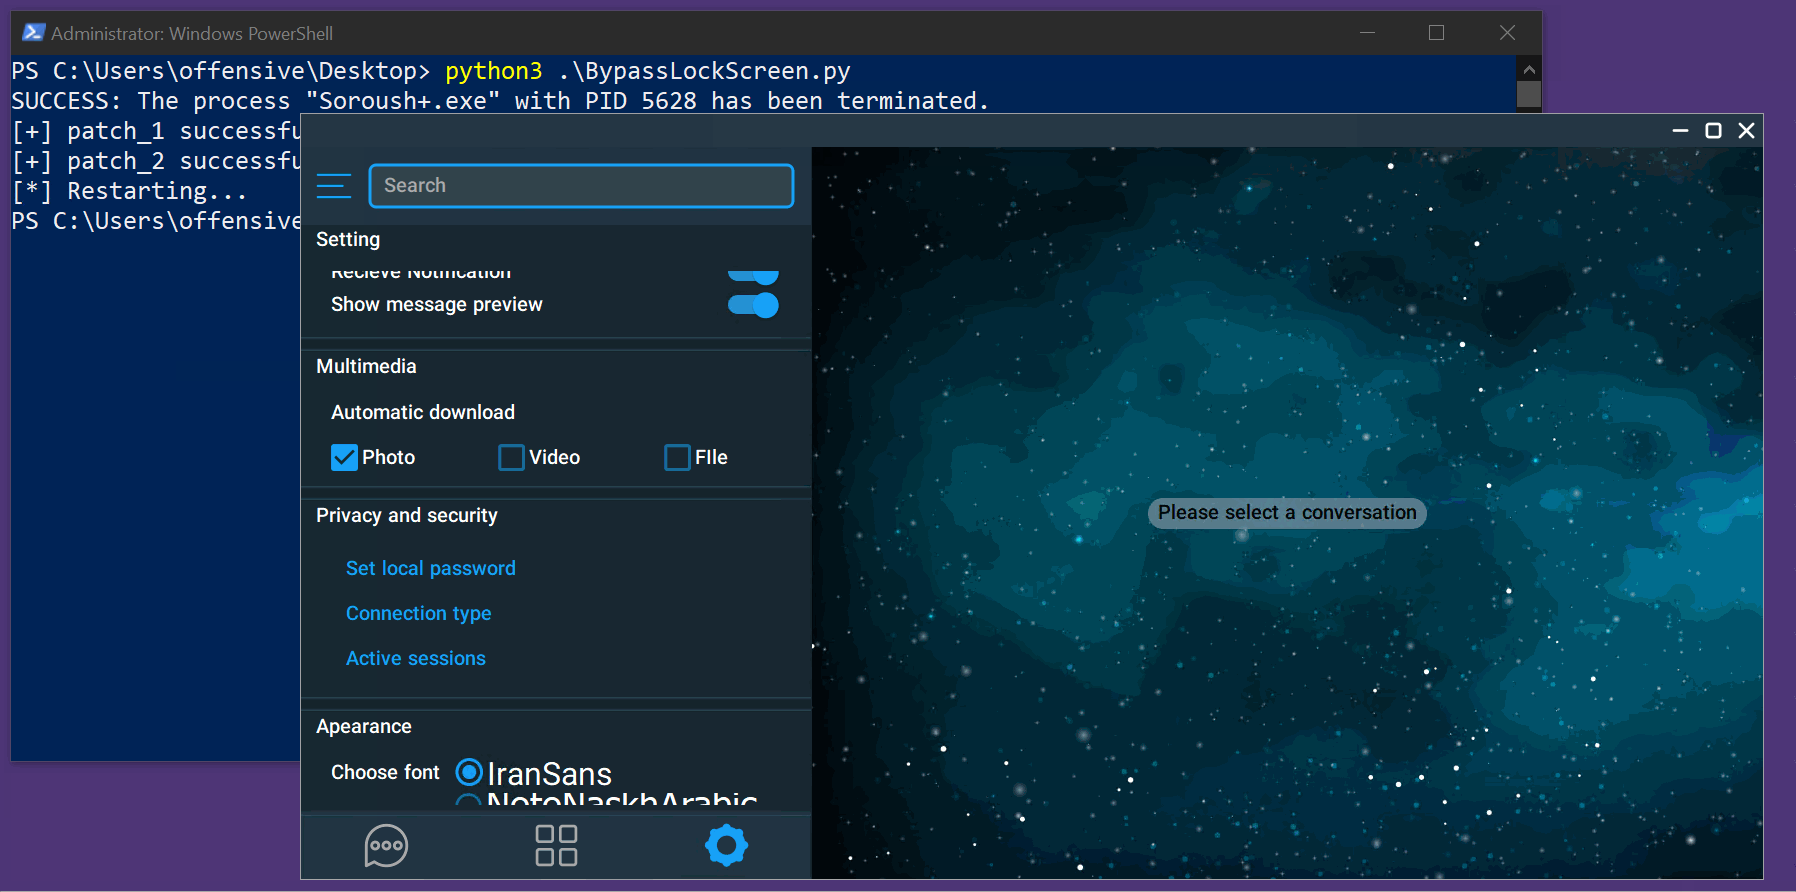 scopion/cve-2022-26629
PoC exploit for CVE-2022-26629: bypasses the lock screen on SoroushPlus+ Messenger 1.0.30 via improper access control. Includes an auto-exploit…
 pazhanivel07/system_bt_a10_r33_cve-2021-0474
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0474, providing source code for building and testing the Bluetooth component on…
 mazx0p/cve-2014-8609-poc
pendingintent vulnerability
 sumeetit/cve-2022-20607
In the Pixel cellular firmware, there is a possible out of bounds write due to a missing bounds check. This could lead to remote code execution with…
 abrarkhan/g3_frameworks_av_cve-2024-0023
Proof-of-concept exploit for CVE-2024-0023 in Android's frameworks/av, implemented in C++ to demonstrate the media framework vulnerability.
 shinycolumn/cve-2025-50944
Improper Certificate Chain Validation in EagleEyes Lite Android Application
 shaikusaf/frameworks_base_aosp10_r33_cve-2021-0334
Android framework base repository for AOSP 10 R33, modified to address CVE-2021-0334, focusing on vulnerability analysis and exploitation.
 actuator/com.simplemobiletools.dialer
CVE-2023-49003








