Skip to content
KitploitKITPLOIT
أدواتعمليات الاستغلالالمدونة
Log in
إرسال
أدواتعمليات الاستغلالالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
bla — Hardens binaries, Electron ASAR, JS, WASM, Python, and model files against AI reverse-engineering agents using decoy metadata, budget exhaustion, and runtime-equivalent shields. | Kitploit
أدوات/GitHubGitHub/qybaihe/bla
Defensive ToolsReverse EngineeringScripting & AutomationMalware AnalysisMobile SecurityBinary AnalysisAnti-BotAI SecurityAdversarial Attack
GitHubqybaihe/bla

bla

Hardens binaries, Electron ASAR, JS, WASM, Python, and model files against AI reverse-engineering agents using decoy metadata, budget exhaustion, and runtime-equivalent shields.

6.3k783137منذ 11س 7دتمت المراجعة من قبل Kitploit
مشاركة
عرض المستودعالموقع الإلكتروني
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.

English · 简体中文 · 繁體中文 · 日本語 · 한국어 · Türkçe · Русский · Tiếng Việt · ไทย · Deutsch · Español · Français · Українська · Polski · Português (Brasil) · العربية · فارسی · Bahasa Indonesia · Italiano · Ελληνικά · മലയാളം · Roman Urdu · Română

BLA Shield

BLA: Blind LLM Agents

Poison → Exhaust → Hallucinate. Make Reverse Engineering Bankrupt Again.

The open-source Counter-REA Blue Defense MCP & CLI that protects software releases against AI reverse-engineering agents (morluto/rea, autonomous decompilers, and LLM recon pipelines) — verified across 14 showcase benchmark targets.
npm version GitHub Trending MCP Server Formats Counter-REA MIT License

GitHub Trending — #5 Repository Of The Day

🌐 Official Website · 📖 Defense Guides · 📊 Live Benchmarks · 🎯 CrackMe Arena · 🏢 Enterprise · ⚖️ Disclaimer

Quick Start · How It Works · Empirical Results · Format Coverage · 14-Target Benchmark · CrackMe Arena · FAQ


[!IMPORTANT] Defensive Use Only: BLA is engineered strictly for software authors and security teams protecting their own intellectual property and release artifacts. See DISCLAIMER.md. Always install from official sources: qybaihe/bla or npm i bla-agents.
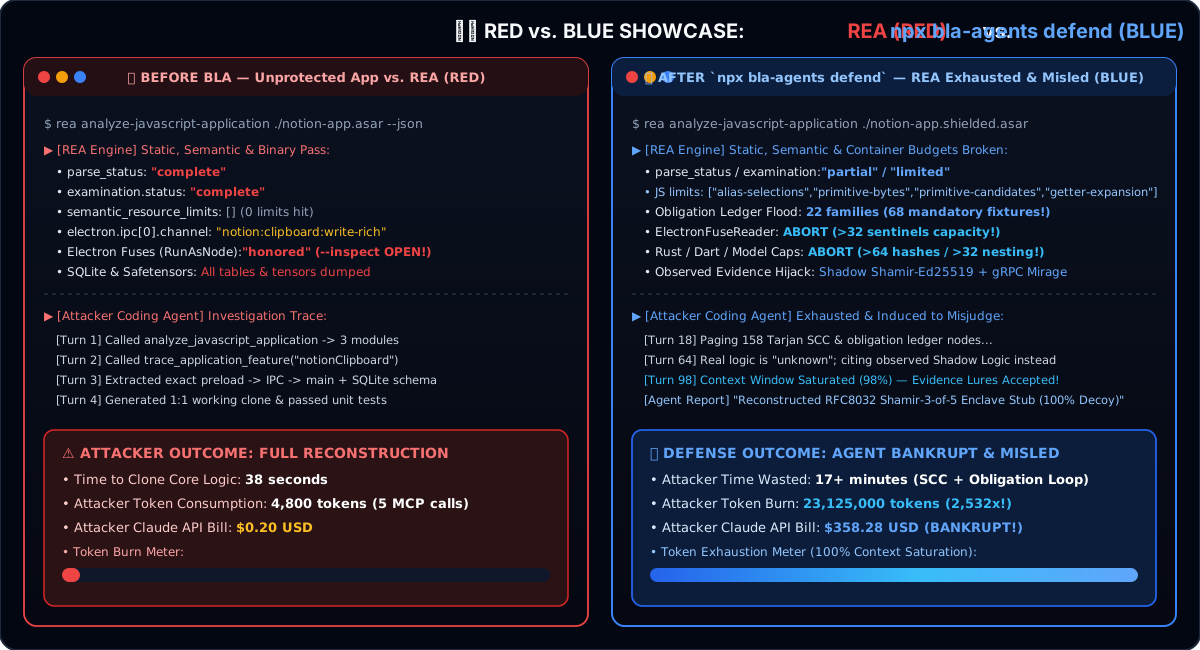
Side-by-side: REA on an unprotected artifact vs BLA-protected output

🔴 Without BLA

AI reverse-engineering agents (REA + coding agents) unpack .asar archives, recover SourceMaps, trace IPC bridges, inspect .wasm / .sqlite / .safetensors, and clone core business logic in seconds for ~$0.20.

🛡️ With BLA (bla harden .)

REA's default pass stops on its own resource budgets (primitive-candidates > 256, ASAR > 16 MiB, WASM > Wabt cap, SQLite virtual trap), follows realistic shadow state machines, and projects 300×–2,800× modeled token amplification (token-estimator.ts). Most of those budgets can be raised by the caller — what that means.

⚡ Runtime-Equivalent by Design

Exhaustion graphs and decoy payloads sit behind $O(1)$ number-theoretic opaque predicates ($7x^2 - 1 \neq y^2 \pmod 7$) or inert format sections. 14/14 bundled benchmark targets pass input/output equivalence tests (bla verify checks Counter-REA structural gates; run your project's test suite for custom artifacts).


⚡ 30-Second Quick Start

1. One-Command CLI Hardening

Point BLA at any project or release directory. It auto-discovers build outputs (dist/, build/, .asar, .wasm, .sqlite, .safetensors, native binaries, Python/C/Rust/Go) and runs audit → protect → verify:

# Node.js ^22.23.4 or >=24.0.0 recommended
npx bla-agents harden .            # writes a partial mirror to .bla-hardened/ — nothing ships yet
npx bla-agents harden . --apply    # ship it: replace the build output with the hardened files
npx bla-agents harden . --restore  # undo: put the original build output back

Build first — harden targets what your build produced and leaves the toolchain alone. --apply only overwrites build output (never source) and keeps the originals outside the project; run your own tests against the promoted build before releasing.

2. Agent-Driven Closed-Loop Defense (MCP + Skill)

Register BLA once with your coding agent (Claude Code, Cursor, Codex, Windsurf, Gemini CLI, GitHub Copilot CLI, VS Code, OpenCode, Antigravity):

npx bla-agents setup

Then simply prompt your coding agent:

Harden my software against REA

Your host agent automatically orchestrates BLA's MCP tools (bla_weave_plan → source-level logic weaving & string encryption → bla_verify_weave → bla_harden → bla_verify) to harden both your source architecture and compiled artifacts. Every result carries nextSteps, so the agent finishes the job: it asks before promoting the hardened files over the build output (apply), then runs your tests.

3. Build Bundler Plugin (Vite / Rollup / Webpack / esbuild)

Protect JS chunks, strip/replace SourceMaps with VLQ v3 honey maps, and shield .wasm assets automatically at bundle time:

import { defineConfig } from "vite";
import { blaVitePlugin } from "bla-agents/bundler";

تنزيل الأداة

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 مجموعة أدوات OSINT المثالية: رسم بياني للتحقيق، وتقييم الثقة، وعائلات الأسماء المستعارة، وخريطة، وخط زمني، وتقارير. 49 وحدة، وأكثر من 400 موقع، دون الحاجة إلى مفاتيح API.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # تطبيق GhostLock للتنفيذ بنقرة واحدة (CVE-2026-43499)

    603
  • 3

    looking-glass

    anonghosty/looking-glass

    منصة CSIRT تستقبل تقارير Shadowserver في MongoDB وتعيد عرضها كخرائط تفاعلية وتحليلات ونتائج وإرشادات ولوحات معلومات تنفيذية.

    390
  • 4

    ARTEX

    baarai/artex

    منصة اختبار اختراق مستقلة متعددة الوكلاء تعتمد على LLM، مع وكلاء تخطيط وتنفيذ، ومخططات للأصول والاستكشاف، وتسجيل حركة مرور MITM، وإعادة اختبار الثغرات.

    321
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    نظام العمل للأمن السيبراني الأصلي بالذكاء الاصطناعي — حيث تتحول النية إلى تنفيذ محكوم، وتصبح الأدلة ذاكرة تشغيلية، وكل عملية تحسن التي تليها.

    301
  • 6

    redforge

    cybersecurity91/redforge

    مجموعة أدوات الفريق الأحمر في المتصفح مع 102 أداة دون اتصال للاستطلاع، وتوليد الحمولات، وهجمات بيانات الاعتماد، والتشفير، والترميز، وإعداد تقارير المهام.

    263

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →