 hakky54/certificate-ripper
🔐 A CLI tool to extract server certificates


A CLI tool to extract server certificates
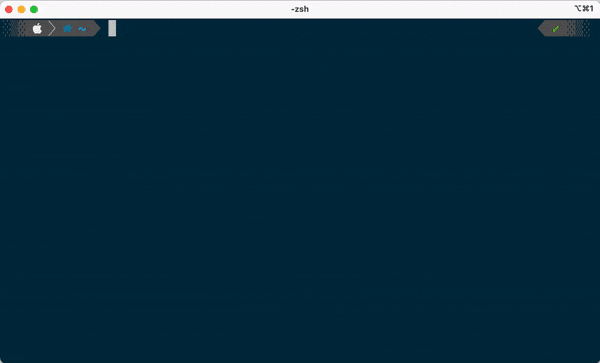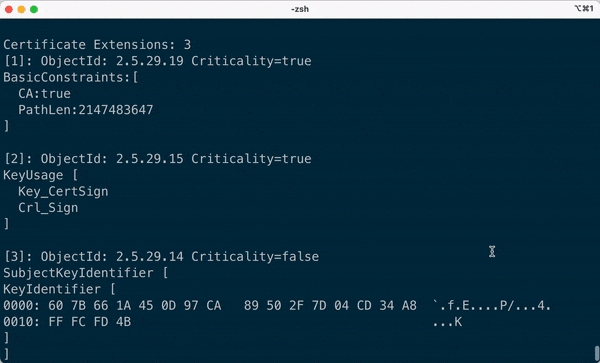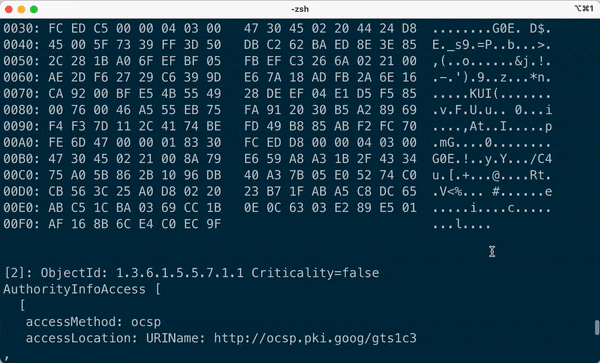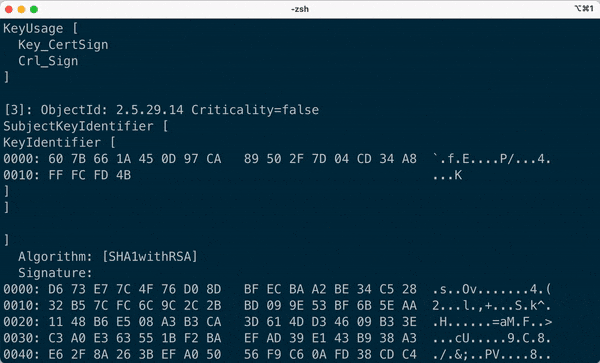
The executables are available for download in the Releases. Alternatively you can also install the tool using one of the following methods:
brew install cripbrew install hakky54/homebrew-apps/cripsudo add-apt-repository ppa:hakky554/apps && sudo apt update && sudo apt-get install crip -t 'o=LP-PPA-hakky554-apps'nix-shell -p certificate-ripper or add pkgs.certificate-ripper to your configuration.nix filechoco install cripscoop install extras/cripMinimum requirements:
Additional OS specific requirements
sudo apt-get update && sudo apt-get install build-essential libz-dev zlib1g-dev -yxcode-select --installchcp 65001 (UTF-8 encoding) is active in the command linemvn clean install -Pnative-image \
&& ./target/crip print --url=https://youtube.com/
The os native executable binary will be available under the target directory having the file name crip
Minimum requirements:
mvn clean install -Pfat-jar \
 && java -jar target/crip.jar print --url=https://youtube.com/
The fat jar will be available under the target directory having the file name crip.jar
Usage: crip [COMMAND]
Commands:
  print             Prints the extracted certificates to the console
  export p12        Export the extracted certificate to a PKCS12/p12 type truststore
  export jks        Export the extracted certificate to a JKS (Java KeyStore) type truststore
  export der        Export the extracted certificate to a binary form also known as DER
  export pem        Export the extracted certificate to a base64 encoded string also known as PEM

Usage: crip print
Prints the extracted certificates to the console
  -f, --format              To be printed certificate format. This option is not required. Default is human-readable.
  -u, --url                 Url of the target server to extract the certificates. Can be provided multiple times.

Usage: crip export pkcs12
Export the extracted certificate to a PKCS12/p12 type truststore
  -u, --url                 Url of the target server to extract the certificates. Can be provided multiple times.
  -p, --password            TrustStore password. This option is not required. Default is changeit.
  -d, --destination         Destination of the to be stored file. Default is current directory if none is provided.

Usage: crip export der
Export the extracted certificate to a binary form also known as DER
  -u, --url                 Url of the target server to extract the certificates. Can be provided multiple times.
  -c, --combined            Indicator to either combine all of the certificate into one file for a given url or export into individual files.
  -d, --destination         Destination of the to be stored file. Default is current directory if none is provided.

Usage: crip export pem
Export the extracted certificate to a base64 encoded string also known as PEM
  -u, --url                 Url of the target server to extract the certificates. Can be provided multiple times.
  -c, --combined            Indicator to either combine all of the certificate into one file for a given url or export into individual files.
  -d, --destination         Destination of the to be stored file. Default is current directory if none is provided.
      --include-header      Indicator to either omit or include additional information above the BEGIN statement.

Other additional options applicable for all commands
      --proxy-host          Proxy host
      --proxy-port          Proxy port
      --proxy-password      Password for authenticating the user for the given proxy
      --proxy-user          User for authenticating the user for the given proxy
  -t, --timeout             Amount of milliseconds till the ripping should timeout
      --resolve-ca          Indicator to automatically resolve the root ca. Possible options: true, false
      --resolve-siblings    Indicator to automatically resolve the certificates from DNS names. Possible options: true, false
      --cert-type           To be extracted certificate types. Available Formats: root, inter, leaf, all. Default: all
crip export pkcs12 -u=https://github.com
crip export pkcs12 \
-u=https://youtube.com \
-u=https://github.com \
-u=https://stackoverflow.com \
-u=https://facebook.com
crip export pkcs12 -u=https://github.com -d=/path/to/directory
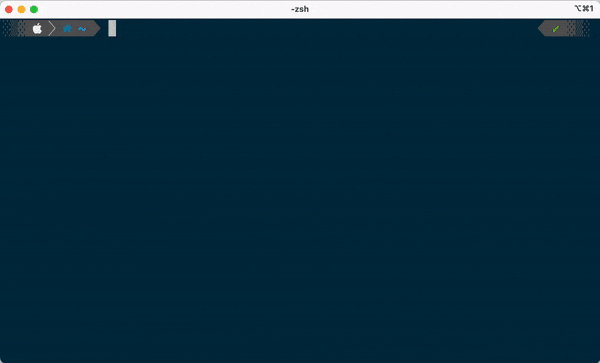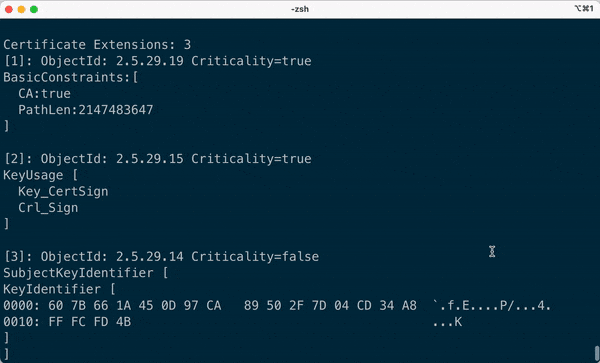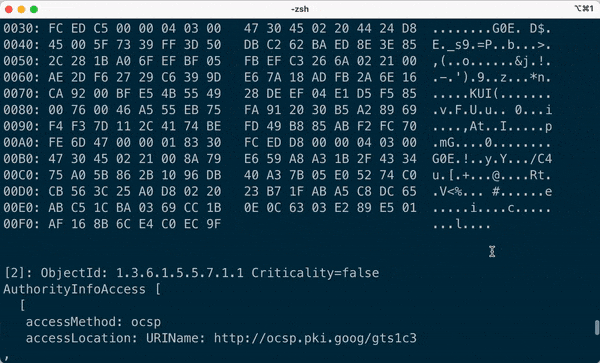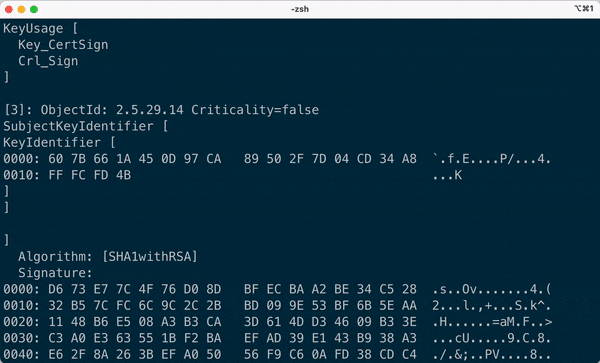
crip print -u=https://github.com
crip print -u=https://github.com -f=pem
