

الماسح الضوئي التكراري للإنترنت للقراصنة. 🧡




https://github.com/blacklanternsecurity/bbot/assets/20261699/e539e89b-92ea-46fa-b893-9cde94eebf81
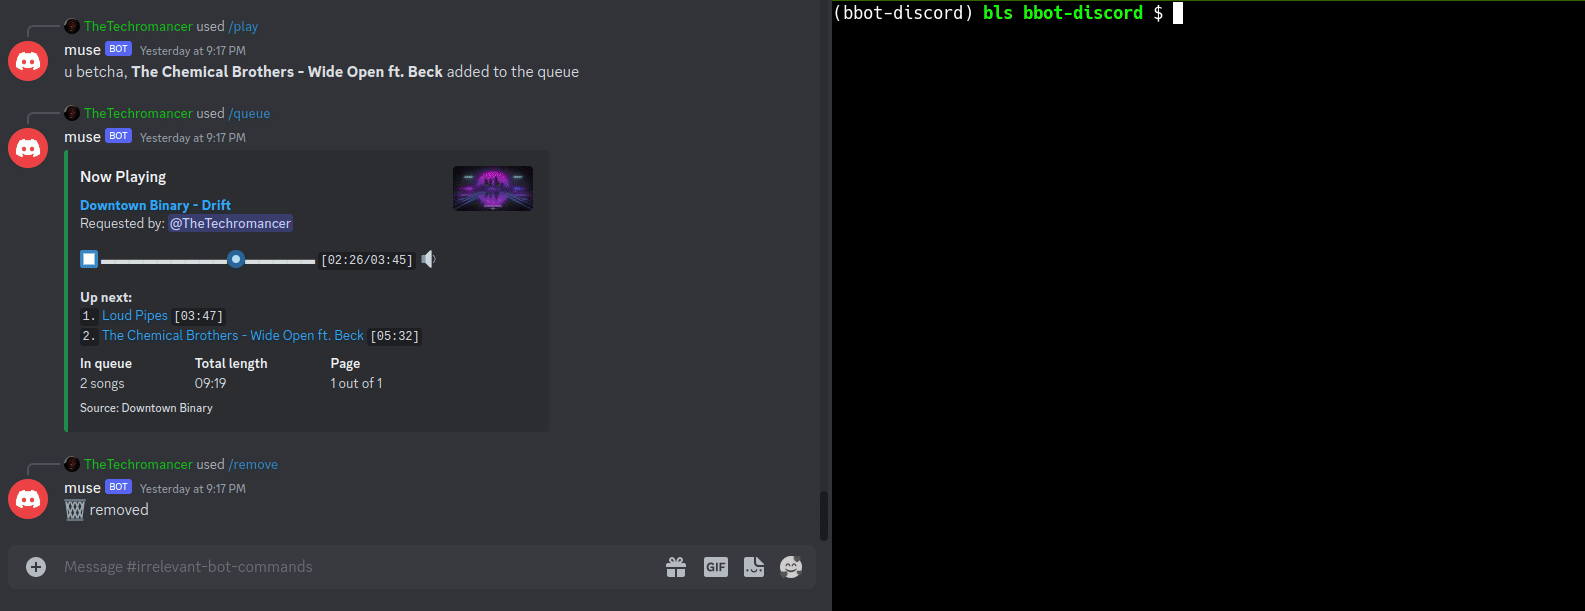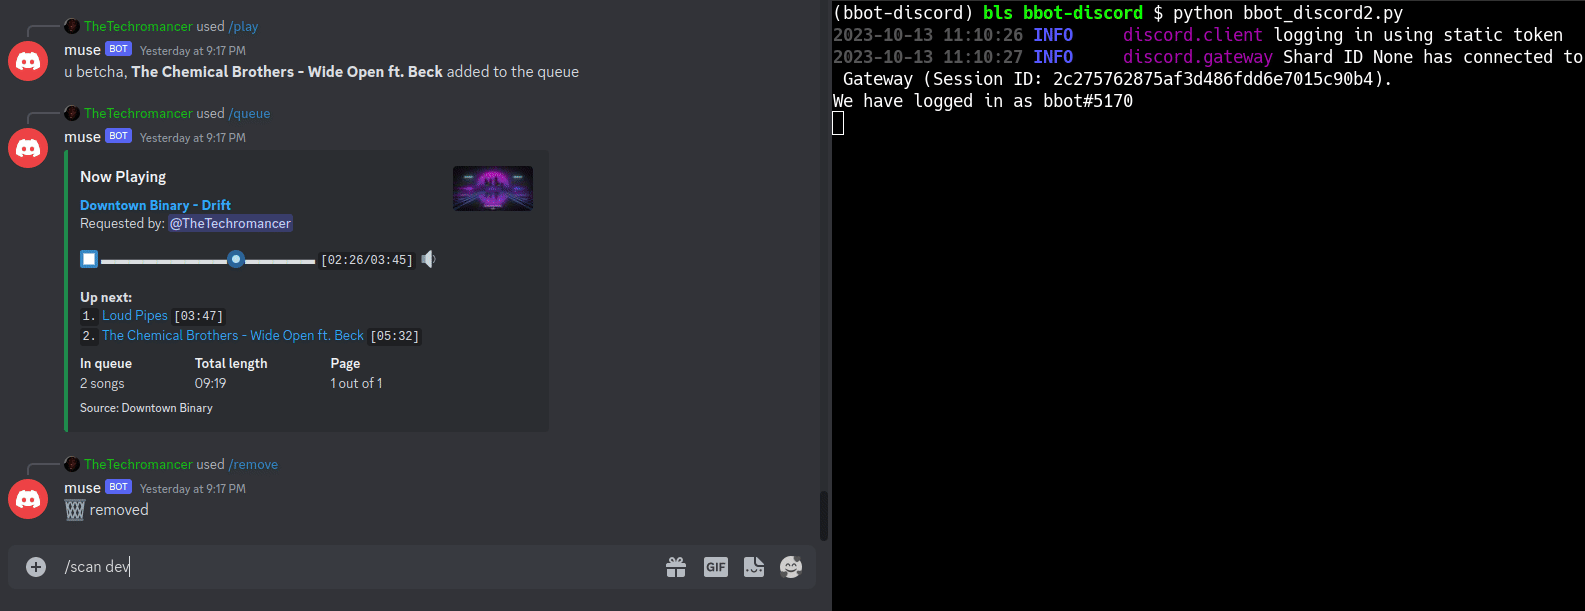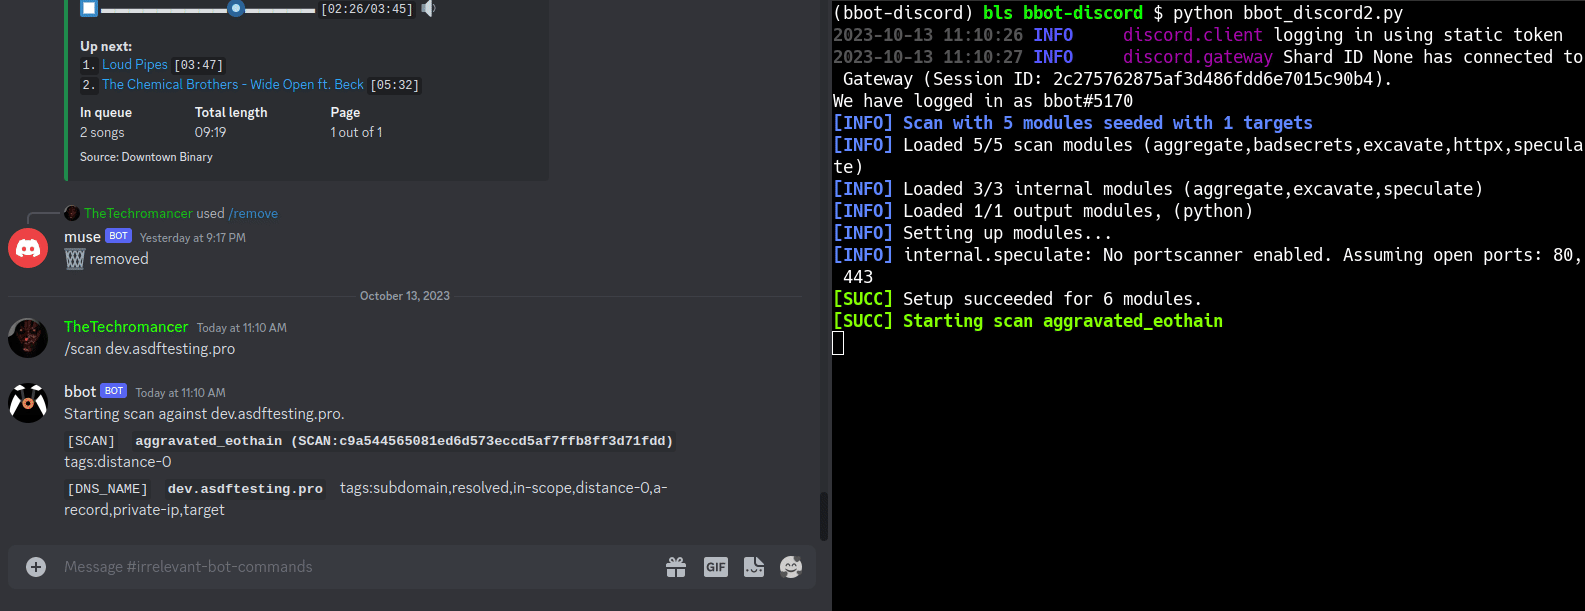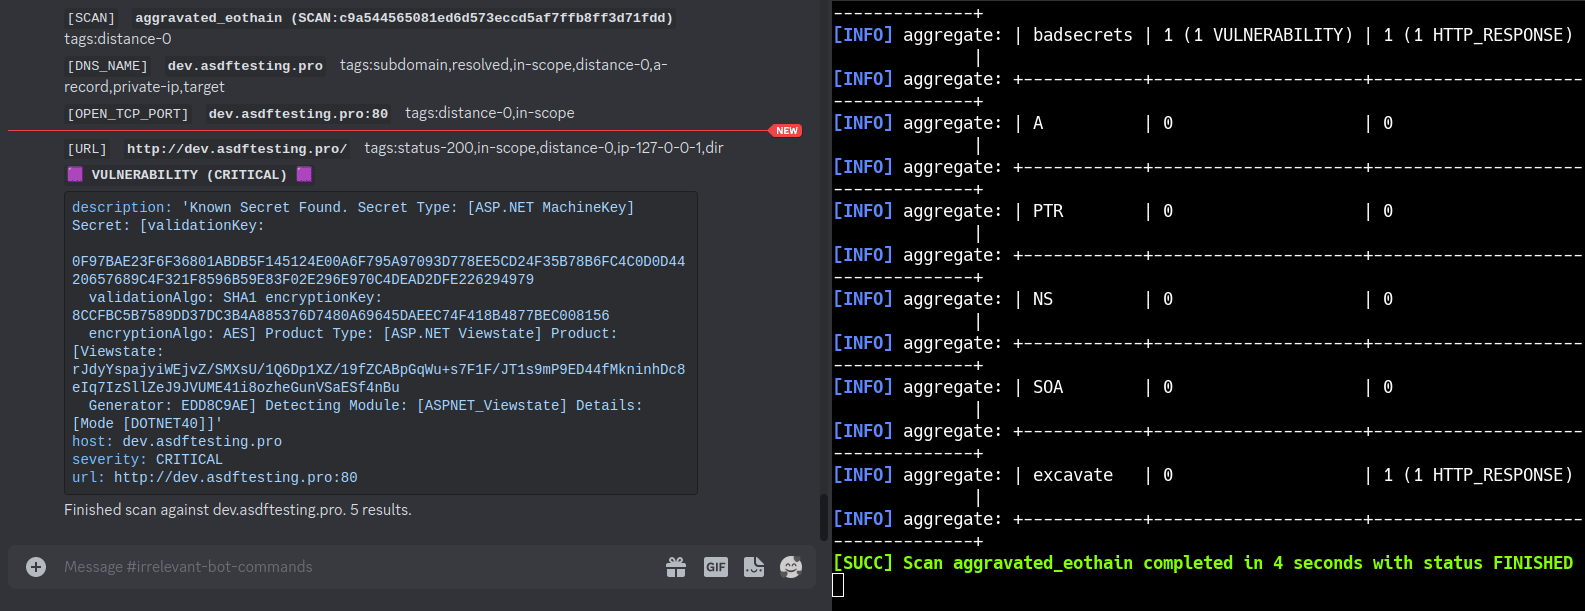
فحص BBOT في الوقت الفعلي - تصوّر بياني باستخدام VivaGraphJS
# stable version
pipx install bbot

# bleeding edge (dev branch)
pipx install --pip-args '\--pre' bbot
لمزيد من طرق التثبيت، بما في ذلك Docker، راجع البدء
هل تقوم بالترقية من 2.x؟ يحتوي BBOT 3.0 على تغييرات جذرية (breaking changes) في واجهة سطر الأوامر (CLI) والإعدادات المسبقة والوحدات والأحداث وواجهة Python البرمجية. راجع دليل الترحيل من 2.x إلى 3.0 (المصدر) قبل الترقية.
نصيحة للأداء: محلل DNS الخاص بـ BBOT (blastdns) يشغّل عدة خيوط (threads) لكل محلل في
/etc/resolv.conf. إضافة المزيد من المحللات غير المفلترة يسرّع عمليات الفحص بشكل كبير. راجع نموذج resolv.conf والنصائح والحيل للتفاصيل.
مصادر API سلبية بالإضافة إلى هجوم تخميني متكرر على DNS (brute-force) مع تحويرات نطاقات فرعية مخصصة للهدف.
# find subdomains of evilcorp.com
bbot -t evilcorp.com -p subdomain-enum

# passive sources only
bbot -t evilcorp.com -p subdomain-enum -rf passive
subdomain-enum.ymldescription: Enumerate subdomains via APIs, brute-force
flags:
# enable every module with the subdomain-enum flag
- subdomain-enum
output_modules:
# output unique subdomains to TXT file
- subdomains
config:
dns:
threads: 25
brute_threads: 1000
# put your API keys here
# modules:
# github:
# api_key: ""
# chaos:
# api_key: ""
# securitytrails:
# api_key: ""
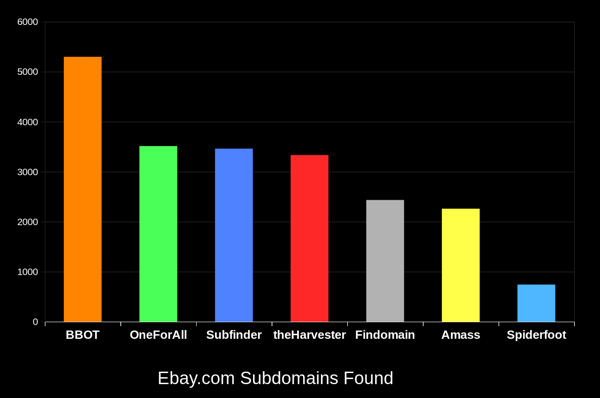
يجد BBOT باستمرار نطاقات فرعية أكثر بنسبة 20-50% من الأدوات الأخرى. وكلما كان النطاق أكبر، كان الفارق أكبر. لمعرفة كيف يكون ذلك ممكنًا، راجع كيف يعمل.
# crawl evilcorp.com, extracting emails and other goodies
bbot -t evilcorp.com -p spider
spider.ymldescription: Recursive web spider
modules:
- http
blacklist:
# Prevent spider from invalidating sessions by logging out
- "RE:/.*(sign|log)[_-]?out"
config:
web:
# how many links to follow in a row
spider_distance: 2
# don't follow links whose directory depth is higher than 4
spider_depth: 4
# maximum number of links to follow per page
spider_links_per_page: 25
# quick email enum with free APIs + scraping
bbot -t evilcorp.com -p email-enum

# pair with subdomain enum + web spider for maximum yield
bbot -t evilcorp.com -p email-enum subdomain-enum spider
email-enum.ymldescription: Enumerate email addresses from APIs, web crawling, etc.
flags:
- email-enum
output_modules:
- emails
# run a light web scan against www.evilcorp.com
bbot -t www.evilcorp.com -p web

# run a heavy web scan against www.evilcorp.com
bbot -t www.evilcorp.com -p web-heavy
web.ymldescription: Quick web scan
include:
- iis-shortnames
flags:
- web
web-heavy.ymldescription: Aggressive web scan
include:
# include the web preset
- web
flags:
- web-heavy
# everything everywhere all at once
bbot -t evilcorp.com -p kitchen-sink

# roughly equivalent to:
bbot -t evilcorp.com -p subdomain-enum cloud-enum code-enum email-enum spider web paramminer webbrute web-screenshots
kitchen-sink.ymldescription: Everything everywhere all at once
include:
- subdomain-enum
- cloud-enum
- code-enum
- email-enum
- spider
- web
- paramminer
- webbrute
- web-screenshots
- baddns-heavy
config:
modules:
dnsbrute:
recursive_mutations: true
dnscommonsrv:
recursive_mutations: true
webbrute:
avoid_wafs: False
wayback:
urls: True
parameters: True
archive: True
انقر على الرسم البياني أدناه لاستكشاف الآلية الداخلية لـ BBOT.