
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
22 results
RDPHijack-BOF preview

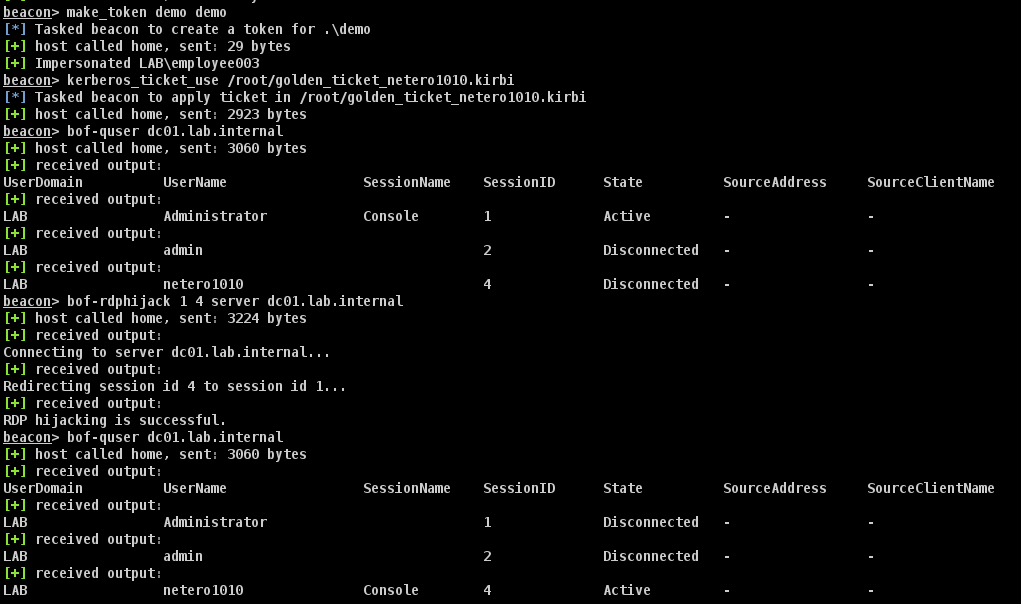
RDPHijack-BOF

GitHubnetero1010/rdphijack-bof

Cobalt Strike Beacon Object File (BOF) that uses WinStationConnect API to perform local/remote RDP session hijacking.
exploit-frameworkslateral-movementpenetration-testing+2
3184 years ago
FindObjects-BOF preview

FindObjects-BOF

GitHuboutflanknl/findobjects-bof

A Cobalt Strike Beacon Object File (BOF) project which uses direct system calls to enumerate processes for specific loaded modules or process handles.
command-and-controlpenetration-testingpost-exploitation+1
2733 years ago
injectAmsiBypass preview

injectAmsiBypass

GitHubboku7/injectamsibypass

Cobalt Strike BOF - Bypass AMSI in a remote process with code injection.
exploit-frameworkspayload-developmentpenetration-testing+1
3793 years ago
CVE-2026-49176_BOF preview

CVE-2026-49176_BOF

GitHub777erp/cve-2026-49176_bof

CVE-2026-49176 WalletService LPE — standalone PoC + Cobalt Strike BOF (SYSTEM command on interactive session)

exploitationpayload-developmentpost-exploitation+2
51 month ago
lsawhisper-bof preview

lsawhisper-bof

GitHubdazzyddos/lsawhisper-bof

A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…

authenticationcommand-and-controlexploitation+4
2976 months ago
cs-token-vault preview

cs-token-vault

GitHubhenkru/cs-token-vault

In-memory token vault BOF for Cobalt Strike

authentication-authorizationpenetration-testing-frameworkspost-exploitation+2
1514 years ago
amd-ryzen-master-driver-v17-exploit preview

amd-ryzen-master-driver-v17-exploit

GitHubtijme/amd-ryzen-master-driver-v17-exploit

Cobalt Strike (CS) Beacon Object File (BOF) for kernel exploitation using AMD's Ryzen Master Driver (version 17).
binary-exploitationexploitationexploit-frameworks+4
1593 years ago
kernel-mii preview

kernel-mii

GitHubtijme/kernel-mii

Cobalt Strike (CS) Beacon Object File (BOF) foundation for kernel exploitation using CVE-2021-21551.

exploit-frameworkspayload-developmentpenetration-testing+2
853 years ago
WdToggle preview

WdToggle

GitHuboutflanknl/wdtoggle

A Beacon Object File (BOF) for Cobalt Strike which uses direct system calls to enable WDigest credential caching.
exploit-frameworkspost-exploitationred-teaming
2183 years ago
CobaltWhispers preview

CobaltWhispers

GitHubnvisosecurity/cobaltwhispers

CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…

adversarial-attackcommand-and-controlids-ips-evasion+4
2423 years ago
BOF_RunPe preview

BOF_RunPe

GitHubntdallas/bof_runpe

BOF to run PE in Cobalt Strike Beacon without console creation
memory-forensicspost-exploitationred-teaming+1
1999 months ago
CVE-2024-26229-BOF preview

CVE-2024-26229-BOF

GitHubapkc/cve-2024-26229-bof

BOF implementations of CVE-2024-26229 for Cobalt Strike and BruteRatel

binary-exploitationexploitationexploit-frameworks+5
292 years ago
ADSyncDump-BOF preview

ADSyncDump-BOF

GitHubparadoxis/adsyncdump-bof

The ADSyncDump BOF is a port of Dirk-Jan Mollema's adconnectdump.py / ADSyncDecrypt into a Beacon Object File (BOF) with zero dependencies.

cloud-securityencryption-decryption-toolsidentity-access-management+3
1841 year ago
SpawnWith preview

SpawnWith

GitHubrasta-mouse/spawnwith

Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
command-and-controlimpersonation-toolslateral-movement+2
1131 year ago
Elevate-System-Trusted-BOF preview

Elevate-System-Trusted-BOF

GitHubmr-un1k0d3r/elevate-system-trusted-bof

Cobalt Strike Beacon Object File that elevates an active beacon to SYSTEM and grants TrustedInstaller privileges through SetThreadToken token…

command-and-controlpayload-developmentpost-exploitation+2
1813 years ago
CVE-2024-35250-BOF preview

CVE-2024-35250-BOF

GitHubro0tmylove/cve-2024-35250-bof

Cobalt Strike 的 CVE-2024-35250 的 BOF。(请给我加个星,谢谢。)

binary-exploitationexploitationexploit-frameworks+3
131 year ago
Aggressor-Aggregator preview

Aggressor-Aggregator

GitHubgmh5225/aggressor-aggregator

A helper script for consolidating Aggressor and BOF repositories into a single CNA for Cobalt Strike.
penetration-testing-frameworksred-teamingscripting-automation
2 years ago
WindowSpy preview

WindowSpy

GitHubcodextf2/windowspy

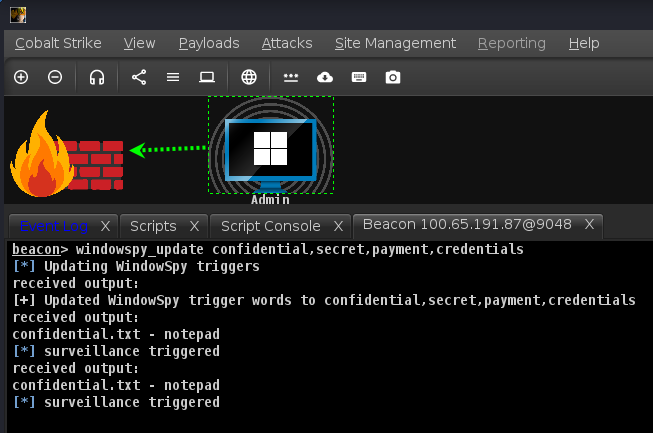
Cobalt Strike Beacon Object File for automated, targeted user surveillance. Triggers screenshots or custom actions when specific window titles (e.g.,…

post-exploitationred-teaming
2871 year ago
Previous12Next