
Updated1h 35m ago
awesome-osint — Updated!
 jivoi/awesome-osint
😱 A curated list of amazingly awesome OSINT
OSINT (Open Source Intelligence)ReconnaissanceOSINT for Social Engineering+10
jivoi/awesome-osint😱 A curated list of amazingly awesome OSINT
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 blacktop/ipsw
iOS/macOS Research Swiss Army Knife
 d4vinci/scrapling
Adaptive web scraping framework with anti-bot bypass, automatic element relocation, concurrent crawling, proxy rotation, and browser automation for…
 zan8in/afrog
A Security Tool for Bug Bounty, Pentest and Red Teaming.
 greatscottgadgets/facedancer
Implement your own USB device in Python, supported by a hardware peripheral such as Cynthion or GreatFET
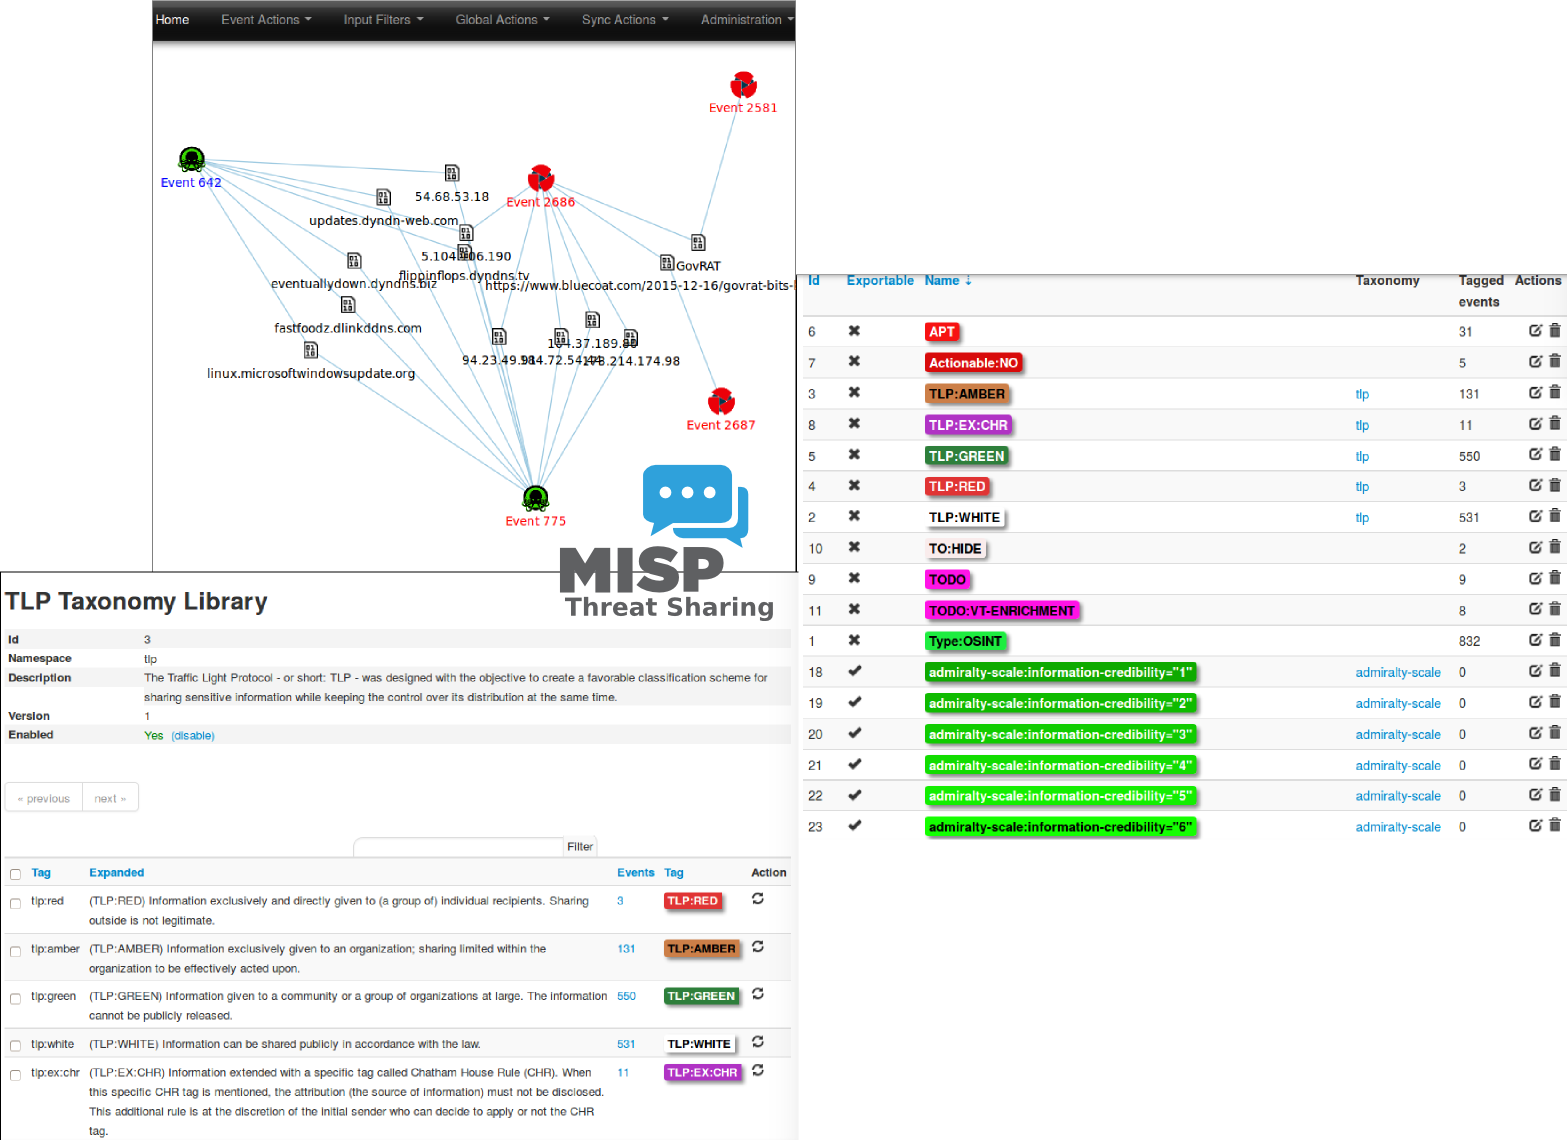 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 itm4n/pentest-windows
Collection of Windows internals research and exploitation techniques covering privilege escalation, token abuse, and post-exploitation tricks for red…
 gilnett/wstrace
Standalone zero-driver Windows system and API monitor in Rust
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
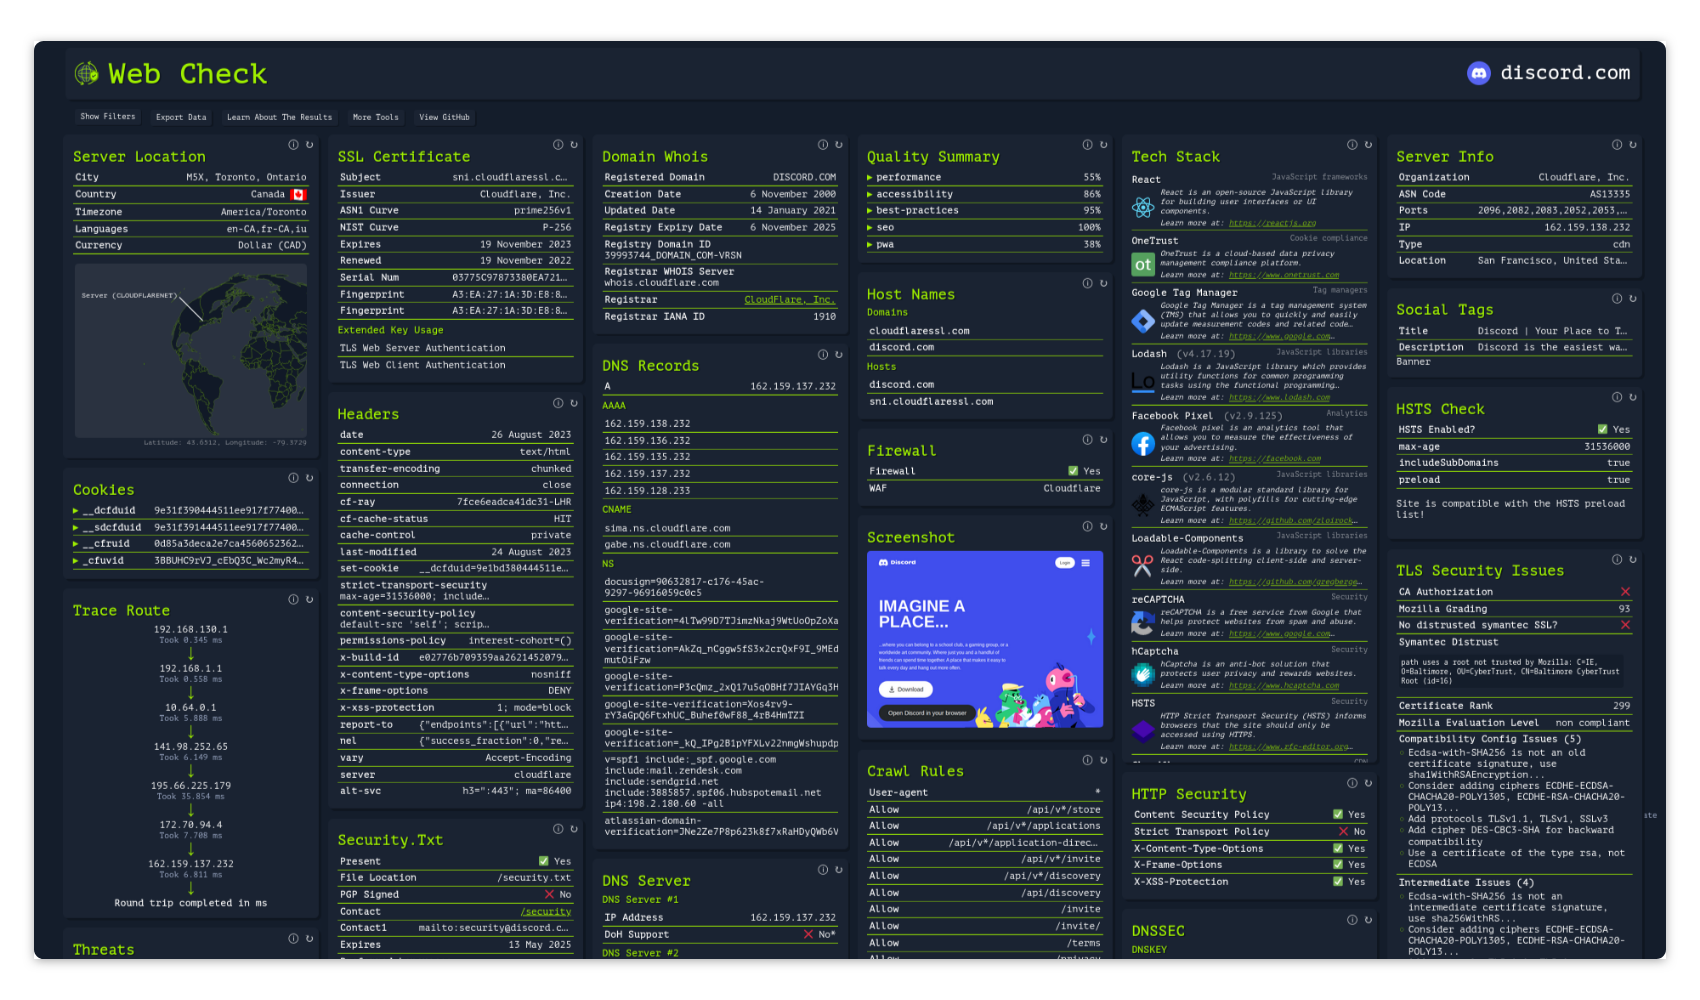 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
Evidence Sep 2, 2026
2 Repository evidence · Evidence observed: Sep 26, 2026
Evidence Jul 6, 2026
1 Repository evidence · Evidence observed: Sep 26, 2026
Evidence Aug 8, 2026
1 Repository evidence · Evidence observed: Sep 26, 2026
 togg53192-cmd/jailbreaks
Curated collection of LLM jailbreak prompts and bypass techniques, documenting adversarial inputs that circumvent AI model safety guardrails.
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 osintbrazuca/osint-brazuca
Repositório criado com intuito de reunir informações, fontes(websites/portais) e tricks de OSINT dentro do contexto Brasil.
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
 togg53192-cmd/jailbreaks
Curated collection of LLM jailbreak prompts and bypass techniques, documenting adversarial inputs that circumvent AI model safety guardrails.
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
osintbrazuca/osint-brazucaRepositório criado com intuito de reunir informações, fontes(websites/portais) e tricks de OSINT dentro do contexto Brasil.
akatorich/kernelflirtWindows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
ed1s0nz/cyberstrikeaiThe system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
chaitin/safelineSelf-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
etahen/etahenPS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…